# Welcome to Catchify

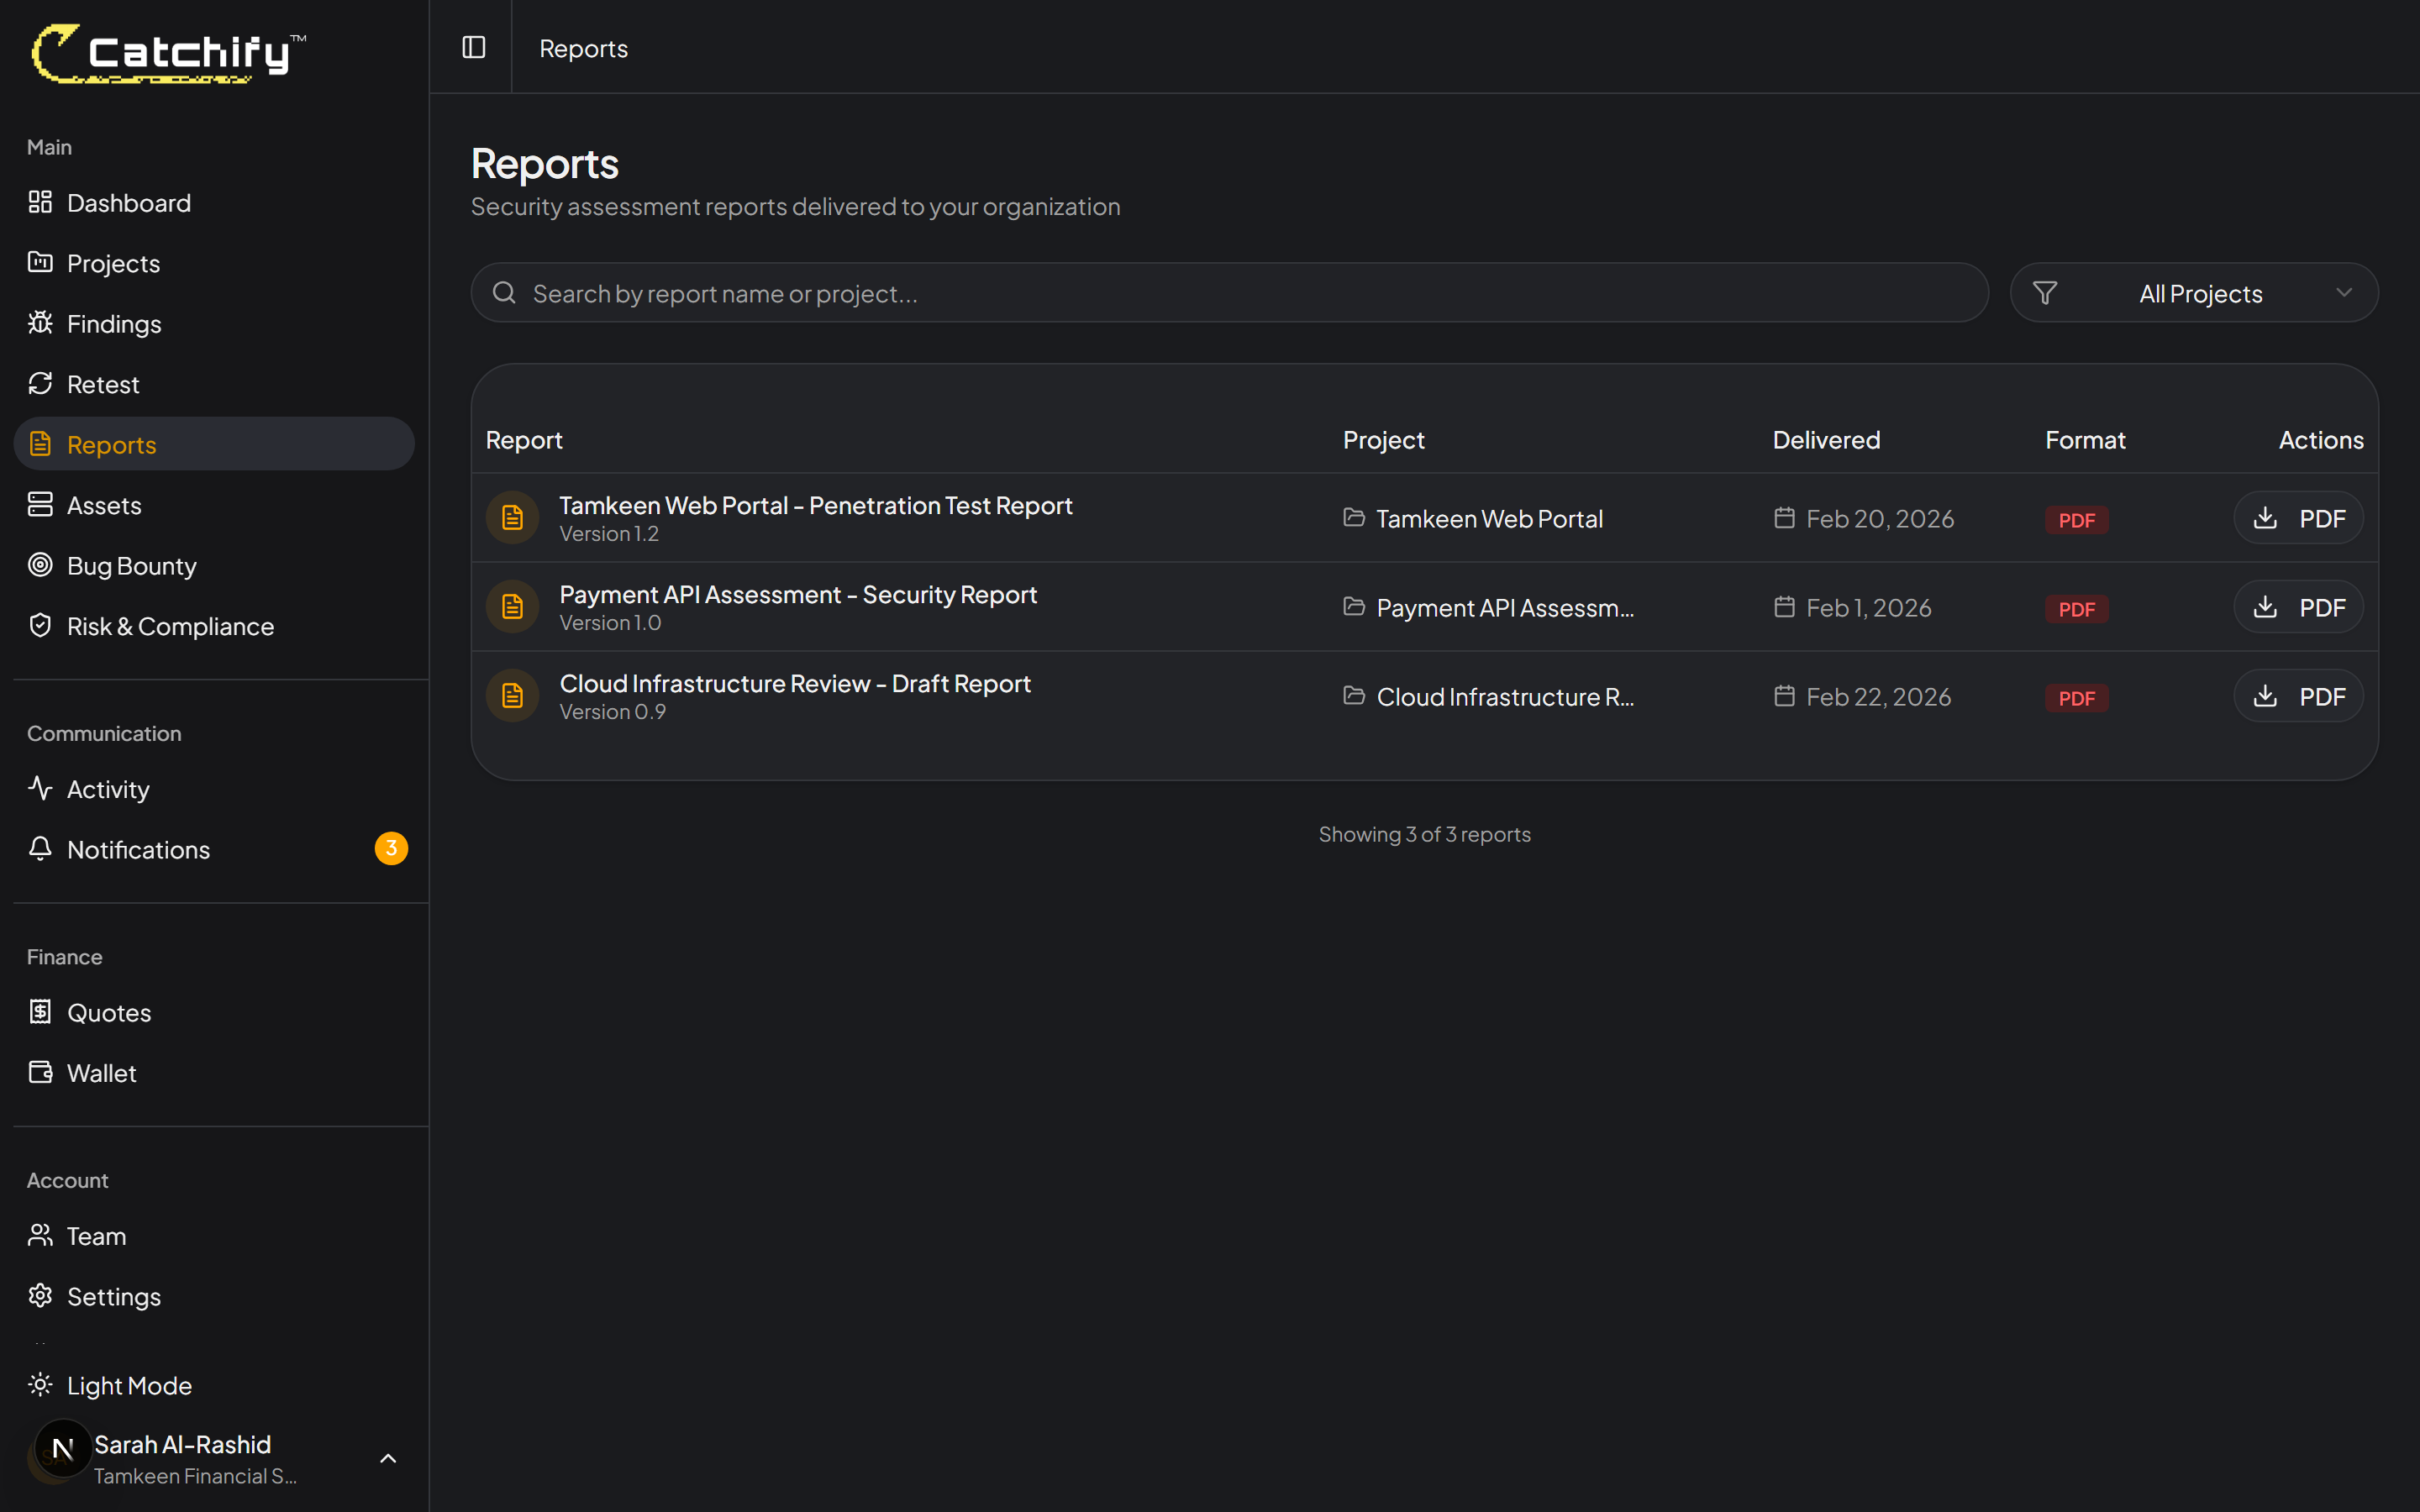
Welcome to the Catchify Client Portal! This documentation is designed to help you confidently navigate our platform and take full advantage of our Penetration Testing as a Service (PTaaS) offering.

### 🚀 Our Mission

At **Catchify**, our mission is simple:\
**We aim to automate penetration testing and deliver the highest impact for your organization.**

We believe in reducing noise, accelerating response times, and giving you full control and visibility over your security testing process, all in one secure, easy-to-use platform.

### 📘 What You’ll Find Here

* How to set up your account and company profile
* How to manage users, assets, and contacts
* How to request, track, and manage pentests
* How to review and respond to security findings
* Tips for collaborating with your pentesters in real time

Whether you're a security lead, a developer, or a compliance officer, this guide will walk you through everything you need to know.

***

Let’s get started. You’re in good hands!


# Quickstart

At this Quickstart we will outline the setup for your account at Catchify.

## ⚡ Quickstart

This Quickstart guide helps you configure your Catchify environment in just a few steps.

### 🚀 Steps to Get Started

1. **Activate your account**\
   Check your inbox for an invite and follow the instructions to set up your password.
2. **Set up your company profile**\
   Go to Settings → Company Info and enter your business details.
3. **Add your team members**\
   Invite developers, managers, or anyone who needs access to the portal.
4. **Add your assets**\
   Register websites, APIs, or systems you want to manage under your account.

***

Once these steps are done, your workspace is ready.


# Account Setup

Setting up an account for your company.

You can join Catchify through an email invite sent by us through. The setup process is very straightforward.

Your company account will be created. Once that’s done, an **Admin User** will be configured, and you'll receive an invitation email to activate your access.

### ✅ To get started:

1. Click "**Verify"** in your email invite
2. Sign in using your email and temporary password
3. You may be prompted to **change your password**

That’s it, you now have full access to the Catchify Client Portal.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FTu3NOKWLNFJeB0iCZC6v%2Fimage.png?alt=media&amp;token=fb8fc1f6-b1a7-47b0-b3f1-718a9b9a3a02" alt=""><figcaption><p>The Portal</p></figcaption></figure>


# Editing Company Information

Edit Your Information

## 🏢 Editing Company Information

Company information is used to define your organization for reporting, and administrative purposes. This includes your registered business name, address, and contact details.

When your Catchify account is created, your assigned security engineer may prefill this data. However, you can edit it at any time by navigating to your **Settings**.

### ✏️ To edit your company details:

1. From the left-hand menu, click **Settings**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FLfjweEdVb6fSkuoxQcXM%2Fimage.png?alt=media&amp;token=bafbb73d-f854-43f1-b8ed-8b2b0121c904" alt=""><figcaption></figcaption></figure>

2. Select **Company Info**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FDdzIPTkHciL7p8yNrXfZ%2Fimage.png?alt=media&amp;token=cdef4f99-afb6-491e-ac87-b00e0cc153c5" alt=""><figcaption></figcaption></figure>

3. Click the **Edit** button in the top-right section of the page

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FodGsl71x3FDeJO3cU7uR%2Fimage.png?alt=media&amp;token=f3c22cd8-0098-4768-9284-079601dc4758" alt=""><figcaption></figcaption></figure>

4. Fill in or update your company details:

* Company Name
* Website
* Street
* Postal Code
* City
* Country

***

You can also manage your contacts here.


# Adding Users

Add the users.

Users include everyone involved in your Catchify workspace, administrators, stakeholders, developers, or anyone managing findings and remediation. It’s recommended to add all key users early in your setup process.

1. Click **Settings** in the left-hand menu

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FDi0feivLpXqcubRmvvL9%2Fimage.png?alt=media&amp;token=eeb0ac8d-d6bb-4f54-b94f-c4d4cd6c162a" alt=""><figcaption><p>Settings</p></figcaption></figure>

2. Select **Users**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FxbOoerWBdkIYiQ6uE6Mv%2Fimage.png?alt=media&amp;token=87501a6f-b833-40a4-8ab0-a29c0b68a464" alt=""><figcaption></figcaption></figure>

3. Click the **New User** button in the top-right corner

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F4z5fOZsAdSRbWeYA21sE%2Fimage.png?alt=media&amp;token=6ecca1de-ce8b-43fd-8e89-dc2626a16a15" alt=""><figcaption></figcaption></figure>

4. Fill out the user’s information:

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FR6kzIfnVQBuK0xzFsuRY%2Fimage.png?alt=media&amp;token=222d7b46-3044-45d9-898f-611a3346f42e" alt=""><figcaption></figcaption></figure>

Name & Surname

* Email address
* Optional: Phone number
* Settings (enable 2FA, location restrictions, account activation)

Once submitted, the new user will receive an email invitation. They'll complete their account setup using the same steps as the admin.


# The Contacts

Contacts in Catchify are stakeholders and key individuals who should receive notifications about project updates, security findings, and audit reports.

To add someone as a contact, they must first be added as a **user** in the system.\
➡️ [Click here to learn how to add users](/portal-guide/quickstart/adding-users)

### 🛠️ How to Set Up Contacts

1. Go to **Settings** in the left-hand menu

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FnO2PlVSBV7HHc6KSsexh%2Fimage.png?alt=media&amp;token=6b78dd17-a5cf-4a15-95a6-c51ec60b1d76" alt=""><figcaption></figcaption></figure>

2. Click on **Company Info**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F1YEhWKURrneHyFEnoHCz%2Fimage.png?alt=media&amp;token=796360d3-aae2-46b7-8b6a-4a5e5315f089" alt=""><figcaption></figcaption></figure>

3. Click the **Edit** button from the top-right section of the form

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fa9VOnnDoSFxcxC9nB0no%2Fimage.png?alt=media&amp;token=31be66b7-497a-4a43-8b13-500ac7318845" alt=""><figcaption></figcaption></figure>

4. In the contact fields, assign the appropriate users to each role:

* **Main** – Typically the administrator and project owner
* **Compliance** – Your compliance officer
* **Technical** – A lead developer or technical owner
* **Finance** – The person handling budgeting or approvals

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F9yw3o6ys00Q16wXF6xUT%2Fimage.png?alt=media&amp;token=2d320d45-0f30-448e-8814-af7532f30943" alt=""><figcaption></figcaption></figure>

These contacts will automatically receive updates:

* When project status changes
* During key phases of the pentest
* Upon completion and during approval workflows


# Adding Assets

Assets define what will be tested during your security engagement, such as websites, APIs, mobile apps, networks, and other critical systems.

Assets represent the scope of your security testing and include websites, APIs, mobile apps, networks, and other systems. It's important to define these before engaging in any pentesting activity.

### 🛠️ How to Add an Asset

1. In the left-hand menu, click **Settings**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fhwy4nDC4zuzDMthAJbTI%2Fimage.png?alt=media&amp;token=3274783c-30e1-454f-98ae-b2e68986c230" alt=""><figcaption><p>Settings</p></figcaption></figure>

2. Select **Assets**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FFeO3UdotP9JbARfU4sod%2Fimage.png?alt=media&amp;token=cb62994e-5619-46df-8cfc-12d3e9c4510e" alt=""><figcaption><p>Assets Selection</p></figcaption></figure>

3. Click the **+ New Asset** button in the top-right

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F9lNuhqU3Oz2tmaey2LvU%2Fimage.png?alt=media&amp;token=16da4bee-9b59-4f69-9c52-f4ecfd88b415" alt=""><figcaption><p>Button For Asset</p></figcaption></figure>

4. Fill out the **Asset Details**:

* **Title** – Must be descriptive and unique

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FMLybO9L1lVaZ2QNnLPt4%2Fimage.png?alt=media&amp;token=a141b335-d68d-49e9-a6c9-f5cba9739564" alt=""><figcaption><p>The title should be unique</p></figcaption></figure>

* **Description** – Example:\
  `Primary website for Catchify, consisting of 20+ pages and multiple subdomains`

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FCXvSBJxoYwebgTekwwLE%2Fimage.png?alt=media&amp;token=932269a5-259b-478b-bc18-8f4472b94a93" alt=""><figcaption></figcaption></figure>

* **Domain** –  `app.catchify.sa`
* **IP Address** – Optional, for IP-based assets
* **Asset Type** – Choose one:
  * Website
  * Web Application
  * Mobile Application
  * API
  * Network
  * Other
* **Hosting Type** – Public Cloud, Private, etc.
* **Environment** – (Production, Staging)

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F3gI27DAu1ZYtRY4CDJjp%2Fimage.png?alt=media&amp;token=12c181d5-a92d-4fc3-9de0-25182eeeeae9" alt=""><figcaption></figcaption></figure>

5. Click **Save** to register the asset.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fw6BTL7Zyuy62JjOKxUu9%2Fimage.png?alt=media&amp;token=fb290945-fb9f-4b95-83b8-61d9be90826a" alt=""><figcaption><p>Choose scope and save asset</p></figcaption></figure>


# Pentest Management

Manage the entire lifecycle of your security tests, from initiating pentests to tracking findings and retesting, all within Catchify’s automated platform.

The Pentest Management section explains how Catchify helps you plan, request, and track your security tests, all from one place.

With Catchify, you can:

* Launch new pentest requests for specific assets
* Collaborate with security engineers on scope and timelines
* Monitor test progress in real time
* View findings as they're discovered
* Request retesting or follow-up assessments
* Automate recurring testing cycles

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FvCqSSLrkXoexcUFGqQMq%2Fimage.png?alt=media&amp;token=00016d1a-13f5-4c2c-86af-da83b5464081" alt=""><figcaption></figcaption></figure>

Everything is streamlined, no lengthy email threads, no waiting on static reports.

***

This section will walk you through each step of the process.


# How it Works

Understand the full pentest lifecycle in Catchify, from request to kickoff, findings, and retesting, all managed in one streamlined workflow.

Catchify makes it easy to manage penetration testing from start to finish, all within one secure platform.

Here’s how a typical workflow looks:

* You create a new pentest request and select the target assets
* A Catchify engineer reviews the scope and provides a proposed plan
* You approve or request changes to the scope or timeline
* Once approved, the pentest is queued and scheduled
* On the scheduled start date, testing begins
* Your team receives real-time notifications for any discoveries
* You can log in any time to track progress, view reports, and add comments
* Findings are uploaded progressively to your dashboard
* You may request retesting through the platform once fixes are applied
* You can schedule recurring pentests based on your testing cycle

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FGVLma3Quf2u6HmsELw0Z%2Fimage.png?alt=media&amp;token=711b0f2a-d0f9-4f38-ba15-5f524e9958d3" alt=""><figcaption></figcaption></figure>

***

This streamlined process eliminates the need for back-and-forth emails and static reporting.\
Catchify ensures that findings are delivered as **actionable work items,** making remediation faster and more efficient.


# Start A Pentest With Catchify

Follow these steps to submit a new pentest request in Catchify, including template selection, start date, and custom instructions.

Follow these steps to submit a new pentest request:

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FjdgO6ZhffpSIu8Iq0kbe%2Fimage.png?alt=media&amp;token=e5d25a4d-860b-4ad5-876f-ee6d91a53925" alt=""><figcaption><p>Click on Pentests</p></figcaption></figure>

1. **Enter Pentest Information**

* Type a descriptive name for your test (e.g., "Pentest on API")
* Click **Next** to continue

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FSRmTDZWVS6aUx8bmol2B%2FScreenshot_343.png?alt=media&amp;token=8c0909fd-791c-47cd-b0bf-766feca14e89" alt=""><figcaption></figcaption></figure>

<br>

2. **Select the Target Assets**

* Choose the asset(s) you'd like included in the test
* Optionally, click **+ New Asset** to add something new
* Click **Next** when ready

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FDOpBcgMLORRJvtDYsT7K%2F9a52d142-f1e1-44f5-94c8-4d70031d110f.png?alt=media&amp;token=fd27e844-08c5-4eb8-aa2c-77c7a613cdab" alt=""><figcaption></figcaption></figure>

<br>

3. **Confirm and Submit the Request**

* Review the pentest name, selected assets, and any objectives
* If everything looks good, click **Submit request**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fw6nP1nXwp9yamYaRypcA%2Fa789bd23-9bfc-4174-bc3b-8ad6d9d9bc48.png?alt=media&amp;token=b7ca2c8e-b748-440a-a2b4-48db56d647fe" alt=""><figcaption><p>Submitting A Request</p></figcaption></figure>

***

Once submitted, the request will be reviewed by the Catchify team.


# What Next After Requesting A Pentest

Learn what happens after you submit a pentest request, from review and proposal to approval and scheduling.

After submitting your pentest request in Catchify, the following process begins:

1. **Your request is received**\
   Our security team is immediately notified through the platform.
2. **Initial review**\
   We assess your request details, scope, and selected assets. Review time may vary depending on the complexity of the engagement.
3. **Quote sent**\
   You’ll receive a budget estimate and timeline proposal. You can approve it as-is or work with the Catchify engineer to adjust it.
4. **Approval & next steps**\
   Once approved, the pentest is scheduled. You'll be notified when kickoff is confirmed.

***

➡️ Click here to understand Pentest Statuses


# Pentest Statuses

This is your guide to understand your pentest status.

You can track every pentest in Catchify using status labels. Each status reflects the current stage of the engagement and who is responsible for the next action.

* **Requested** – You’ve submitted a request and are discussing the scope, timeline, and budget
* **Quoted** – Catchify has reviewed your request and shared a proposal including cost, testing duration, and start availability

  > You can approve the quote, suggest changes, or hold off until you're ready
* **Scheduled** – The pentest has been approved and is locked in to begin on a specific date
* **Onboarding** – Project kickoff begins. Asset access, permissions, and environment handoff take place
* **In Progress** – The pentest is underway. You’ll receive updates as findings are discovered
* **Remediation** – Findings are delivered. Your team can begin remediation and request retesting
* **Offboarding** – Final review, report handoff, and scheduling for future tests
* **Done** – The pentest is complete and closed
* **Canceled** – The request or project was canceled before or during execution

***

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FLfvd9V3SrTd0DfuBQ4Ik%2Fimage.png?alt=media&amp;token=a96a3ef5-a18d-4328-b02c-71121110cee1" alt=""><figcaption><p>Status</p></figcaption></figure>


# Findings Management

View, track, and manage all reported findings in one place, with filters for severity, status, and assignment to streamline remediation.

This section gives you full visibility into all vulnerabilities discovered across your pentests.

You can:

* View findings by severity, status, and asset
* Track which issues are still open or have been resolved
* Assign findings to your team for remediation
* Monitor updates and retesting outcomes

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FDxVZ30PMGBODHXEeCSea%2FScreenshot_77%20(1).png?alt=media&amp;token=5659309f-5a65-4722-82d0-321aa10c1df6" alt=""><figcaption><p>Findings Dashboard</p></figcaption></figure>

***

Findings Management helps your team stay aligned and take action faster through a clear, centralized view of all findings.


# View Findings

Learn how to access, filter, and sort findings across your pentests using the Catchify dashboard or individual project views.

Findings in Catchify can be accessed from three places:\
the **Findings** tab, the **Pentest** view, and the **Dashboard**.

***

### 📁 From Findings Management

1. Go to **Findings** in the left-hand menu

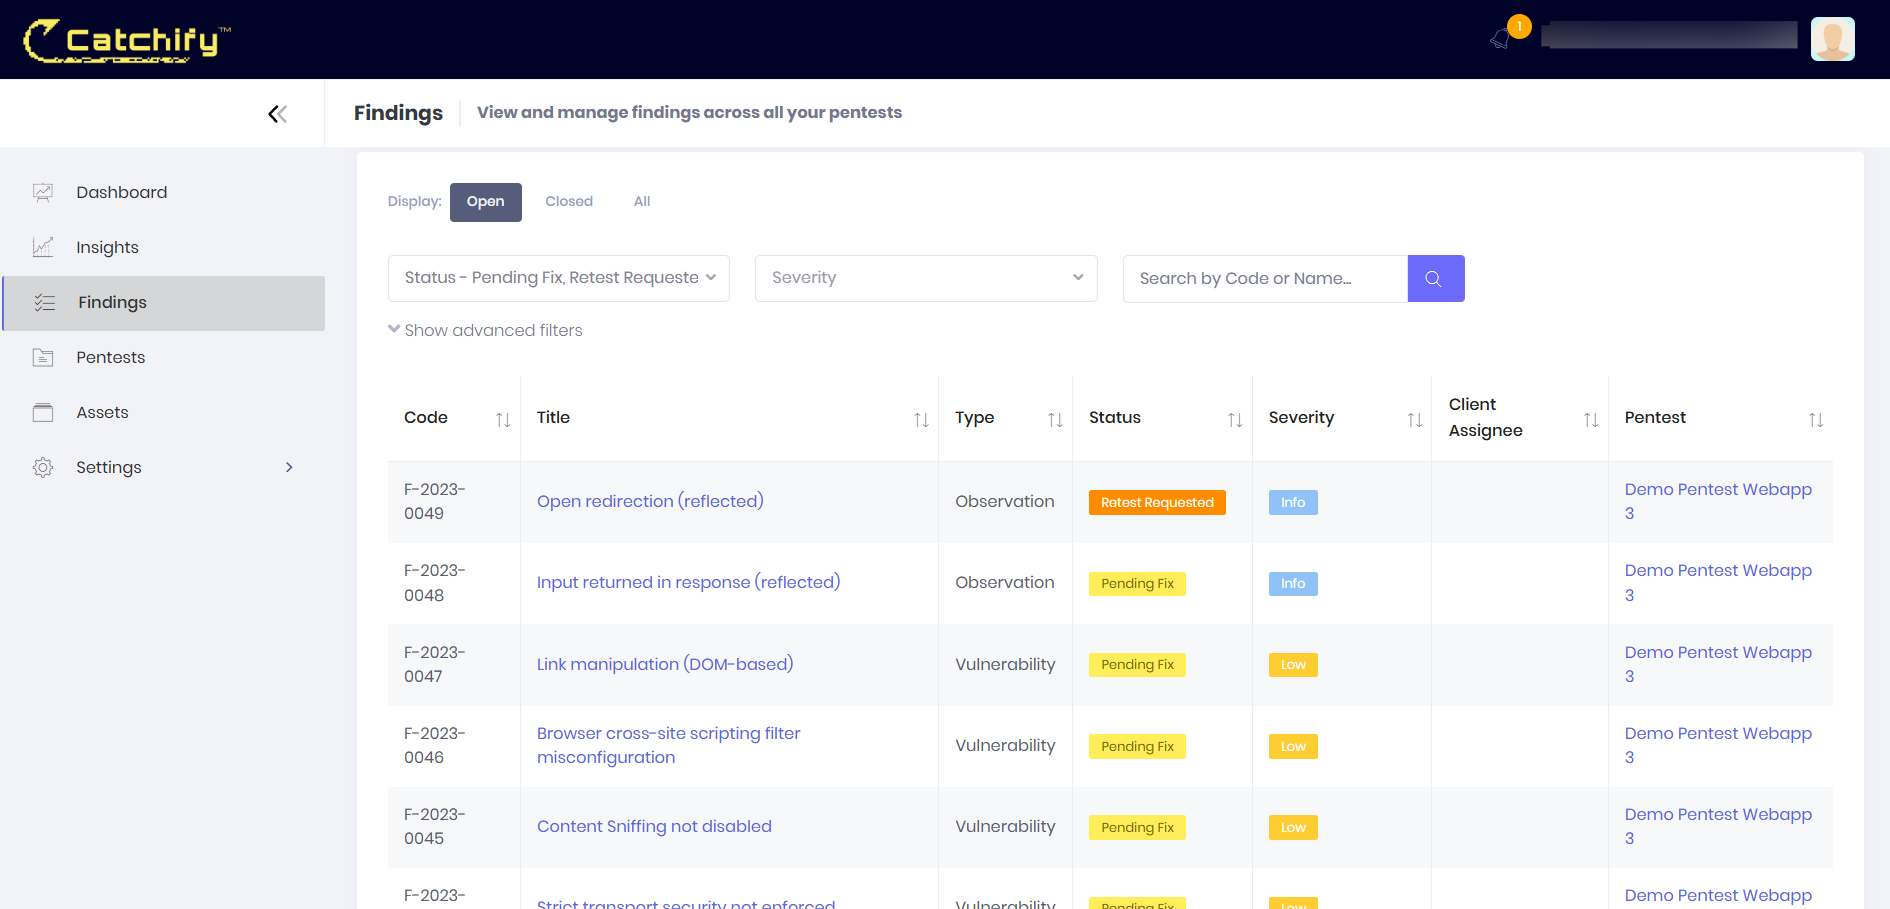
<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FDZyznUF5tYaPb6b5wLK7%2Fimage.png?alt=media&amp;token=b9ee89d8-7582-4d1a-83bc-3813d003d715" alt=""><figcaption></figcaption></figure>

2. Choose the filter: **Open**, **Closed**, or **All**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FdnAo8XYxvTaBleSm0kqx%2Fimage.png?alt=media&amp;token=87f978b0-a85b-45d6-9c9a-76d72ef52859" alt=""><figcaption></figcaption></figure>

3. Use the dropdown menus to sort by **Status** or **Severity**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FEMe6LnXqOyLqM5L0De75%2Fimage.png?alt=media&amp;token=9ff9f0ad-5ae5-4c3a-bf9f-2df1692ba176" alt=""><figcaption></figcaption></figure>

4. Use the search bar or advanced filters to narrow your view

***

### 📂 From a Specific Pentest

1. Click **Pentests** in the left-hand menu

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FWeYgsAsNKz3w0umbtEYB%2Fimage.png?alt=media&amp;token=2cc7b445-f232-42be-bc61-57d15e8a2db3" alt=""><figcaption></figcaption></figure>

2. Choose the pentest you want to inspect

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FrADHpjJQZVSCzvdrZJrx%2Fimage.png?alt=media&amp;token=eeca3953-861d-4b23-a449-1b045dfb3dd7" alt=""><figcaption><p>Pentest Management</p></figcaption></figure>

3. In the pentest tabs, click **Findings**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F6Ez3UOABSUD7qcOFh7XI%2Fimage.png?alt=media&amp;token=7221e582-e9e5-45ac-ab3b-cae4251d0a50" alt=""><figcaption><p>Finding Tab</p></figcaption></figure>

4. Filter the list by **Severity** or **Status**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FXOeZsxcvfMCSuGpLUHdS%2Fimage.png?alt=media&amp;token=a2245824-69f3-43d5-824a-c5d5fc1b69f3" alt=""><figcaption><p>Findins In the Penetst</p></figcaption></figure>

***

### 📊 From the Dashboard

The Dashboard gives you a high-level overview of all active findings:

* **Open Risks** – Displays findings with the highest criticality across all pentests\
  Click "View" to see a list based on severity
* **Findings** – Shows unresolved findings across all projects\
  Click "View" to review and manage remediation

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FVyBv1fWNBTMkRAnOEHR9%2Fimage.png?alt=media&amp;token=dd86a8d5-cdf9-4081-8ec6-83f13e676a32" alt=""><figcaption><p>Dashboard</p></figcaption></figure>

***

Findings are updated in real-time and always available across these views for better visibility and faster response.


# Scoring Explained

Learn how Catchify calculates severity, impact, and risk for each finding — including how CVSS scores help prioritize what to fix first.

In Catchify, each finding is scored based on **Risk** and **Criticality** to help you prioritize what matters most. These scores are set by our assigned pentester, aligned with your organization’s risk profile.

### 🔍 Scoring Breakdown

* **Severity** – Reflects the urgency of the issue based on its potential impact
* **Impact** – Describes how serious the consequences would be if exploited
* **Likelihood** – How likely the vulnerability is to be successfully exploited
* **CVSS** – A standardized score (0–10) that combines impact and likelihood into a single risk number

> **CVSS**: A higher score means the issue is more critical and should be prioritized for remediation.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F2xQf5NRDJV5dkgnOW7Iw%2Fimage.png?alt=media&amp;token=023005f1-514e-406f-91f2-c1b9afe8bccf" alt=""><figcaption></figcaption></figure>

These scores are visualized in the Risk Matrix inside your Catchify portal, giving you a clear view of which vulnerabilities need urgent attention.


# Findings Status

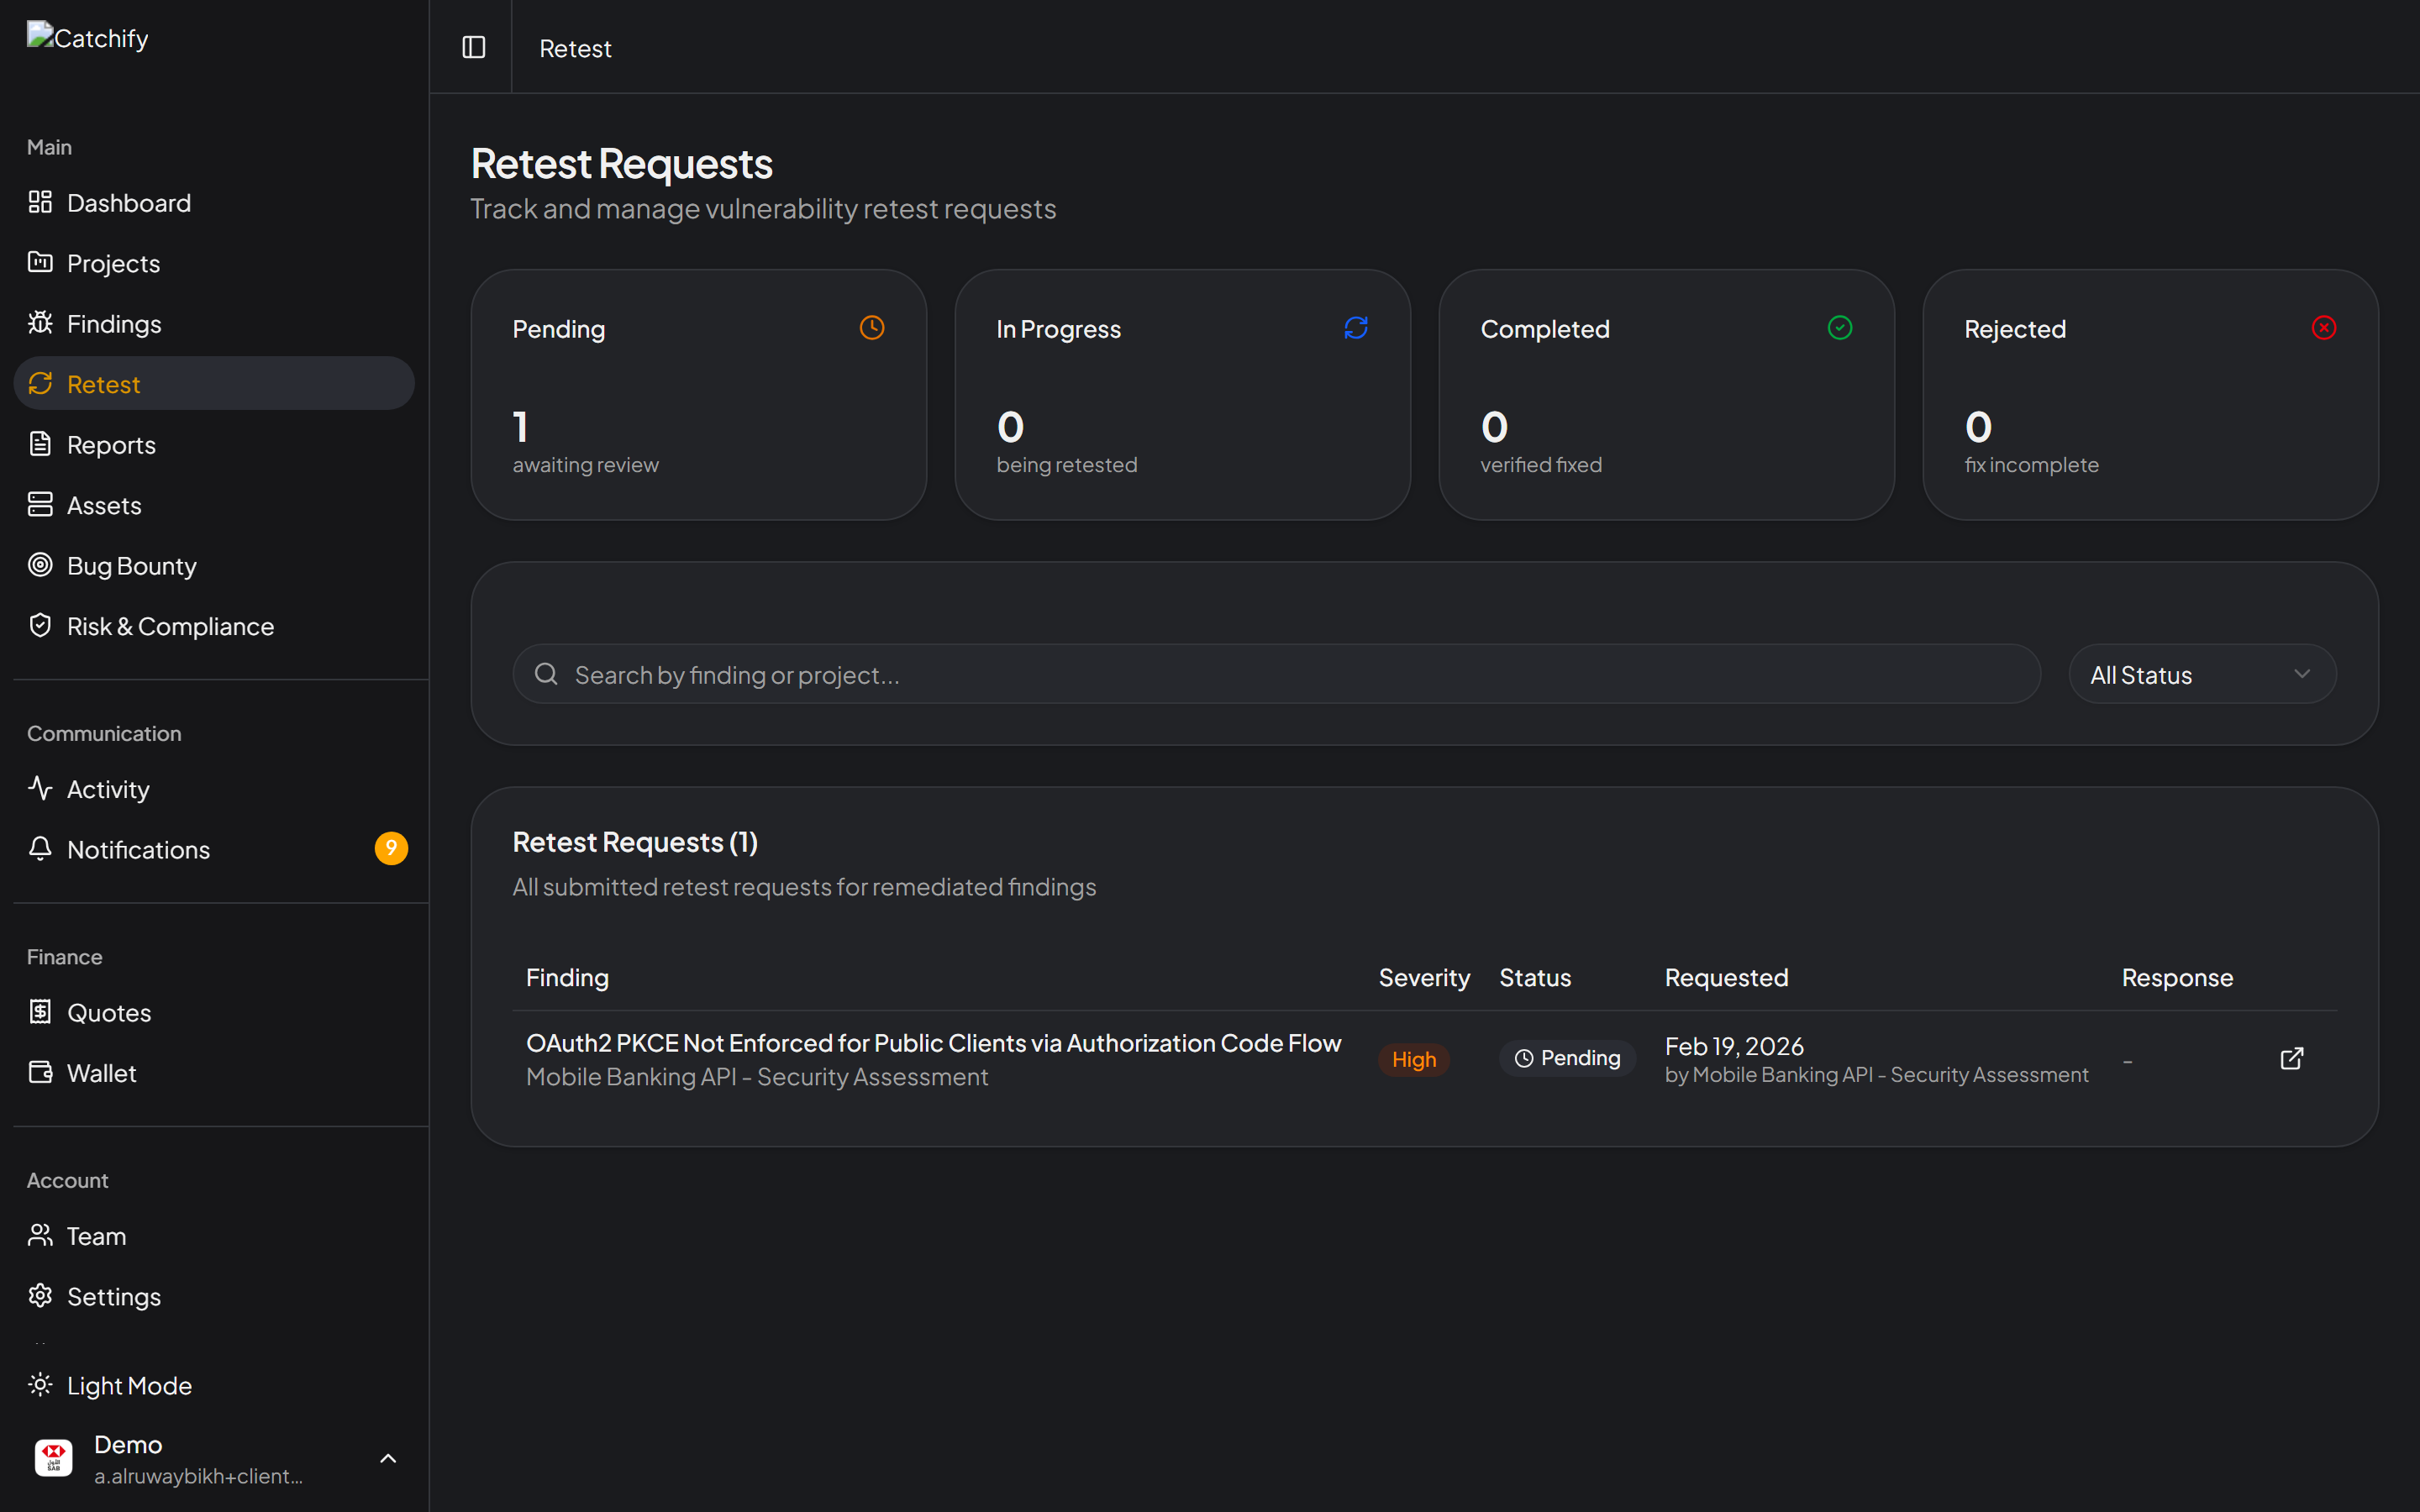
Mark findings as fixed, ready for retest, or accepted risk to keep your remediation workflow clear and aligned with your Catchify pentester.

Finding status helps your team manage remediation and coordinate retesting with Catchify’s pentesters. As your developers take action on each finding, you can update its status to reflect progress.

### 🔄 Status Options

* **Pending Fix** – Finding is newly reported and awaiting developer action
* **Fixed** – The issue has been remediated and no retest is needed
* **Ready Retest** – The issue is fixed and you're requesting validation
* **Accepted** – The risk is acknowledged and accepted as-is by your team

***

### ✅ To Update a Finding Status

1. Click **Pentests** from the left-hand menu

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FsC0OOY2W0sZcyudiqw2J%2Fimage.png?alt=media&amp;token=b87ccc7c-a48a-40b2-bef1-886277b4afcf" alt=""><figcaption></figcaption></figure>

2. Select the pentest you want to manage

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FHGW2rswqFGPxTNuPkMD8%2Fimage.png?alt=media&amp;token=dc164aaa-0171-4883-98a1-95c026708668" alt=""><figcaption></figcaption></figure>

3. Click the **Findings** tab

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FE2UXmYQm91nQfbNN527G%2Fimage.png?alt=media&amp;token=68ac9e35-2c1d-47a3-b97c-d63d64c6f7df" alt=""><figcaption></figcaption></figure>

4. Click the specific **Finding** you want to update

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fuqn9qLvi1Pv8OnAyJE8N%2Fimage.png?alt=media&amp;token=7d89b332-6f83-4bc5-8ac2-aa14b6bcf239" alt=""><figcaption></figcaption></figure>

5. Scroll down and choose a new status from the dropdown

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FhShCGka9ecF9dpRGQOYQ%2Fimage.png?alt=media&amp;token=037d6a9d-046b-4364-8e7f-c139471c5753" alt=""><figcaption></figcaption></figure>

6. Click **Submit** to save

***

This process ensures your remediation flow is visible and organized for both your team and the pentester.


# Communication With Pentesters

Use Catchify's comment box and file upload to securely collaborate with your pentester and keep all communication in one place.

You can leave comments, upload proof (like screenshots or logs), and tag team members, all within the Finding view.

***

### 💡 Steps to Communicate on a Finding

1. Go to **Pentests** in the left-hand menu

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FXjZj4rSbgR3PCIWAONNZ%2Fimage.png?alt=media&amp;token=fa419856-e4f0-4e6e-816c-ed57c5e3262c" alt=""><figcaption></figcaption></figure>

2. Select the pentest you want to work on

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F014KQT51cuZK20TOmugg%2Fimage.png?alt=media&amp;token=0a7a12d8-1bb9-4f9f-8380-74152982151f" alt=""><figcaption></figcaption></figure>

3. Click the **Findings** tab

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FIovebKvHOZeWgKLLDaiG%2Fimage.png?alt=media&amp;token=06a83aa1-d344-4fa1-b071-f3b9b901724b" alt=""><figcaption></figcaption></figure>

4. Open the finding you want to comment on

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FzmTM6OrWfjxYEb3xEltK%2Fimage.png?alt=media&amp;token=c12fc120-3a17-44f0-80a5-8bdf58d3202b" alt=""><figcaption></figcaption></figure>

5. Scroll to the bottom and use the **comment box**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FkRoIsW9L4o9YorPDCM8J%2FScreenshot%202020-07-01%20at%2001.49.53.png?alt=media&amp;token=1d752590-f5cf-4a32-bfde-e308e766c7e4" alt=""><figcaption></figcaption></figure>

6. Use **Add Attachment** to upload files (screenshots, logs, etc.)
7. (Optional) Update the **status** if it has changed
8. Click **Submit**

> Everyone assigned under the "Team" tab will be notified of new comments or uploads.

***


# User Management

Add, remove, and manage users in your Catchify workspace, including password resets, 2FA enforcement, and user lockouts.

User Management in Catchify allows Admins to control who can access the platform, assign the right roles, and maintain secure access across your team.

### 🔧 What You Can Do

* **Add and remove users**
* **Assign roles** such as Admin, Developer, or Viewer
* **Enforce 2-Factor Authentication (2FA)** for enhanced security
* **Reset passwords** or trigger recovery options
* **Lock out accounts** after multiple failed login attempts
* **Update user permissions** anytime

Catchify also supports:

* Password reset and recovery flows
* Enforced login security policies
* User activity visibility for admins

> Keep your workspace secure and organized by managing access and actions from one centralized place.


# Two Factor Authentication

Enable 2FA to add an extra layer of protection to your Catchify account using email or Google Authenticator. Recommended for all users.

To enhance account security, Catchify supports 2-Factor Authentication (2FA) for all users.

Admins can require 2FA on account creation, or individual users can enable it anytime through their profile settings.

***

### ✨ How to Enable 2FA

1. Click your **user email** at the top right corner
2. Select **My Settings**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FC66yxCU65SP8XONpOPxf%2Fimage.png?alt=media&amp;token=ed6ab442-47c7-40fd-8ab8-a9a670381fca" alt=""><figcaption></figcaption></figure>

3. Go to the **2-Factor Authentication** tab
4. Click **Enable**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FnmttdLRJreoffHvuyaTi%2Fimage.png?alt=media&amp;token=e475e7c5-9e8c-423d-b351-ee701e559827" alt=""><figcaption></figcaption></figure>

***

### 🔒 Using Google Authenticator (Recommended)

To set up Google Authenticator:

* Click **Enable** next to “Google Authenticator”
* Scan the QR code with your mobile authenticator app
* Complete the code confirmation in the app
* Click **Save**

> We recommend using Google Authenticator as you will probably deal with senesitive infomration for your orgnaization.


# Managing Users in Catchify

Add, edit, delete, or pause users in your Catchify workspace to maintain secure and flexible access control across your team.

Admins in Catchify can easily add, edit, delete, or pause access for users as needed. Here's how to manage users efficiently from the platform.

***

### ➕ Create New User

1. Go to **Settings** in the left-hand menu
2. Click **Users**
3. Click **New User**
4. Enter user details (Name, Email, etc.)
5. Assign permissions
6. Click **Save**

***

### ✏️ Edit Existing User

1. Go to **Settings** > **Users**
2. Click on the user you wish to edit

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FeeF2JC7gtTwtnW8ZuTKL%2Fimage.png?alt=media&amp;token=cd1290f9-cab4-4c34-b3f5-efdbb2f76870" alt=""><figcaption></figcaption></figure>

3. Click **Edit**
4. Make changes (name, email, role, or permissions)
5. Click **Save**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FRMBCGH1jmBivN8Cgxons%2Fimage.png?alt=media&amp;token=3ea48806-6ec5-4d34-8861-3466056bcdd0" alt=""><figcaption></figcaption></figure>

***

### 🗑️ Delete a User

1. Go to **Settings** > **Users**
2. Click the user you want to remove
3. Click **Edit** > **Delete**

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FJ3uqjwj0CBE1hdsFECvN%2Fimage.png?alt=media&amp;token=bf26af79-b521-4142-8e2f-9265bc50eaca" alt=""><figcaption></figcaption></figure>

4. Confirm deletion

> ⚠️ Deletion is permanent and cannot be undone.

***

### ⏸️ Pause User Access

1. Go to **Settings** > **Users**
2. Click the user
3. Click **Edit**
4. Scroll down and check "Lock user" or disable login permissions

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FNLvpGlh22j03FoAhub8o%2Fimage.png?alt=media&amp;token=40a94ad3-0fac-4ac5-82a0-50bc6307810b" alt=""><figcaption></figcaption></figure>

5. Click **Save**

> Use this when temporarily revoking access instead of deleting an account.


# Password And Recovery

This section allows administrators to securely manage user credentials. You can update passwords, trigger account verification emails, and disable lockouts when necessary, ensuring users can access t

Admins on Catchify can manage user password resets, enforce new password creation, and control lockout behavior for enhanced security and flexibility.

***

### 🔑 Resetting a User’s Password

To reset a user’s password:

1. Click **"Settings"** in the left-hand menu.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FJ4N2rwifiLahRPJoDO6W%2Fimage.png?alt=media&amp;token=30a45e98-94de-447f-b1c2-7e1a1dc47efe" alt=""><figcaption></figcaption></figure>

2. Click **"Users"**.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FzuwuAYhvnbfJcY7LRIBk%2Fimage.png?alt=media&amp;token=971d5ff1-81b8-4977-bdce-2a4887e9f5ff" alt=""><figcaption></figcaption></figure>

3. Locate the user you want to edit and click the **three dots (...)** under "Actions".
4. Select **"Edit"**.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2F4UHIRlzfnV9Fv17m9QkF%2Fimage.png?alt=media&amp;token=84b31438-93b9-4e96-a2ae-2c5257df4834" alt=""><figcaption></figcaption></figure>

5. Enter a new password in the **"Set New Password"** fields.

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FijOU1mC87yJX0Zato00N%2Fimage.png?alt=media&amp;token=985238e8-4122-477e-92c9-9c4a225b50b8" alt=""><figcaption></figcaption></figure>

6. Check:

* ✅ *Send Activation Email* – Sends a verification email again.
* ✅ *Change Password on Next Login* – Forces the user to set a new password.

7. Click **"Save"**.

***

### 🚫 Managing Lockouts

Catchify automatically locks users out after 3 failed login attempts. To disable lockout for a specific user:

1. Click **"Settings"** > **"Users"**.
2. Find and edit the user.
3. Scroll to the bottom and **uncheck**:
   * ⬜ *Lockout Enabled*

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FcQuR5wrjRAZW5iUUN76X%2Fimage.png?alt=media&amp;token=c63e53a2-4e8b-47c7-89af-9d69647fd440" alt=""><figcaption><p>Lockout Check</p></figcaption></figure>

4. Click **"Save"**


# Integration

Catchify is designed to integrate smoothly with the tools your team already uses to manage workflows, track issues, and ensure accountability.

Our integration features help reduce context switching, speed up remediation, and keep your security processes efficient and transparent.

#### Jira Integration

Currently, Catchify supports native integration with **Jira** — one of the most popular project and issue tracking platforms used by security and development teams. With this integration, you can:

* Push findings from Catchify directly into Jira as issues
* Link findings to specific Jira projects, epics, or sprints
* Automatically sync statuses between platforms
* Assign vulnerabilities to relevant developers for remediation
* Maintain a full audit trail from discovery to resolution

This integration ensures that vulnerabilities discovered during your pentests become actionable tasks in your existing workflow without the need for manual duplication or follow-ups via email.

#### How It Works

Once Jira is connected, authorized users can map Catchify findings to Jira projects and define rules for how findings are pushed (severity filters, default assignees, issue types).&#x20;

***

If you have a preferred tool you'd like to integrate with Catchify, let us know, we’re building our roadmap with your needs in mind.


# Jira Integration

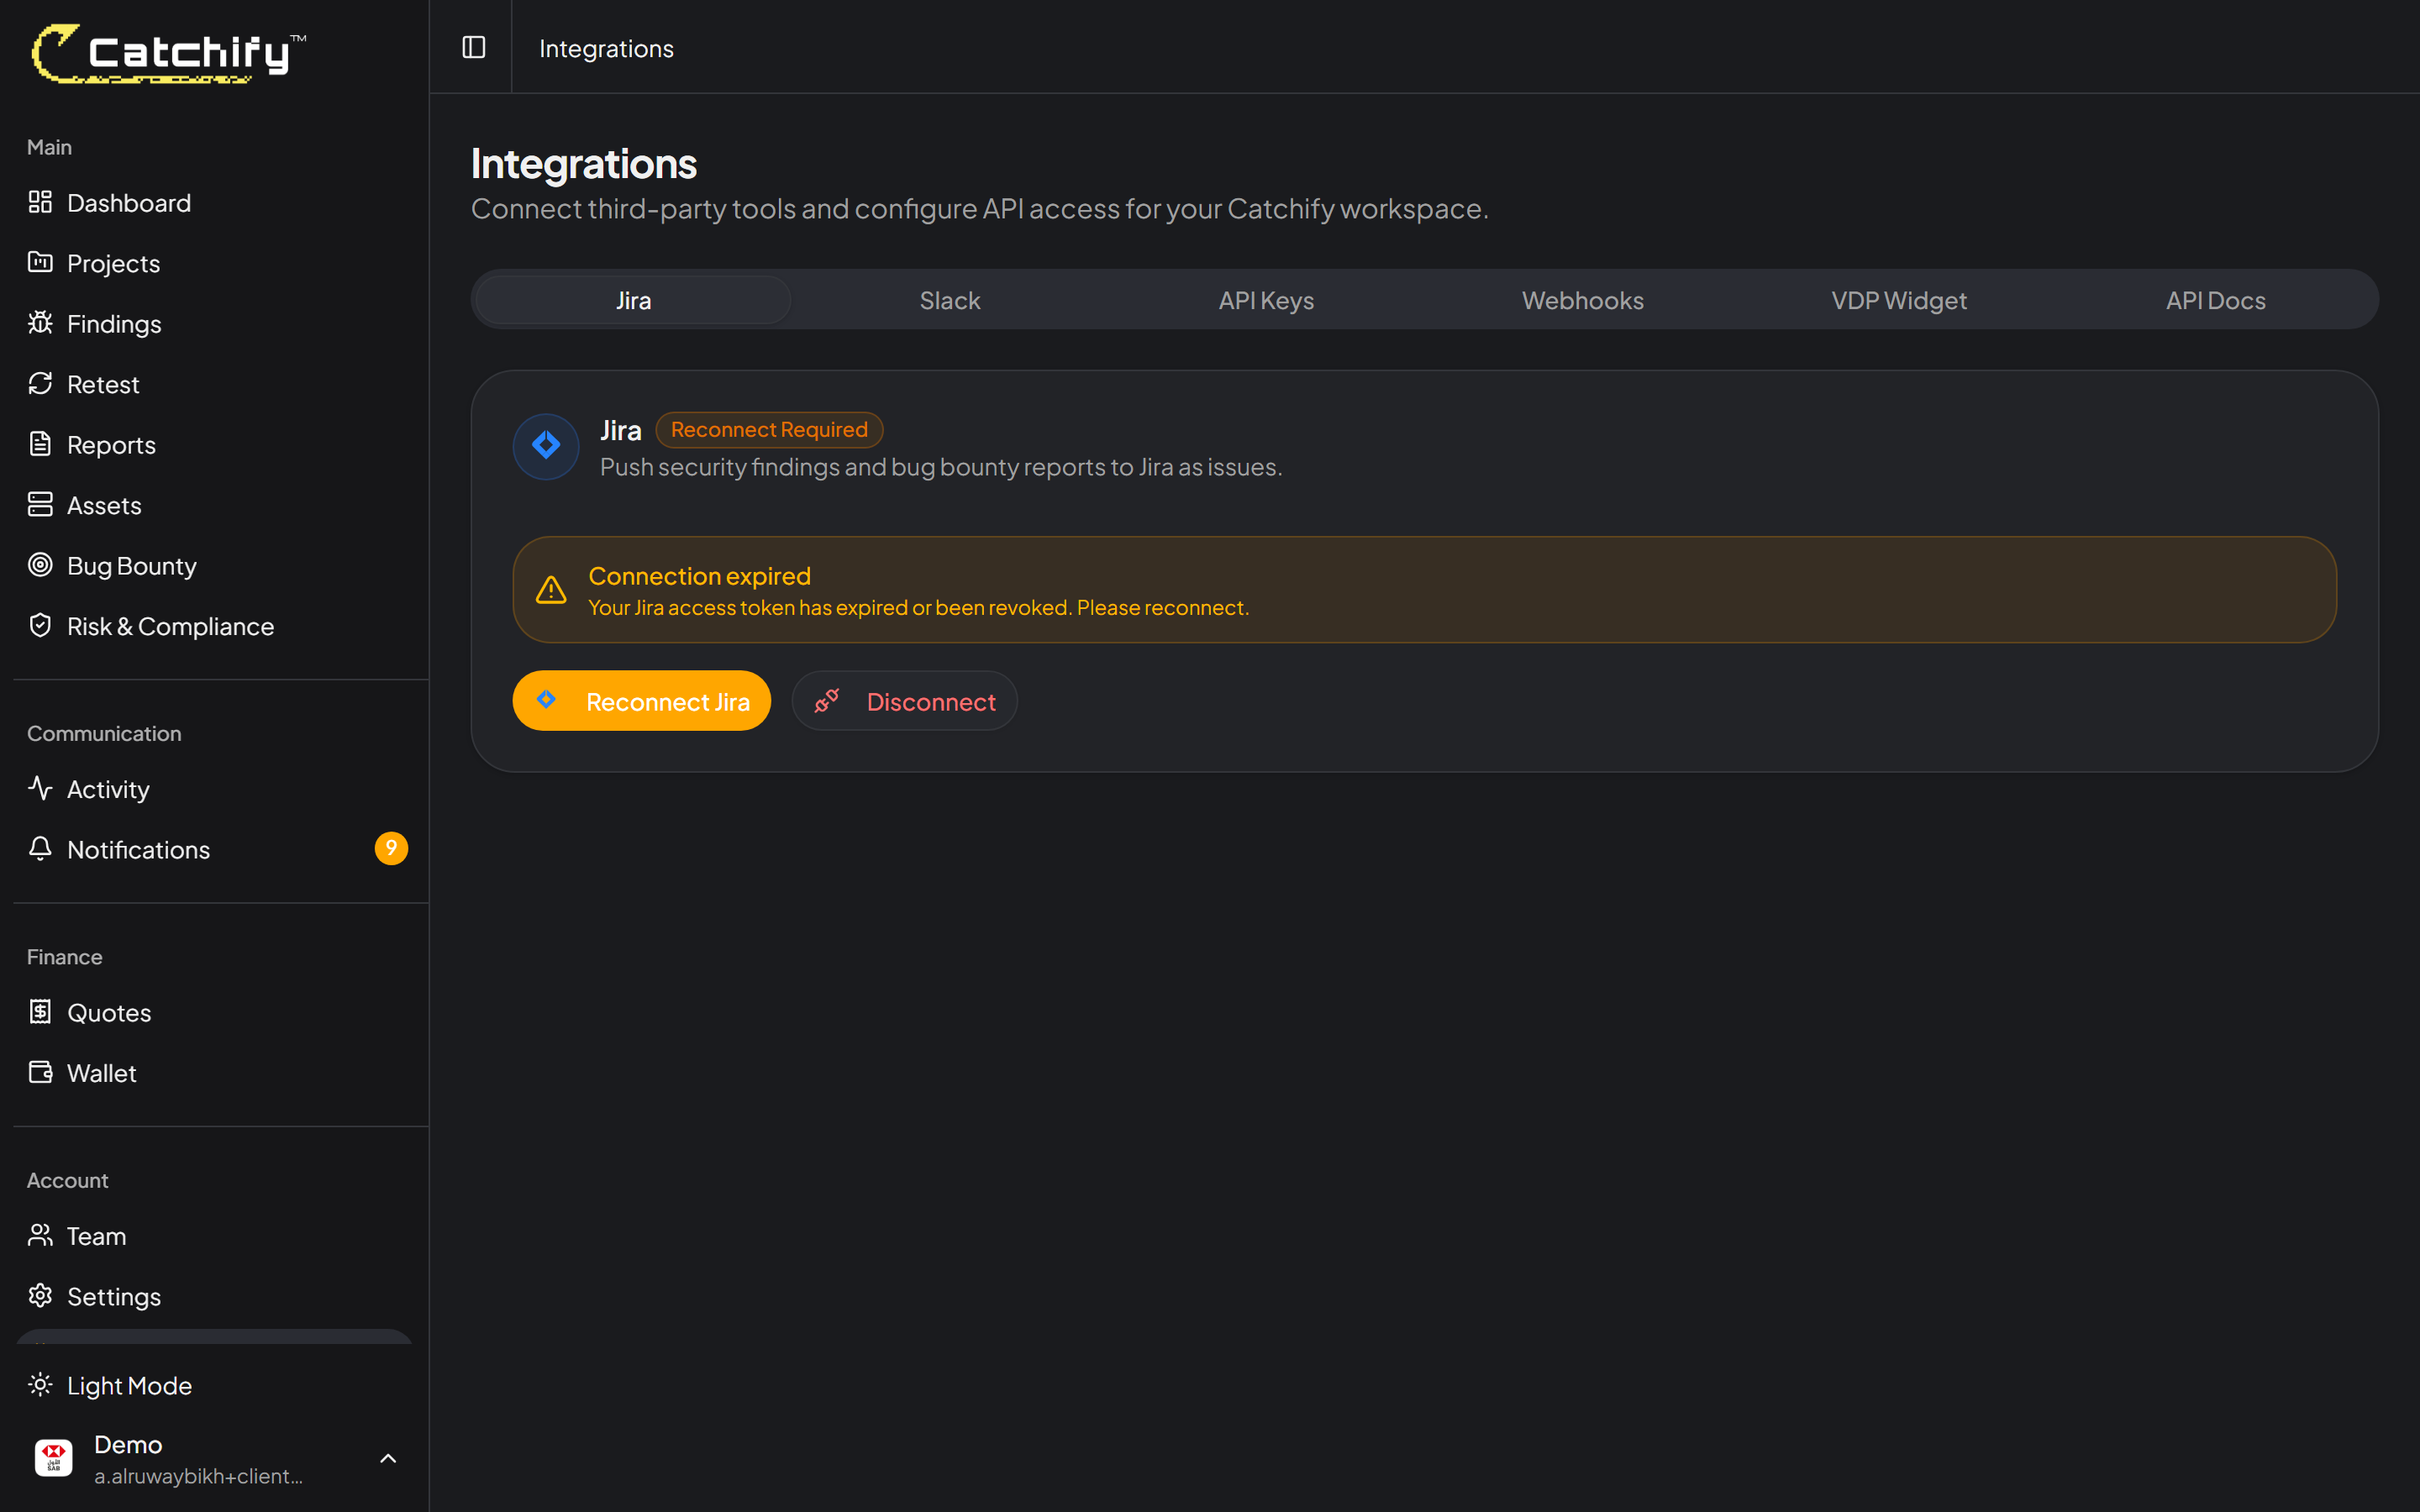
Connect your Catchify workspace with Jira Cloud to streamline issue tracking.

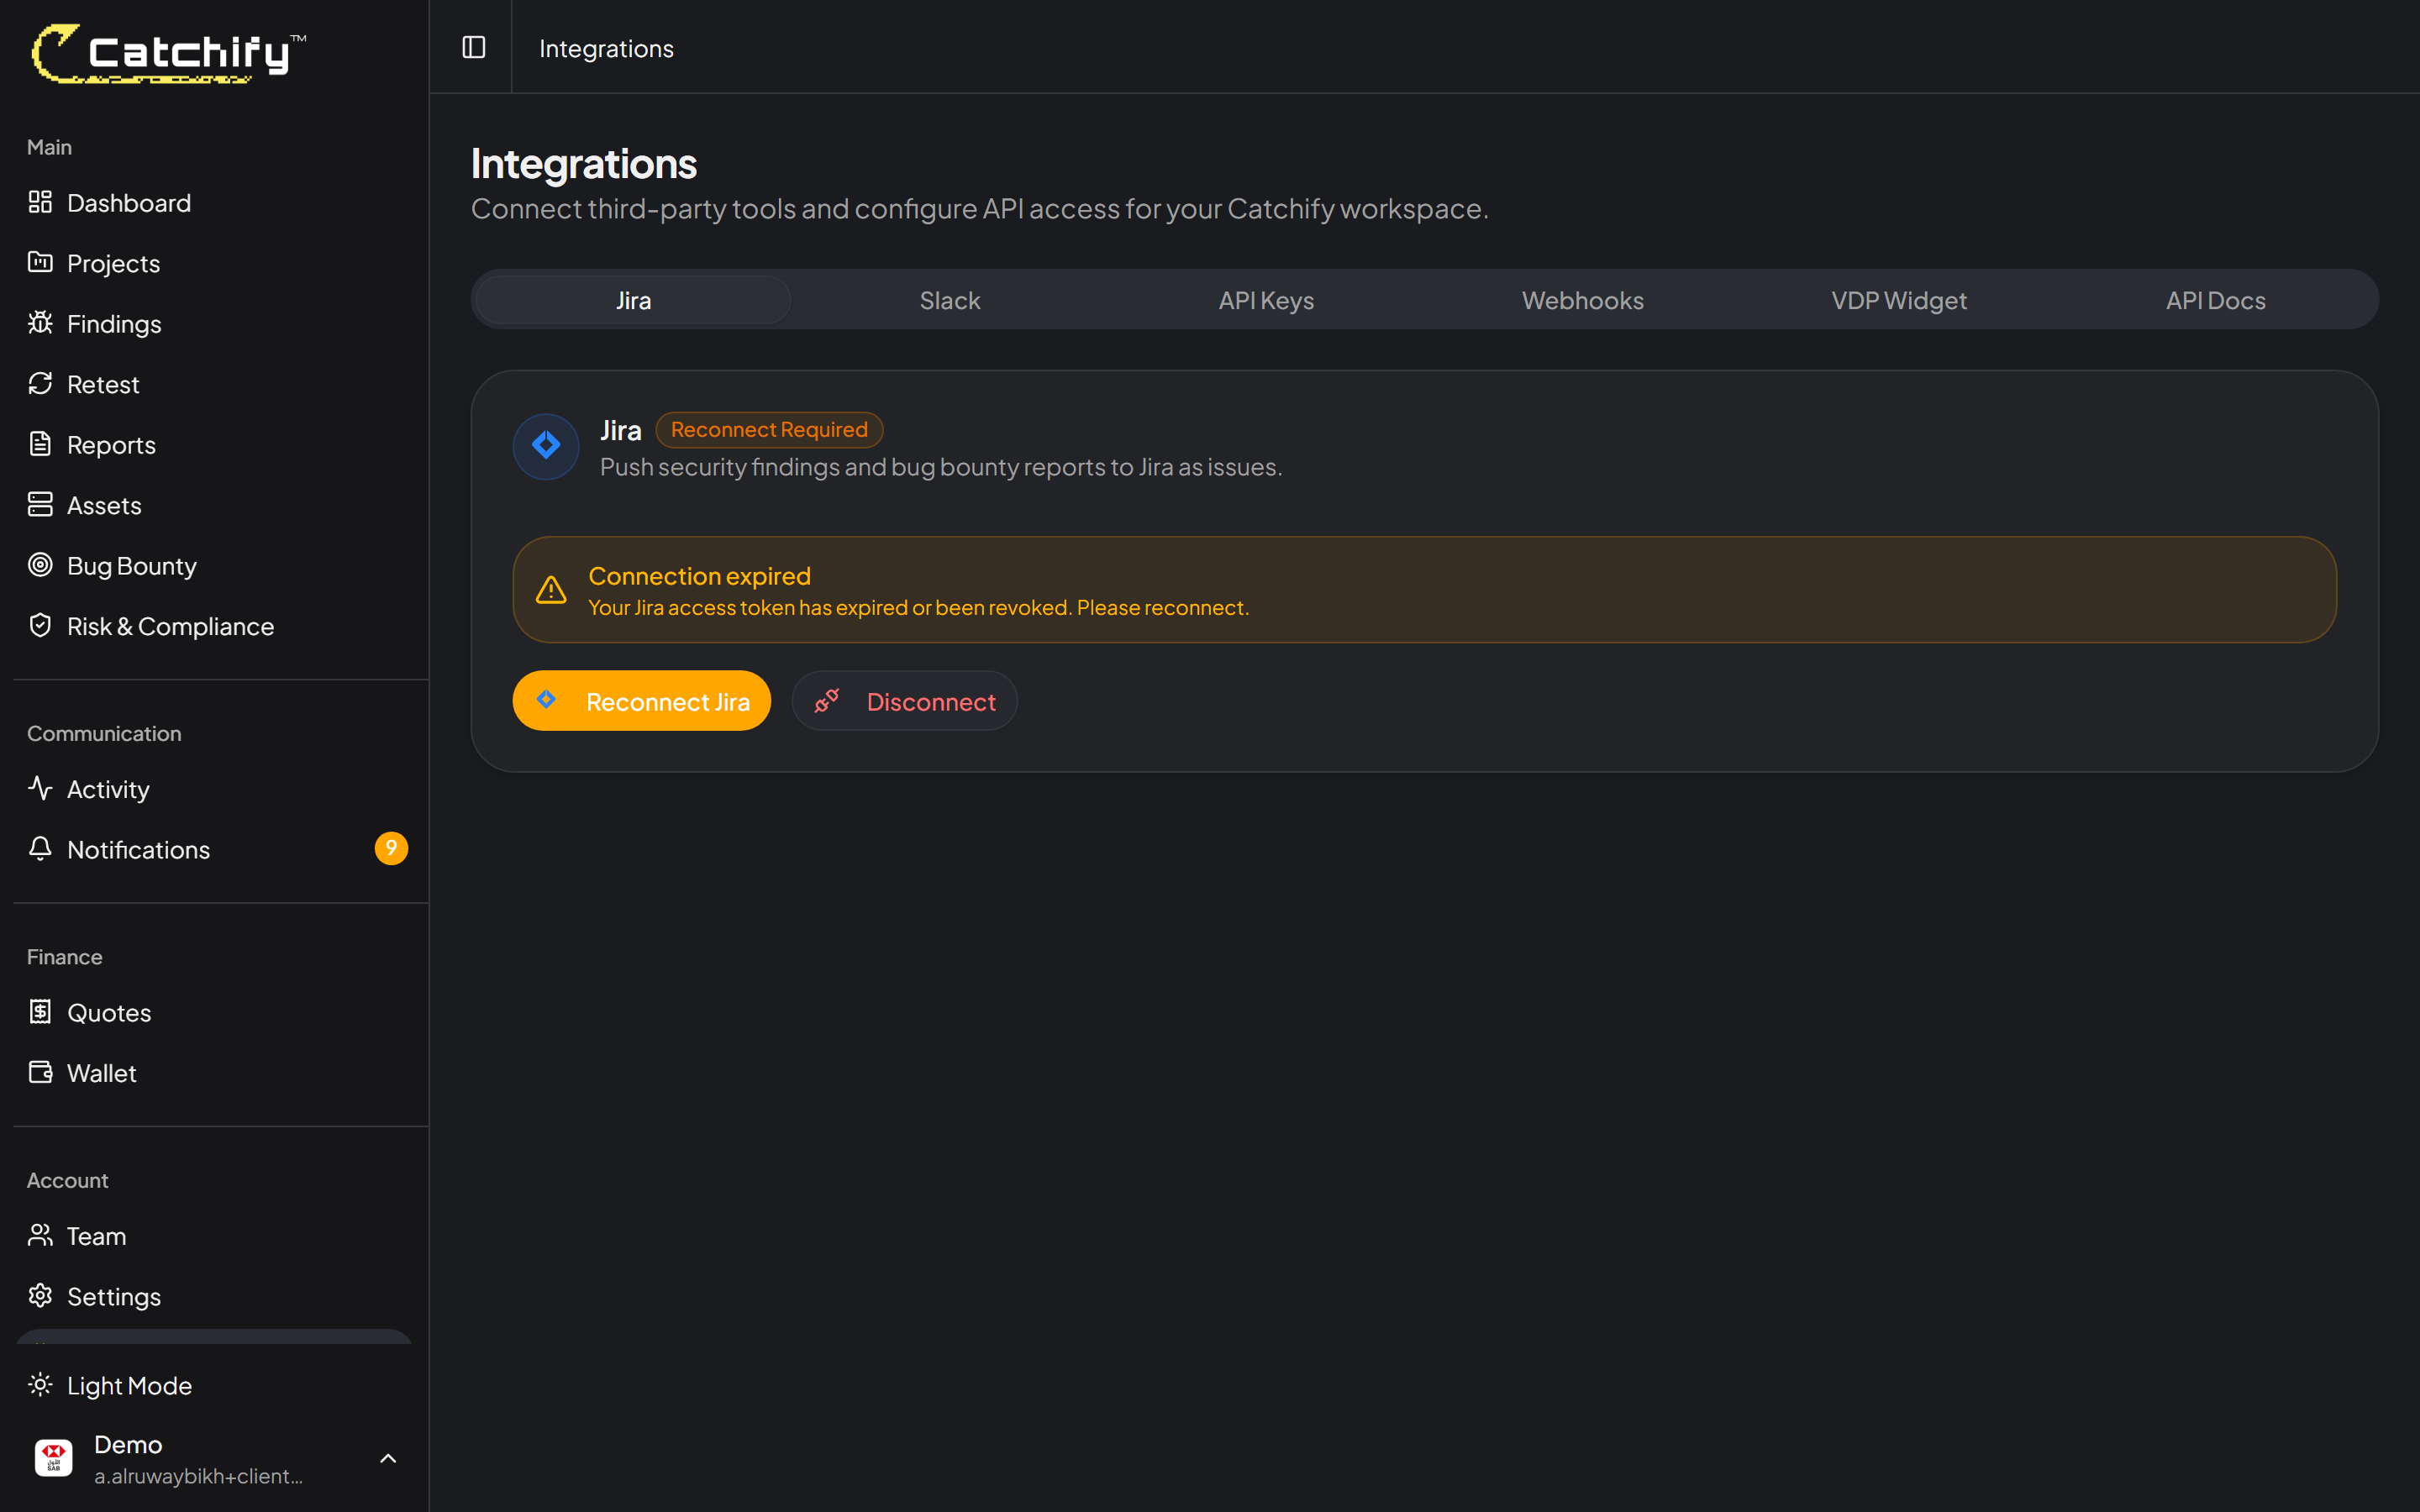
Catchify allows seamless integration with Jira Cloud, enabling you to push findings directly into Jira issues or link them to existing ones. This helps streamline collaboration between your security team and developers, all from within the platform.

***

### 🔌 Connect Client Portal – Jira Cloud

#### 1. Connect to Your Jira Cloud Account

* Navigate to **Settings** in the left-hand menu
* Go to **Integrations**
* Click **Connect to Jira** under the Jira Integration section

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FlrHZL3ytaqObRYGembRM%2Fimage.png?alt=media&amp;token=477d8f72-fa00-4e88-9901-0821e4ea3bce" alt=""><figcaption></figcaption></figure>

> You’ll be redirected to authorize Catchify with your Jira account.

#### 2. Choose a Jira Project

* Once connected, select which Jira project you want to sync with
* You can now send findings from Catchify to your chosen Jira project

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FoZdz7hGFJJ4kysmlpnx9%2Fimage.png?alt=media&amp;token=3cd95f5f-6cd0-4108-832d-587f99fd6ea0" alt=""><figcaption></figcaption></figure>

![](https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2FLl1hQtzRdNAXBp5iMnMd%2Fimage.png?alt=media\&token=cd47ed94-1a8d-47b1-8c53-52cb360cbf3f)

Your Jira Cloud account is now successfully connected!

***

### 📝 Create New Jira Ticket

#### 1. Open a Finding

* Go to the **Findings** section and select the vulnerability you want to escalate

#### 2. Click on “Create Jira Ticket”

* Choose the appropriate **issue type** (Bug, Task, etc.)
* The title and description fields will be pre-filled, adjust as needed

#### 3. Click **Create**

* The finding will now appear in Jira and will be traceable from Catchify

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fi2yTdgAVzhMMPXkmvDl1%2Fimage.png?alt=media&amp;token=e73b1994-865f-49e2-b54e-e147d237fab2" alt=""><figcaption></figcaption></figure>

***

### 🔗 Link to Existing Jira Ticket

#### 1. Open the Finding

* Navigate to the relevant finding in Catchify

<figure><img src="https://1159325253-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fmq03Q5eywxpWcWY1bNEr%2Fuploads%2Fmd0SMN1Dah5mi2QxuAJx%2Fimage.png?alt=media&amp;token=d847c405-f713-4481-b744-6dd237ada859" alt=""><figcaption></figcaption></figure>

#### 2. Click "**Link to Existing Ticket"**

* Type in the **title or key** of the existing Jira issue (`SEC-341`)

#### 3. Click **Link**

* The finding is now associated with that Jira issue for future tracking and updates

***

*Note: You must have admin rights in Catchify to enable this integration.*


# Terms and Conditions

This is the Terms and Conditions for Catchify's PTaaS system.

## Catchify – Terms and Conditions

Welcome to Catchify. These Terms and Conditions govern the use of our Penetration Testing as a Service (PTaaS) platform and all related services. By engaging with Catchify, you agree to comply with these terms.

***

### 1. Service Scope

Catchify provides manual and automated security assessments, including:

* Web & mobile application testing
* Infrastructure penetration testing
* Vulnerability analysis and risk reporting

Services may be delivered under different billing models, including **Pay-On-Catch,** and the scope is defined per engagement or Order Form.

***

### 2. Pay-On-Catch Model

The Pay-On-Catch model applies **only** to eligible PTaaS engagements agreed upon in writing before testing begins.

* **No fees** are charged if **no valid vulnerabilities** are found.
* Vulnerabilities are rated based on severity (CVSS or custom scale).
* Fees are incurred **only for verified findings**, priced according to severity.
* A final invoice is issued after the client receives the report.
* Catchify reserves the right to determine which engagements qualify for Pay-On-Catch.

***

### 3. Client Responsibilities

Clients agree to:

* Provide **written authorization** to perform penetration testing.
* Clearly define the testing scope and acceptable boundaries.
* Supply any necessary credentials or access tokens securely.
* Maintain operational backups and monitoring during the testing period.

***

### 4. Confidentiality

* Catchify treats all client information, test results, and system data as **strictly confidential**.
* No information is disclosed to third parties without the client's written consent, unless required by law.

***

### 5. Payment Terms (Fixed-Price Engagements)

For fixed-price engagements:

* Fees are agreed upon before the start of the engagement.
* An invoice is issued based on milestones or deliverables as defined in the Order Form.
* Payment is due within **15 days** unless otherwise stated in the agreement.

***

### 6. Report Delivery

Clients receive a detailed report including:

* Vulnerabilities found
* Severity ratings
* Recommended remediation

Reports are delivered securely and may be followed by a debrief session if agreed.

***

### 7. Use of Findings

Catchify’s findings are for internal security improvement. Clients may:

* Use reports to guide remediation or compliance
* Share internally with relevant departments
* Share externally only with prior written consent from Catchify

***

### 8. Testing Limitations

While best efforts are made to uncover vulnerabilities:

* No guarantee is made that all vulnerabilities will be discovered.
* The presence or absence of findings does not imply full security or insecurity.
* Testing is time-boxed and limited to defined scope.

***

### 9. Intellectual Property

* Catchify retains all rights to proprietary tools, scripts, and methodologies used during the engagement.
* Clients may use provided reports and deliverables internally but may not reproduce, modify, or resell without permission.

***

### 10. Disclaimer of Warranties

Catchify provides services "as-is" and makes no warranties regarding:

* Complete vulnerability coverage
* Compatibility with regulatory frameworks unless explicitly stated
* Zero impact on system performance during testing

***

### 11. Limitation of Liability

To the maximum extent permitted by law:

* Catchify is not liable for any indirect, incidental, or consequential damages.
* Direct liability is limited to the total amount paid by the client for the affected engagement.
* The client accepts responsibility for patching and mitigation of all vulnerabilities post-disclosure.

***

### 12. Termination

#### 12.1 Termination for Cause

Either Catchify or the Client may terminate an Order Form or engagement if the other party materially breaches these terms and fails to cure the breach within **forty-five (45) days** after receiving written notice.

#### 12.2 Catchify’s Right to Suspend Access

Catchify may, at its sole discretion, suspend or terminate platform access or engagement for any party not governed by an active Order Form, without notice.

#### 12.3 Client-Initiated Termination

Clients may cancel their account or engagement at any time by emailing **<info@catchify.sa>**. However:

* In **Pay-On-Catch** engagements, if valid vulnerabilities have been discovered prior to cancellation, **payment is still due**.
* Clients are **not entitled to refunds** for any prepaid services unless explicitly stated in the Order Form.

#### 12.4 Effect of Termination

Upon termination:

* All due payments must be completed.
* Sections related to confidentiality, liability, and report usage will remain in effect.

***

### 13. Governing Law

These Terms shall be governed by and construed in accordance with the laws of the **Kingdom of Saudi Arabia**. Any disputes shall be subject to the exclusive jurisdiction of Saudi courts.

***

### 14. Contact

For any questions or formal notices, contact:

**Catchify Security Services**\
Email: **<info@catchify.sa>**\
Website: [www.catchify.sa](http://www.catchify.sa)


# Privacy Policy

This is the Privacy Policy for catchify's PTaaS System.

## Catchify – Privacy Policy

At Catchify, we respect your privacy and are committed to protecting the confidentiality, integrity, and security of your information. This Privacy Policy explains how we collect, use, store, and protect your data when you interact with our services.

***

### 1. Information We Collect

We collect only the information necessary to deliver secure, ethical, and efficient penetration testing services:

#### 1.1 Client-Provided Information

* Full name and contact details (email, phone number, company)
* Authorized asset details (domains, IP ranges, app URLs)
* Test accounts (if applicable)

#### 1.2 Automatically Collected Data

* Audit logs and testing metadata (date/time of access)
* IP addresses or browser data when using our client portal

***

### 2. How We Use Your Information

We use your data solely to:

* Perform the agreed-upon penetration testing engagement
* Identify and report vulnerabilities
* Communicate findings, updates, or follow-up actions
* Process payments in accordance with the chosen engagement model
* Comply with legal and regulatory obligations

***

### 3. Data Retention

* Sensitive credentials or access tokens are stored securely and deleted immediately after the engagement ends.
* Reports and client communication are retained for a period of **\[12 months]** for record keeping, unless otherwise requested by the client.

***

### 4. Sharing and Disclosure

We do **not** sell, trade, or rent your personal or system data.

We may share information only:

* With your **explicit written consent**
* With authorized team members bound by confidentiality agreements
* When legally required by competent authorities

***

### 5. Data Security

We take security seriously. Measures include:

* Encryption at rest and in transit
* Role-based access control (RBAC)
* Secure credential handling
* Regular internal audits and secure development practices

***

### 6. Your Rights

You have the right to:

* Request access to your stored data
* Request correction or deletion of your data
* Withdraw consent for future processing
* Request secure deletion of reports after engagement closure

For any of the above, contact us at **<info@catchify.sa>**

***

### 7. Cookies and Authentication

Catchify may use minimal cookies to:

* Authenticate user sessions
* Improve performance and user experience

No tracking or advertising cookies are used.

***

### 8. Third-Party Services

Catchify may integrate with third-party platforms such as **Jira** to streamline issue tracking and reporting processes. These integrations are used only to:

* Report validated vulnerabilities directly into client-managed Jira projects (when authorized)
* Automate secure communication of technical findings
* Enhance client remediation workflows

We do **not** share client data with third-party services without **explicit written consent**. All integrations are limited in scope, use secure API connections, and follow best practices for access control and data minimization.

***

### 9. Changes to This Policy

Catchify may update this Privacy Policy periodically. Material changes will be communicated via email or our website.

***

### 10. Contact

For questions or privacy-related requests, please contact:

**Catchify Security Services**\
Email: **<info@catchify.sa>**\
Website: [www.catchify.sa](http://www.catchify.sa)

***


# Welcome

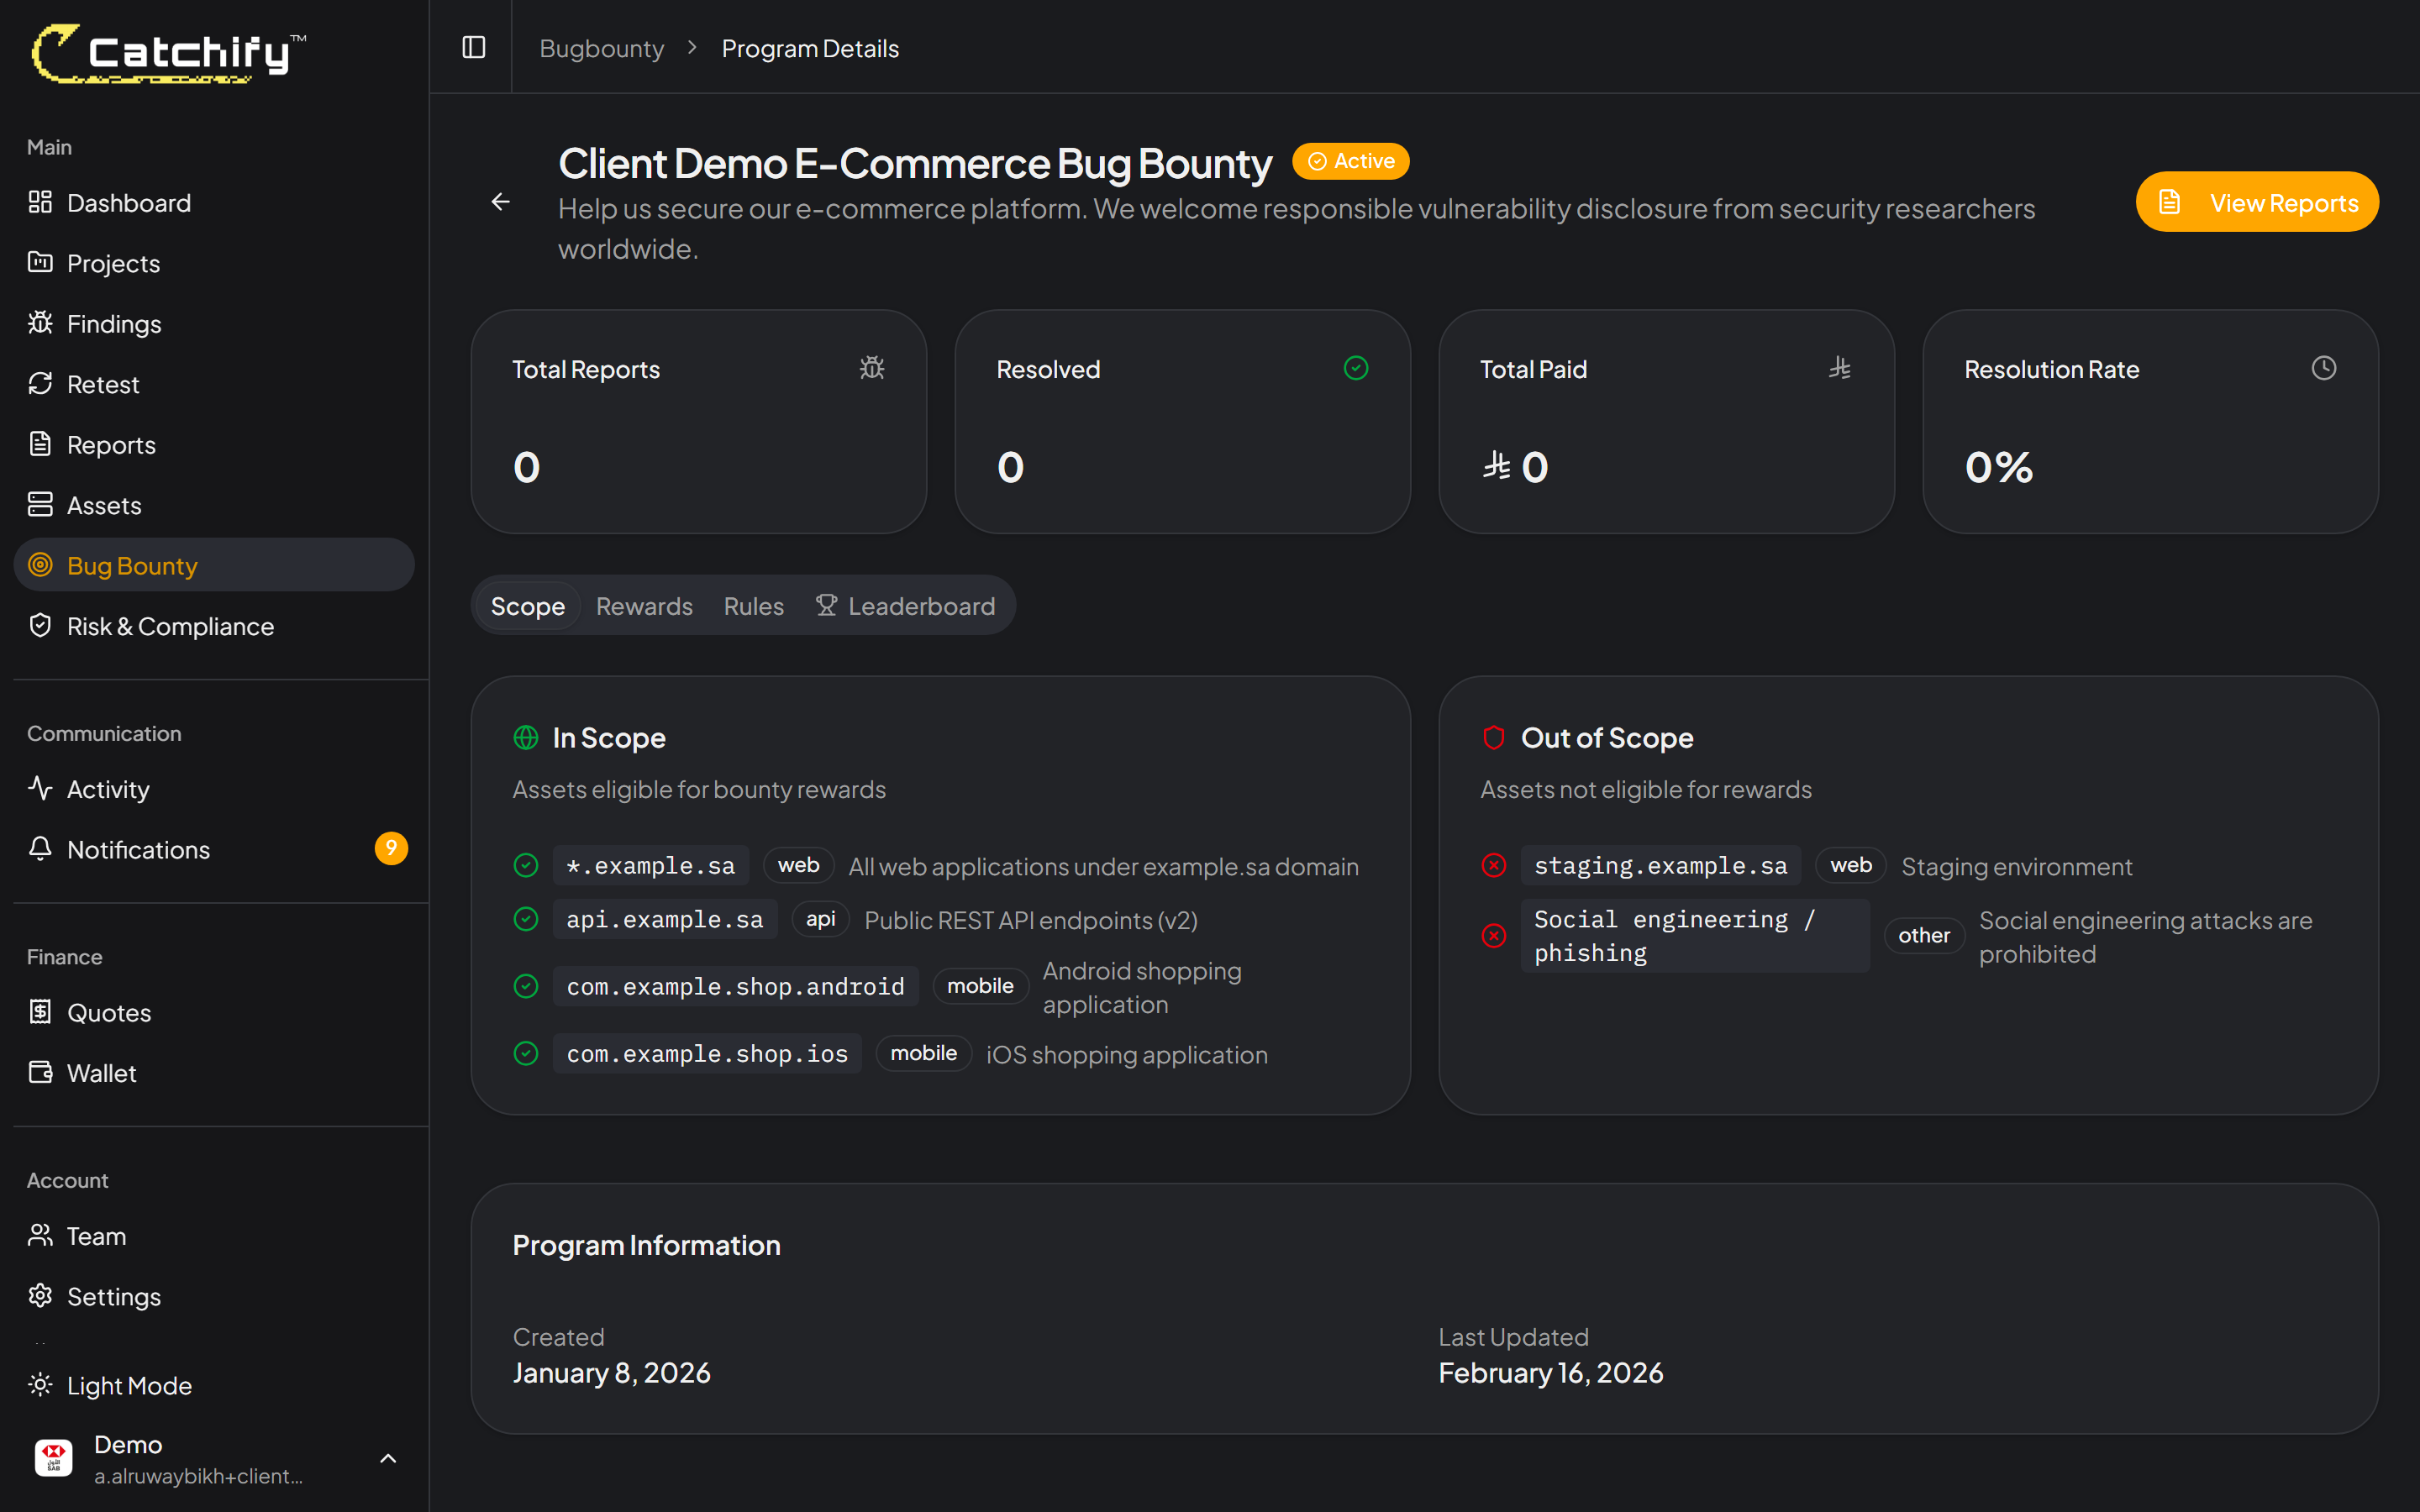
Catchify is Saudi Arabia's leading cybersecurity platform, built to help organizations discover and fix security vulnerabilities before they become threats. Whether you need structured penetration testing or a continuous bug bounty program, Catchify brings together world-class security researchers and an intuitive client portal so you can manage your entire security testing program from one place.

## What Catchify Does

Catchify offers two core services through a single, easy-to-use portal:

**Penetration Testing** -- Our team of certified security researchers conduct thorough assessments of your web applications, mobile apps, networks, and cloud infrastructure. You receive detailed findings with clear remediation guidance, and you can track every issue from discovery through verification -- all inside your portal.

**Bug Bounty Programs** -- Catchify manages a vetted community of security researchers who continuously test your applications for vulnerabilities. You only pay for valid, verified findings. Our triage team reviews every submission before it reaches you, so you can focus on what matters.

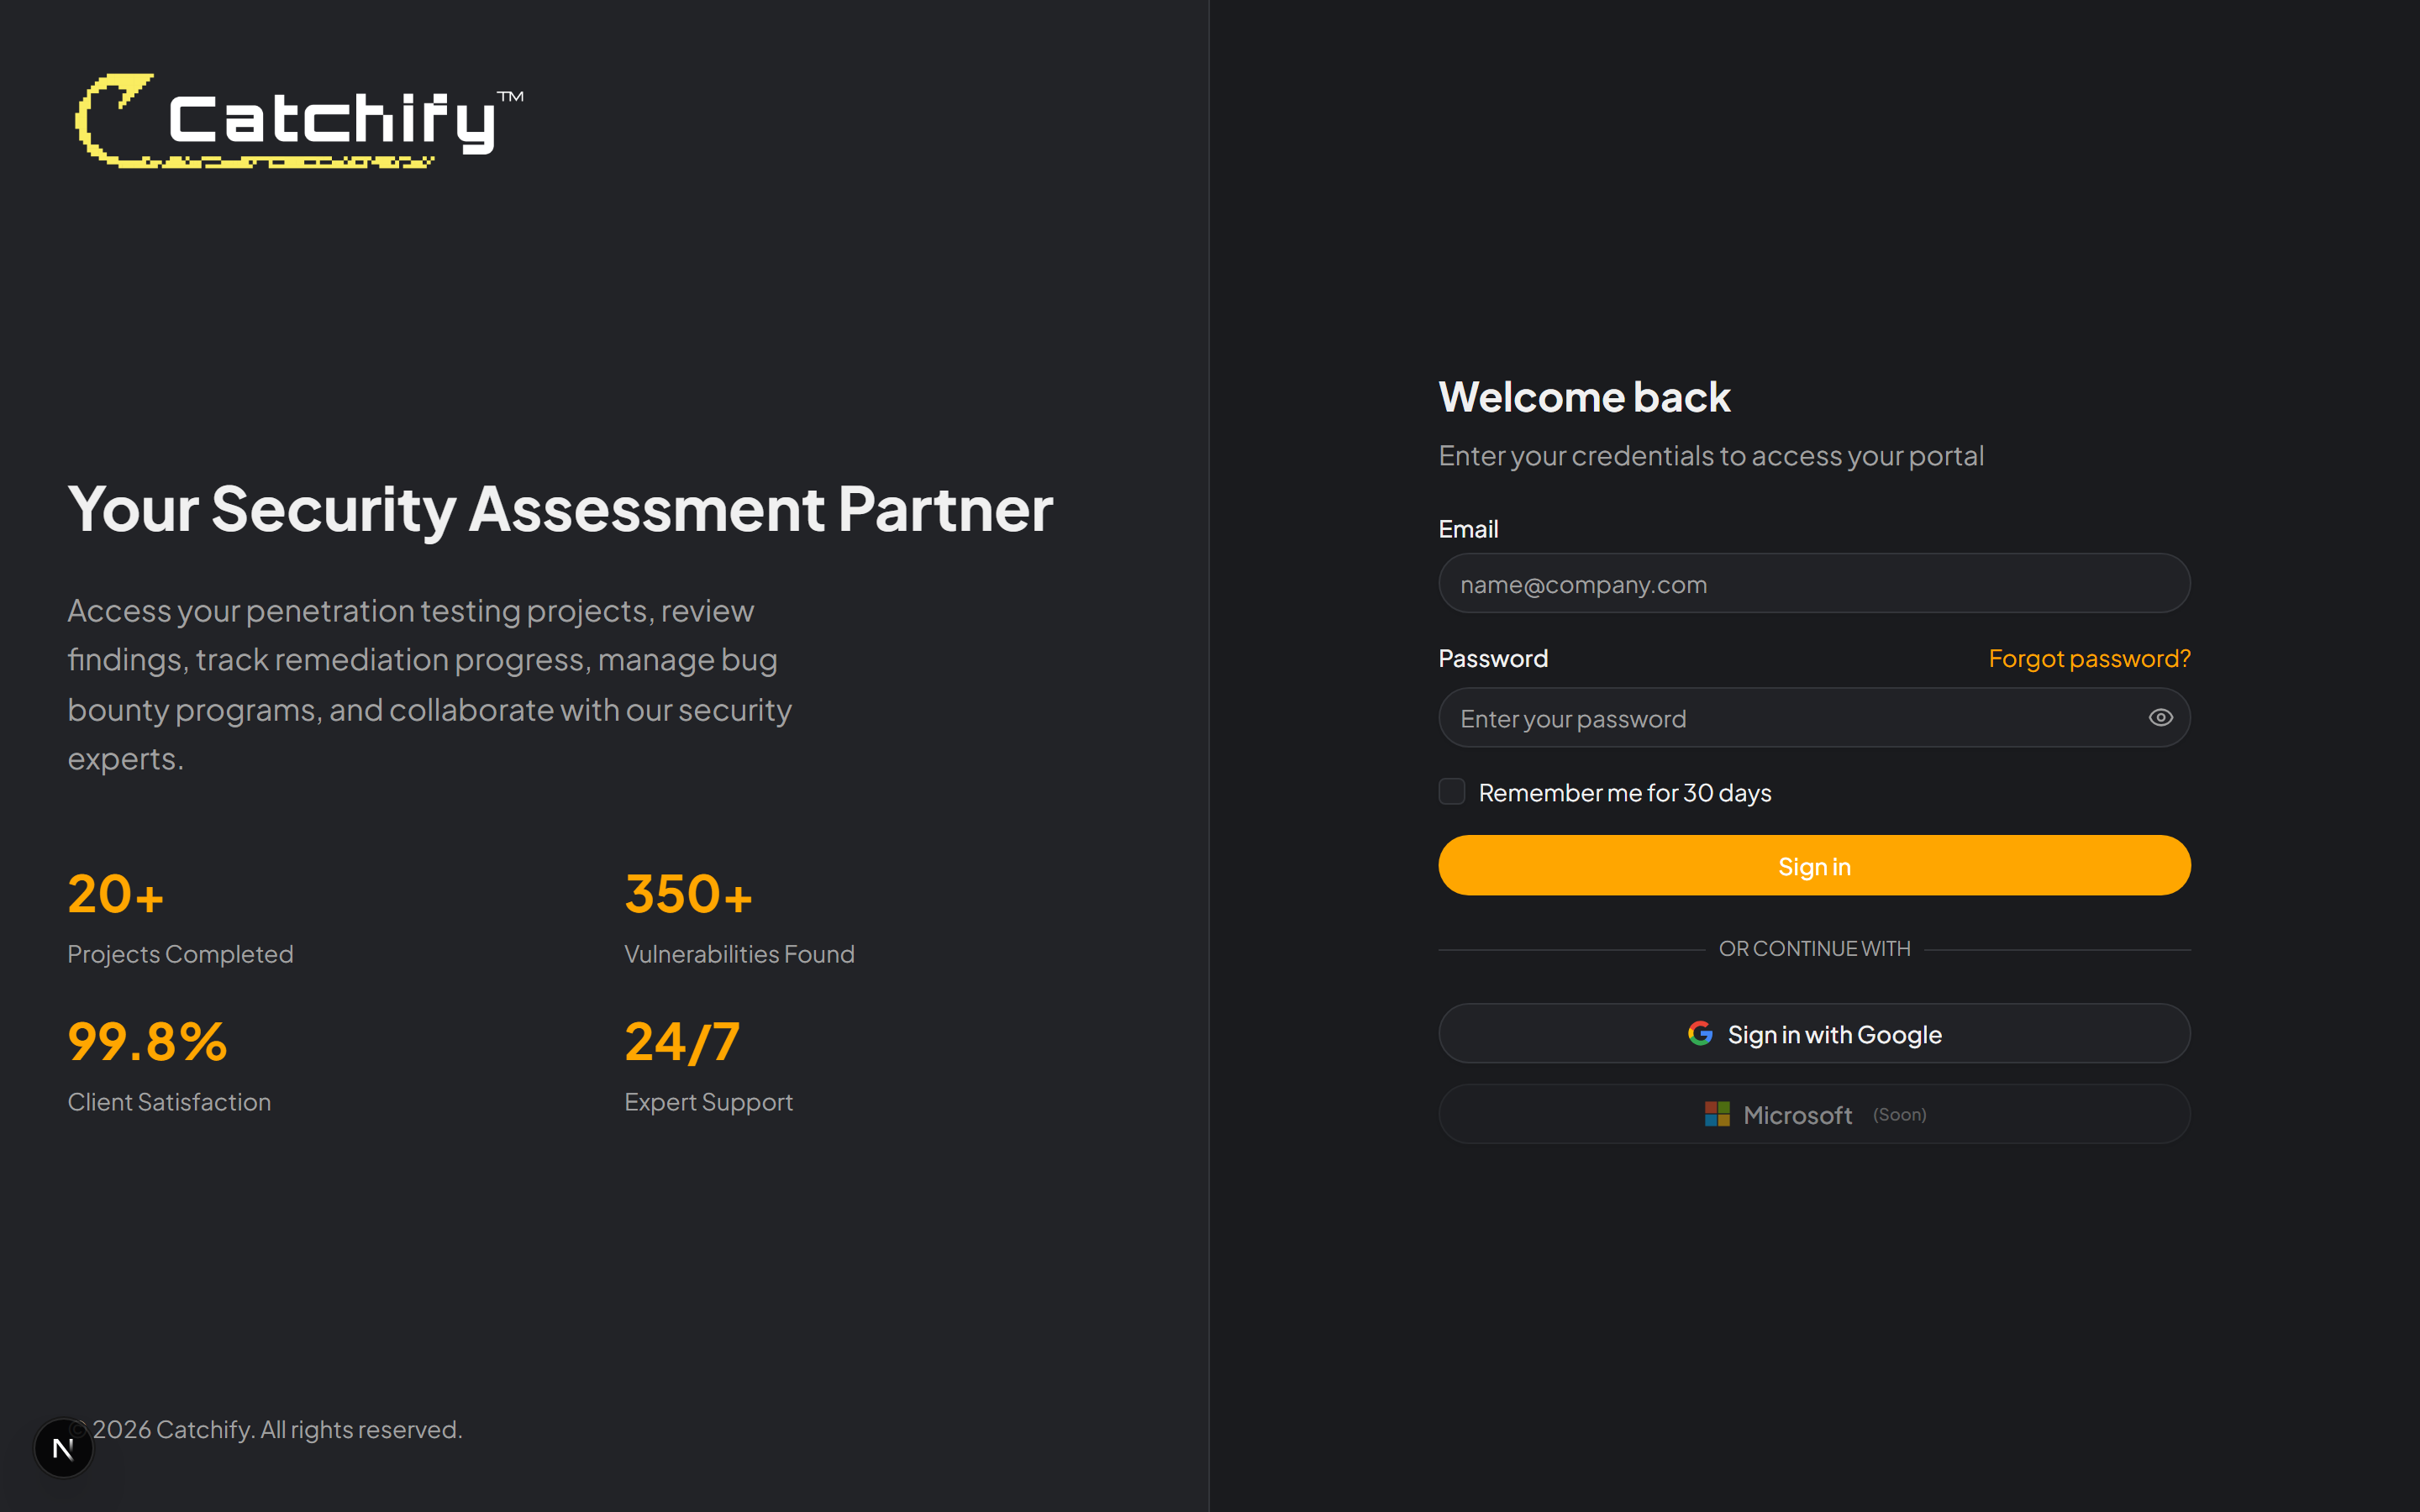
<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-cae53e1697b13504099eae538f5be1ba0989fee7%2Flogin-page.png?alt=media" alt="Catchify client portal login page"><figcaption><p>Your gateway to Catchify -- the client portal at portal.catchify.sa</p></figcaption></figure>

## What This Guide Covers

This guide walks you through everything you need to know as a Catchify client. You will learn how to:

* Navigate your dashboard and understand your security posture
* View and manage penetration testing projects and findings
* Set up and manage a bug bounty program
* Request quotes, view invoices, and manage payments
* Invite your team members and configure their permissions
* Connect Catchify with your existing tools like Slack and Jira

## Your Data, Hosted in Saudi Arabia

All Catchify infrastructure is hosted in Dammam, Saudi Arabia, ensuring your data stays within the Kingdom. Our platform is designed to meet local regulatory requirements and data residency standards.

## Getting Started

If you already have an account, head to [portal.catchify.sa](https://portal.catchify.sa) to log in.

If you are new to Catchify, start with [Creating Your Account](/catchify-platform-documentation/getting-started/creating-your-account) to get set up in just a few minutes.

{% hint style="info" %}
Need help at any point? Reach out to your account manager or email us at <info@catchify.sa> -- we are here to help.
{% endhint %}


# Creating Your Account

Getting started with Catchify takes just a few minutes. Your account is created either through an invitation from your organization or directly by the Catchify team as part of your onboarding.

## How You Get Access

There are two ways your account can be created:

**Invitation from your organization** -- If your company already uses Catchify, a team manager can invite you directly from the portal. You will receive an email with a link to set up your account.

**Set up by the Catchify team** -- When your organization first signs up with Catchify, our team will create your initial admin account and send you a welcome email with login instructions.

## Setting Up Your Account

1. Open the invitation email from Catchify (check your spam folder if you do not see it within a few minutes)
2. Click the **Set Up Your Account** button in the email
3. You will be taken to the registration page at [portal.catchify.sa](https://portal.catchify.sa)
4. Fill in your details:
   * **Full name** -- Your first and last name
   * **Email address** -- This will be pre-filled from your invitation
   * **Password** -- Choose a strong password with at least 8 characters, including uppercase, lowercase, numbers, and special characters
   * **Confirm password** -- Re-enter your password to confirm
5. Click **Create Account**

## Verifying Your Email

After creating your account, you will need to verify your email address:

1. Check your inbox for a verification email from Catchify
2. Click the **Verify Email** button in the email
3. You will be redirected to the portal with a confirmation that your email has been verified
4. You can now log in to your account

{% hint style="warning" %}
The verification link expires after 24 hours. If it has expired, go to the login page and request a new verification email.
{% endhint %}

## What Happens Next

Once your account is verified, you can log in and start using the portal right away. Depending on your role, you may see:

* **Your dashboard** with an overview of your organization's security posture
* **Active projects** if penetration testing engagements are already underway
* **Bug bounty programs** if your organization has an active program

{% hint style="info" %}
We strongly recommend setting up two-factor authentication right after your first login. See [Setting Up Two-Factor Authentication](/catchify-platform-documentation/getting-started/two-factor-authentication) for a quick walkthrough.
{% endhint %}

## Trouble Getting Started?

If you did not receive an invitation email, or if you are having trouble creating your account, contact your account manager or email us at <support@catchify.sa>. We will get you up and running quickly.


# Logging In

Your Catchify client portal is available at [portal.catchify.sa](https://portal.catchify.sa). You can access it from any modern web browser on your computer, tablet, or phone.

## How to Log In

1. Open your browser and go to [portal.catchify.sa](https://portal.catchify.sa)
2. Enter your **email address**
3. Enter your **password**
4. Click **Sign In**

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-cae53e1697b13504099eae538f5be1ba0989fee7%2Flogin-page.png?alt=media" alt="Catchify client portal login page with email and password fields"><figcaption><p>The login page at portal.catchify.sa</p></figcaption></figure>

If you have two-factor authentication enabled (and we recommend you do), you will be prompted to enter a verification code from your authenticator app after entering your password.

## Staying Signed In

Your session will remain active while you are using the portal. For security, you will be automatically signed out after a period of inactivity. Simply log in again when you return.

## Forgot Your Password?

If you have forgotten your password, you can reset it in a few steps:

1. On the login page, click **Forgot Password?**
2. Enter the email address associated with your account
3. Click **Send Reset Link**
4. Check your email for a password reset link
5. Click the link and enter your new password
6. Log in with your new password

{% hint style="warning" %}
Password reset links expire after 1 hour. If yours has expired, simply request a new one from the login page.
{% endhint %}

## Browser Recommendations

Catchify works best on the latest versions of:

| Browser         | Minimum Version |
| --------------- | --------------- |
| Google Chrome   | 90+             |
| Mozilla Firefox | 90+             |
| Microsoft Edge  | 90+             |
| Safari          | 14+             |

{% hint style="info" %}
For the best experience, we recommend using Google Chrome or Microsoft Edge with JavaScript enabled.
{% endhint %}

## Having Trouble Logging In?

If you are unable to log in, here are a few things to check:

* **Incorrect password** -- Make sure Caps Lock is not turned on. Passwords are case-sensitive.
* **Account not verified** -- If you have not verified your email address, check your inbox for the verification email.
* **Account locked** -- After multiple failed login attempts, your account may be temporarily locked for security. Wait a few minutes and try again.
* **Still stuck?** -- Contact us at <support@catchify.sa> and we will help you regain access.


# Setting Up Two-Factor Authentication

Two-factor authentication (2FA) adds an extra layer of security to your Catchify account. With 2FA enabled, you need both your password and a time-based verification code from your phone to log in -- so even if someone learns your password, they cannot access your account without your phone.

## Why You Should Enable 2FA

Your Catchify portal contains sensitive security information about your organization's vulnerabilities and testing results. Enabling 2FA helps ensure that only authorized people can access this data. We strongly recommend that every team member enable 2FA on their account.

{% hint style="warning" %}
If your organization has a security policy that requires 2FA, your account manager can enforce it for all team members. Contact the Catchify team to learn more.
{% endhint %}

## What You Need

Before you begin, download an authenticator app on your phone. Any of these apps will work:

| App                     | Available On          |
| ----------------------- | --------------------- |
| Google Authenticator    | iOS, Android          |
| Microsoft Authenticator | iOS, Android          |
| Authy                   | iOS, Android, Desktop |

## Setting Up 2FA

1. Log in to your account at [portal.catchify.sa](https://portal.catchify.sa)
2. Click on your **profile icon** in the top-right corner
3. Select **Settings** from the dropdown menu
4. Find the **Two-Factor Authentication** section
5. Click **Enable 2FA**
6. A QR code will appear on your screen
7. Open your authenticator app on your phone
8. Tap the **+** button to add a new account
9. Scan the QR code displayed on your screen
10. Your authenticator app will now show a 6-digit code that refreshes every 30 seconds
11. Enter the 6-digit code from your authenticator app into the verification field on the portal
12. Click **Verify and Enable**
13. You will see a confirmation that 2FA has been enabled

{% hint style="success" %}
Your account is now protected with two-factor authentication. Each time you log in, you will be asked for a code from your authenticator app after entering your password.
{% endhint %}

## Logging In with 2FA

Once 2FA is enabled, your login process will look like this:

1. Go to [portal.catchify.sa](https://portal.catchify.sa) and enter your email and password
2. You will be prompted to enter your 2FA code
3. Open your authenticator app and find the Catchify entry
4. Enter the current 6-digit code
5. Click **Verify** to complete your login

## Lost Access to Your Authenticator App?

If you lose your phone or no longer have access to your authenticator app, you can regain access to your account:

1. On the 2FA prompt screen, click **Need help?**
2. Contact the Catchify support team at <support@catchify.sa>
3. After verifying your identity, the Catchify team will reset your 2FA so you can set it up again with a new device

{% hint style="info" %}
To avoid being locked out, consider setting up your authenticator on a second device or using an authenticator app like Authy that supports cloud backup.
{% endhint %}

## Disabling 2FA

If you need to turn off two-factor authentication (for example, when switching phones):

1. Go to **Settings** from your profile menu
2. In the **Two-Factor Authentication** section, click **Disable 2FA**
3. Enter your current 2FA code to confirm
4. 2FA will be removed from your account

We recommend re-enabling it as soon as you have your new device ready.


# Dashboard Overview

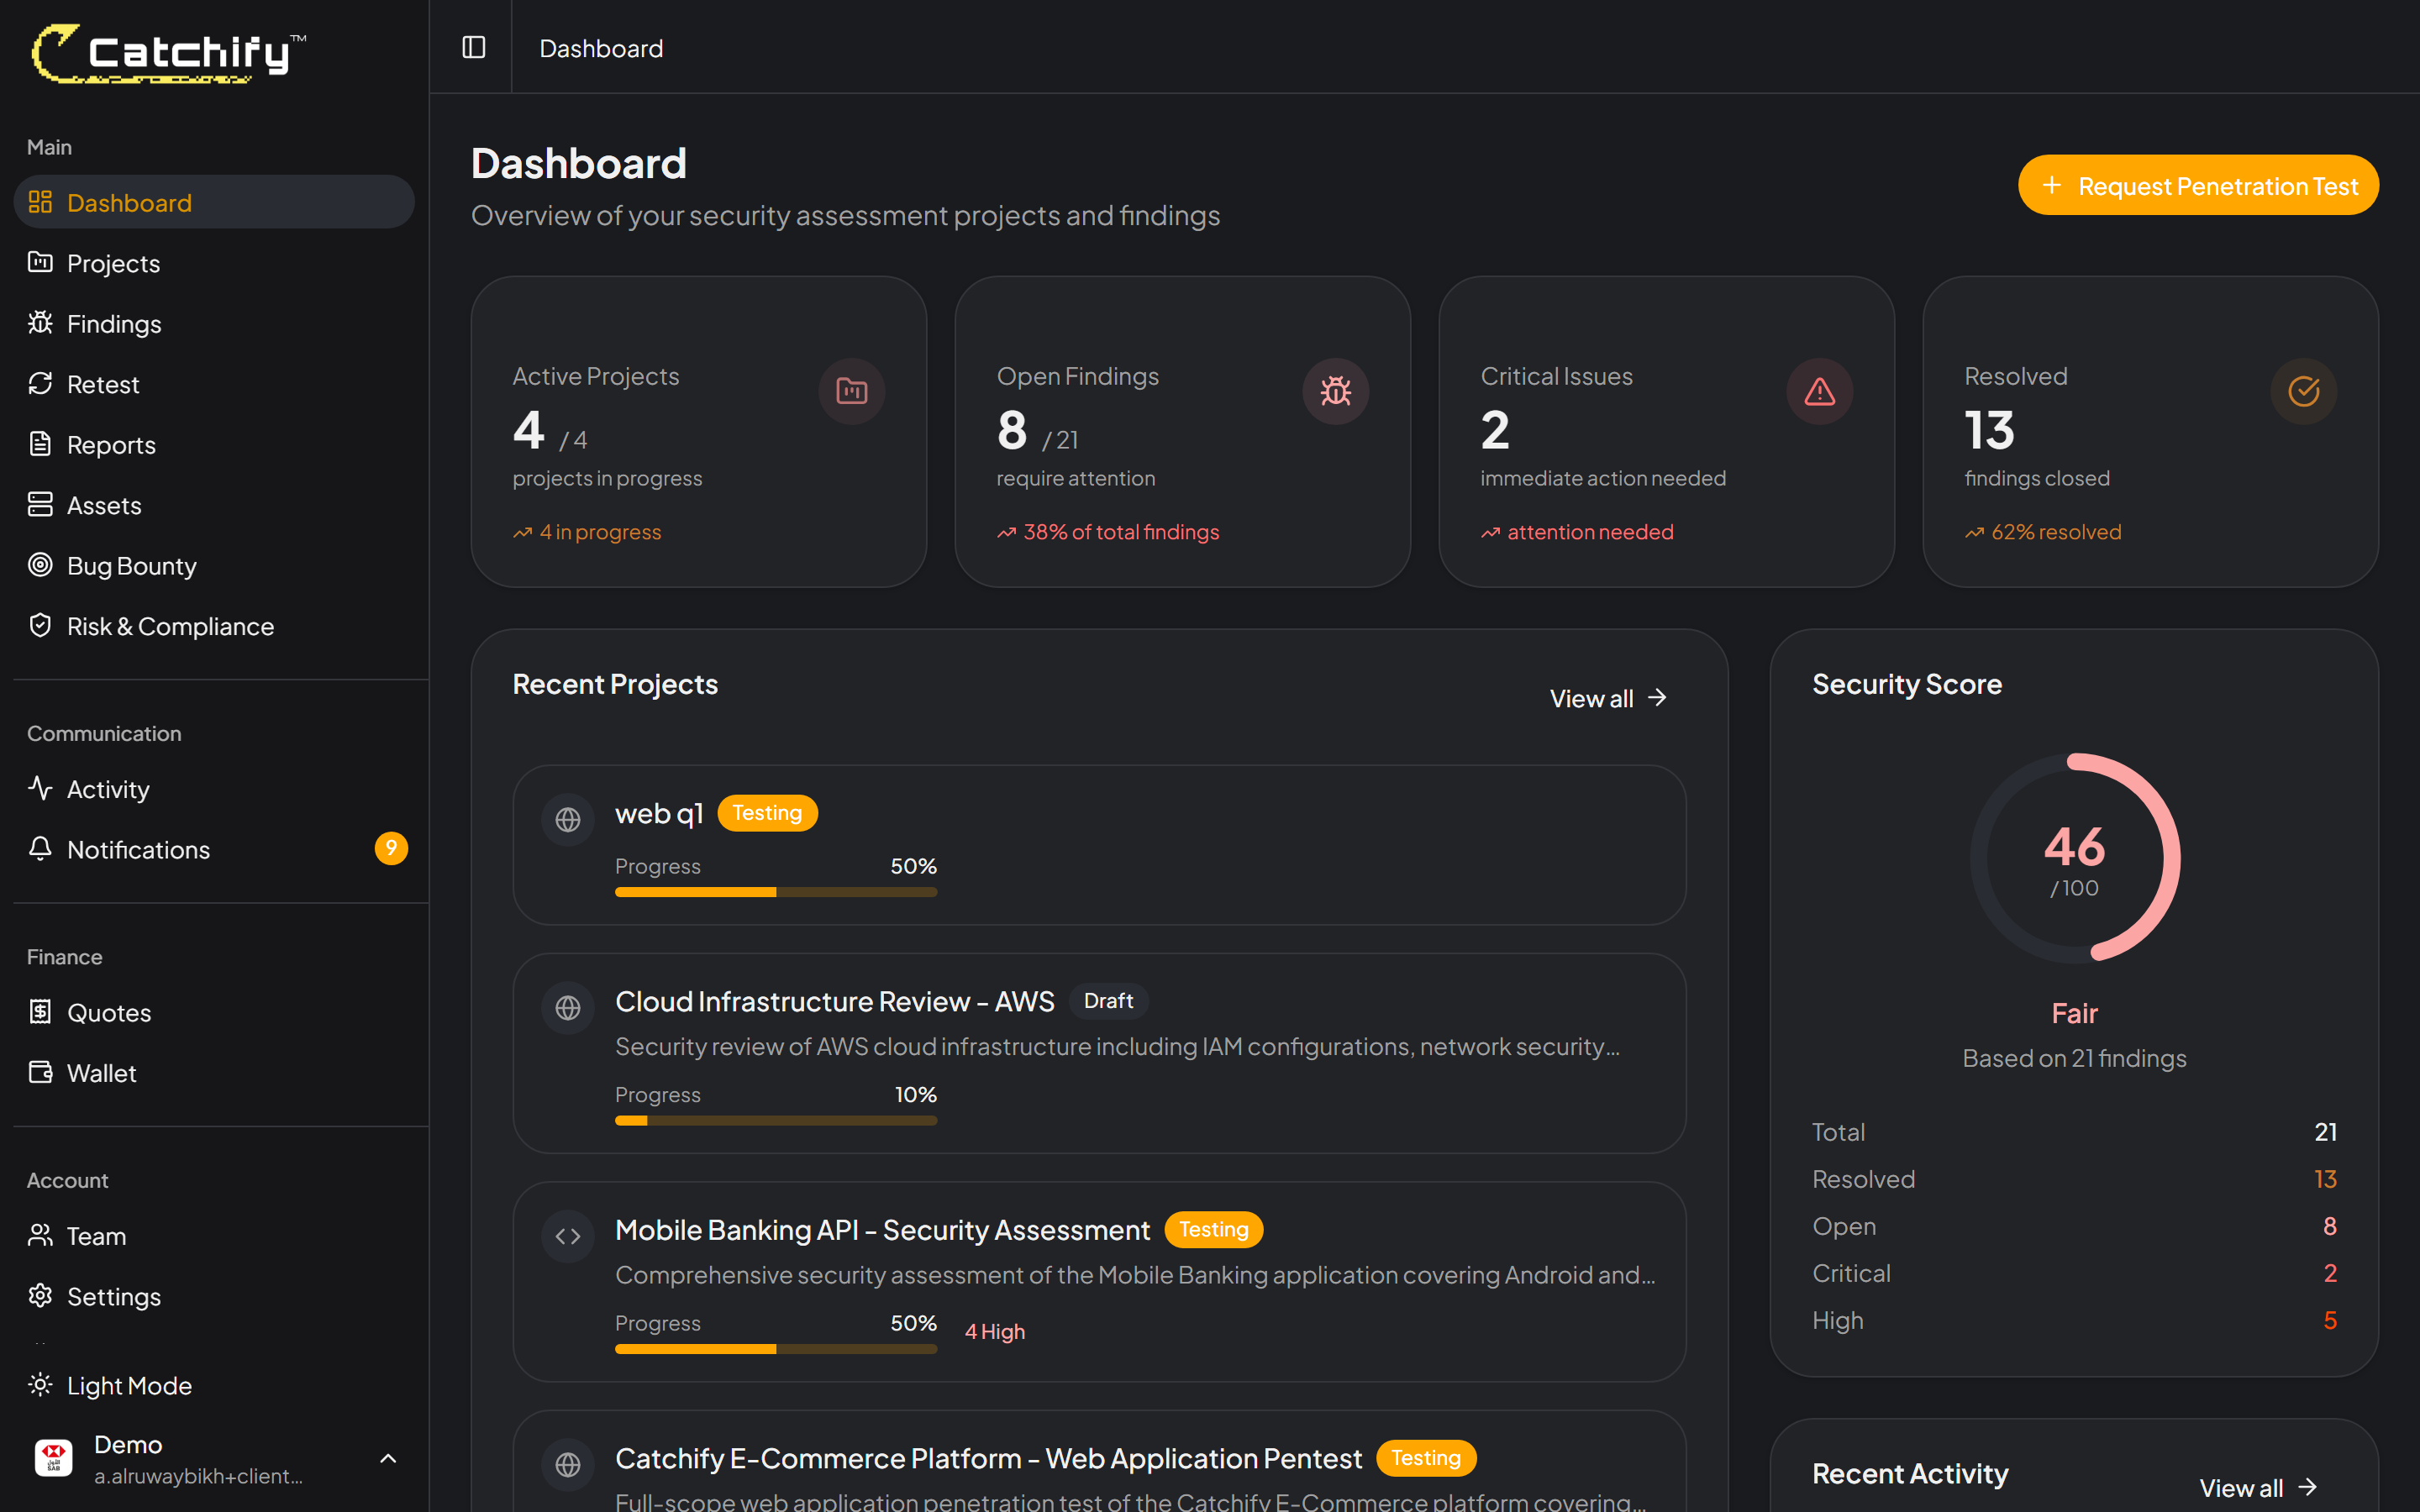
Your dashboard is the first thing you see when you log in to Catchify. It gives you a real-time snapshot of your organization's security posture -- how many vulnerabilities have been found, what their severity is, and what needs your attention right now.

## What You Will See

The dashboard is organized into several sections, each designed to give you quick insight into your security testing program.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-a0d9501b6fa06ca757e057197294b7f1587eb04c%2Fdashboard-overview.png?alt=media" alt="Dashboard overview showing security metrics and charts"><figcaption><p>Your dashboard at a glance -- key metrics, severity breakdown, and recent activity</p></figcaption></figure>

### Summary Cards

At the top of the dashboard, you will find summary cards that show your most important numbers:

| Card                  | What It Means                                                                                 |
| --------------------- | --------------------------------------------------------------------------------------------- |
| **Total Findings**    | The total number of security vulnerabilities discovered across all your projects and programs |
| **Open Findings**     | Findings that have not been resolved yet and still need attention                             |
| **Critical Findings** | The most severe vulnerabilities that require immediate action                                 |
| **Closed Findings**   | Findings that have been fixed and verified by the Catchify team                               |

{% hint style="warning" %}
If you see any critical findings on your dashboard, we recommend addressing them as soon as possible. Critical vulnerabilities represent the highest level of risk to your organization.
{% endhint %}

### Severity Distribution Chart

Below the summary cards, you will see a chart that breaks down your findings by severity level. This visual helps you understand the overall risk profile at a glance:

* **Critical** -- shown in red
* **High** -- shown in orange
* **Medium** -- shown in yellow
* **Low** -- shown in blue
* **Informational** -- shown in gray

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-a0d9501b6fa06ca757e057197294b7f1587eb04c%2Fdashboard-overview.png?alt=media" alt="Severity distribution chart showing findings broken down by severity level"><figcaption><p>Your findings broken down by severity -- aim to keep the critical and high numbers low</p></figcaption></figure>

### Active Projects and Programs

The dashboard also shows your currently active engagements:

* **Active Pentest Projects** -- Penetration tests that are currently in progress, along with their status and timeline
* **Bug Bounty Programs** -- Your active bug bounty programs with recent submission counts

### Recent Activity

At the bottom of your dashboard, you will find a feed of the latest activity across your account. This includes new findings, status changes, comments from the Catchify team, and report submissions.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-a0d9501b6fa06ca757e057197294b7f1587eb04c%2Fdashboard-overview.png?alt=media" alt="Recent activity feed showing latest findings and updates"><figcaption><p>Stay up to date with the latest activity across your projects</p></figcaption></figure>

## Navigating from the Dashboard

Your dashboard is a starting point. Click on any metric card, project name, or activity item to dive deeper:

* Click a **summary card** to view the filtered list of findings
* Click a **project name** to see its full details
* Click an **activity item** to go directly to the relevant finding or report

## Refreshing Your Data

The dashboard updates automatically when you load the page. If you have been on the page for a while and want to see the latest data, simply refresh your browser.

{% hint style="info" %}
The numbers on your dashboard reflect all projects and programs your account has access to. If you manage multiple teams or business units, you will see a combined view. Use the filters on individual pages to narrow down by project.
{% endhint %}


# Security Score

Your security score provides a simple, easy-to-understand measure of how well your organization is managing its security vulnerabilities. It takes into account the findings from both penetration testing and bug bounty programs to give you a single number that reflects your overall security health.

## How the Score Works

Your security score is displayed as a number from 0 to 100, where a higher score means a stronger security posture. The score is calculated based on several factors:

* **How many findings are open** -- Fewer open findings means a higher score
* **The severity of open findings** -- Critical and high-severity findings have a bigger impact on your score than low or informational ones
* **How quickly you fix findings** -- Organizations that resolve findings faster tend to have higher scores
* **Retest results** -- Findings that are fixed and verified by the Catchify team contribute positively to your score

## What Your Score Means

| Score Range | Rating            | What It Means                                                                                             |
| ----------- | ----------------- | --------------------------------------------------------------------------------------------------------- |
| 90 -- 100   | Excellent         | Very few open findings, especially critical or high ones. Your team is resolving issues quickly.          |
| 75 -- 89    | Good              | Most findings are being addressed in a timely manner. A few items may need attention.                     |
| 50 -- 74    | Needs Improvement | There are a significant number of unresolved findings. Focus on addressing high and critical items first. |
| Below 50    | At Risk           | Many serious findings remain unresolved. We recommend prioritizing remediation immediately.               |

## How to Improve Your Score

Improving your security score comes down to addressing findings efficiently. Here are the most effective steps:

1. **Prioritize critical and high findings first** -- These have the largest impact on your score. Work with your development team to fix them as soon as possible.
2. **Request retests after fixing issues** -- Once your team has fixed a vulnerability, request a retest through the portal so the Catchify team can verify the fix. Verified fixes boost your score.
3. **Do not ignore informational findings** -- While they have less impact on the score, addressing best-practice recommendations prevents future issues.
4. **Keep your bug bounty program active** -- Continuous testing helps you catch new vulnerabilities early, before they accumulate and lower your score.

{% hint style="info" %}
Your security score updates automatically as findings are opened, resolved, and verified. There is no action needed on your part to trigger a recalculation.
{% endhint %}

## Score History

The security score page also shows how your score has changed over time. This trend line helps you see whether your overall security posture is improving, staying steady, or declining.

## Sharing Your Score

Your security score can be a valuable metric to share with leadership or compliance teams. You can:

* **Download a summary** -- Export a PDF snapshot of your score and its breakdown
* **Include it in reports** -- Your pentest executive summary reports include the security score at the time of the engagement

{% hint style="success" %}
Many Catchify clients include their security score in board presentations and compliance reports as evidence of their ongoing security efforts.
{% endhint %}


# Activity Feed

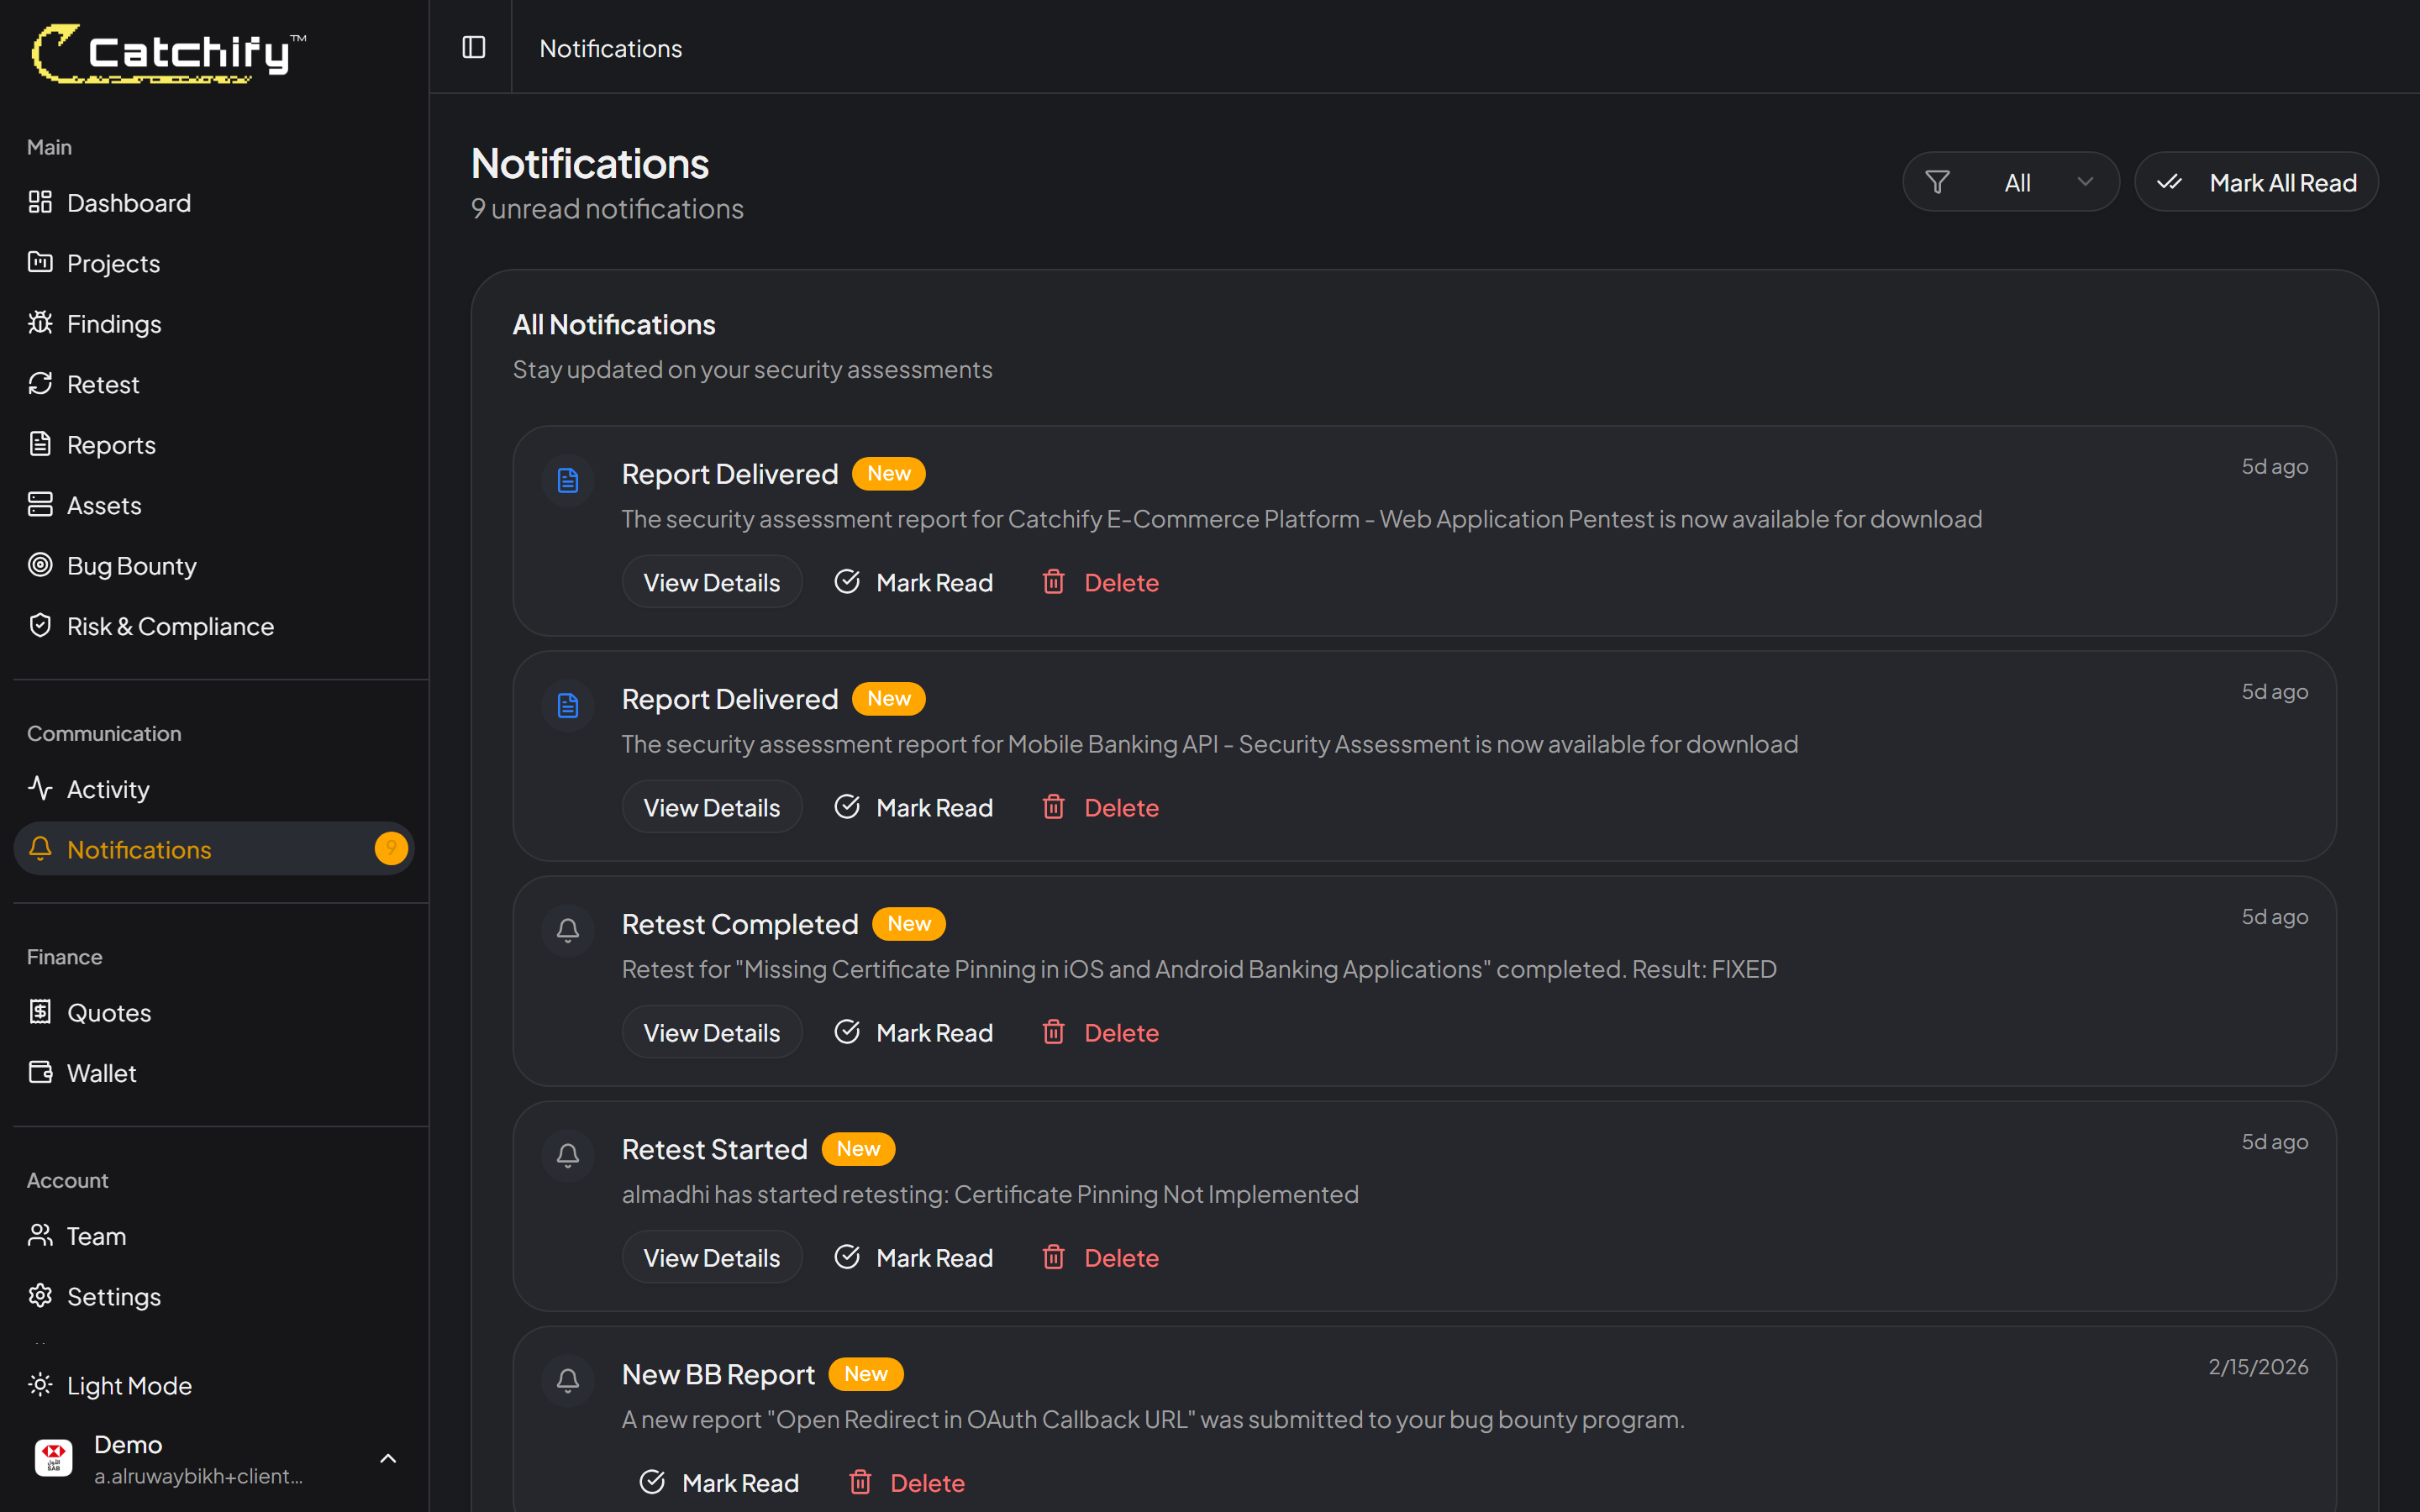
Your activity feed is a chronological log of everything happening across your Catchify account. It helps you stay informed about new findings, status changes, comments, and other important events without having to check each project individually.

## Where to Find It

The activity feed is displayed on your dashboard and can also be accessed from the **Activity** section in the main navigation menu. The dashboard shows the most recent items, while the dedicated Activity page shows the complete history.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-a25ab26e9f3ccbdbdc2a11f6c3395f109c3ad18b%2Fnotifications-page.png?alt=media" alt="Full activity feed page showing chronological list of events"><figcaption><p>Your complete activity feed -- every event across all your projects in one place</p></figcaption></figure>

## What Appears in Your Feed

The activity feed captures events from both penetration testing and bug bounty programs:

| Event Type                 | Description                                                                          |
| -------------------------- | ------------------------------------------------------------------------------------ |
| **New Finding**            | A new security vulnerability has been discovered in one of your projects             |
| **Finding Status Changed** | A finding has moved to a new status (for example, from Open to In Progress)          |
| **Retest Completed**       | The Catchify team has completed a retest on a finding you submitted for verification |
| **New Comment**            | A member of the Catchify team or your own team has added a comment to a finding      |
| **Report Submitted**       | A new bug bounty report has been submitted by a researcher                           |
| **Report Status Changed**  | A bug bounty report has been triaged, confirmed, or resolved                         |
| **Project Started**        | A new penetration testing engagement has begun                                       |
| **Project Completed**      | A penetration test has been completed and the final report is available              |
| **Team Member Added**      | A new team member has joined your organization on Catchify                           |
| **Invoice Created**        | A new invoice has been generated for your account                                    |

## Filtering Your Feed

If you are looking for specific types of events, you can filter the activity feed by:

* **Event type** -- Show only findings, comments, reports, or other specific event types
* **Project** -- Show activity for a particular project or program
* **Date range** -- Narrow down to events from a specific time period

This is especially helpful when you manage multiple projects and want to focus on what is relevant to you right now.

## Notifications

In addition to the activity feed, Catchify sends you notifications for important events. You will see a notification bell in the top-right corner of the portal. A red badge indicates unread notifications.

Click the bell icon to see your latest notifications and quickly jump to the relevant page.

{% hint style="info" %}
Want to receive notifications outside the portal? Connect Catchify to Slack or set up webhook notifications to get updates in your team's communication channels. See the [Integrations](/catchify-platform-documentation/integrations/slack) section for details.
{% endhint %}

## Keeping Your Team Informed

The activity feed is shared across your organization's account. All team members with portal access can see the same events, making it easy to collaborate on security issues without needing separate status meetings or email chains.

{% hint style="success" %}
Review your activity feed regularly -- even a quick daily check helps you stay on top of new findings and ongoing remediation efforts.
{% endhint %}


# Your Projects

The Projects page shows all of your penetration testing engagements with Catchify. Each project represents a testing engagement for a specific application, network, or system -- giving you a clear view of what has been tested, what is in progress, and what is coming up.

## Viewing Your Projects

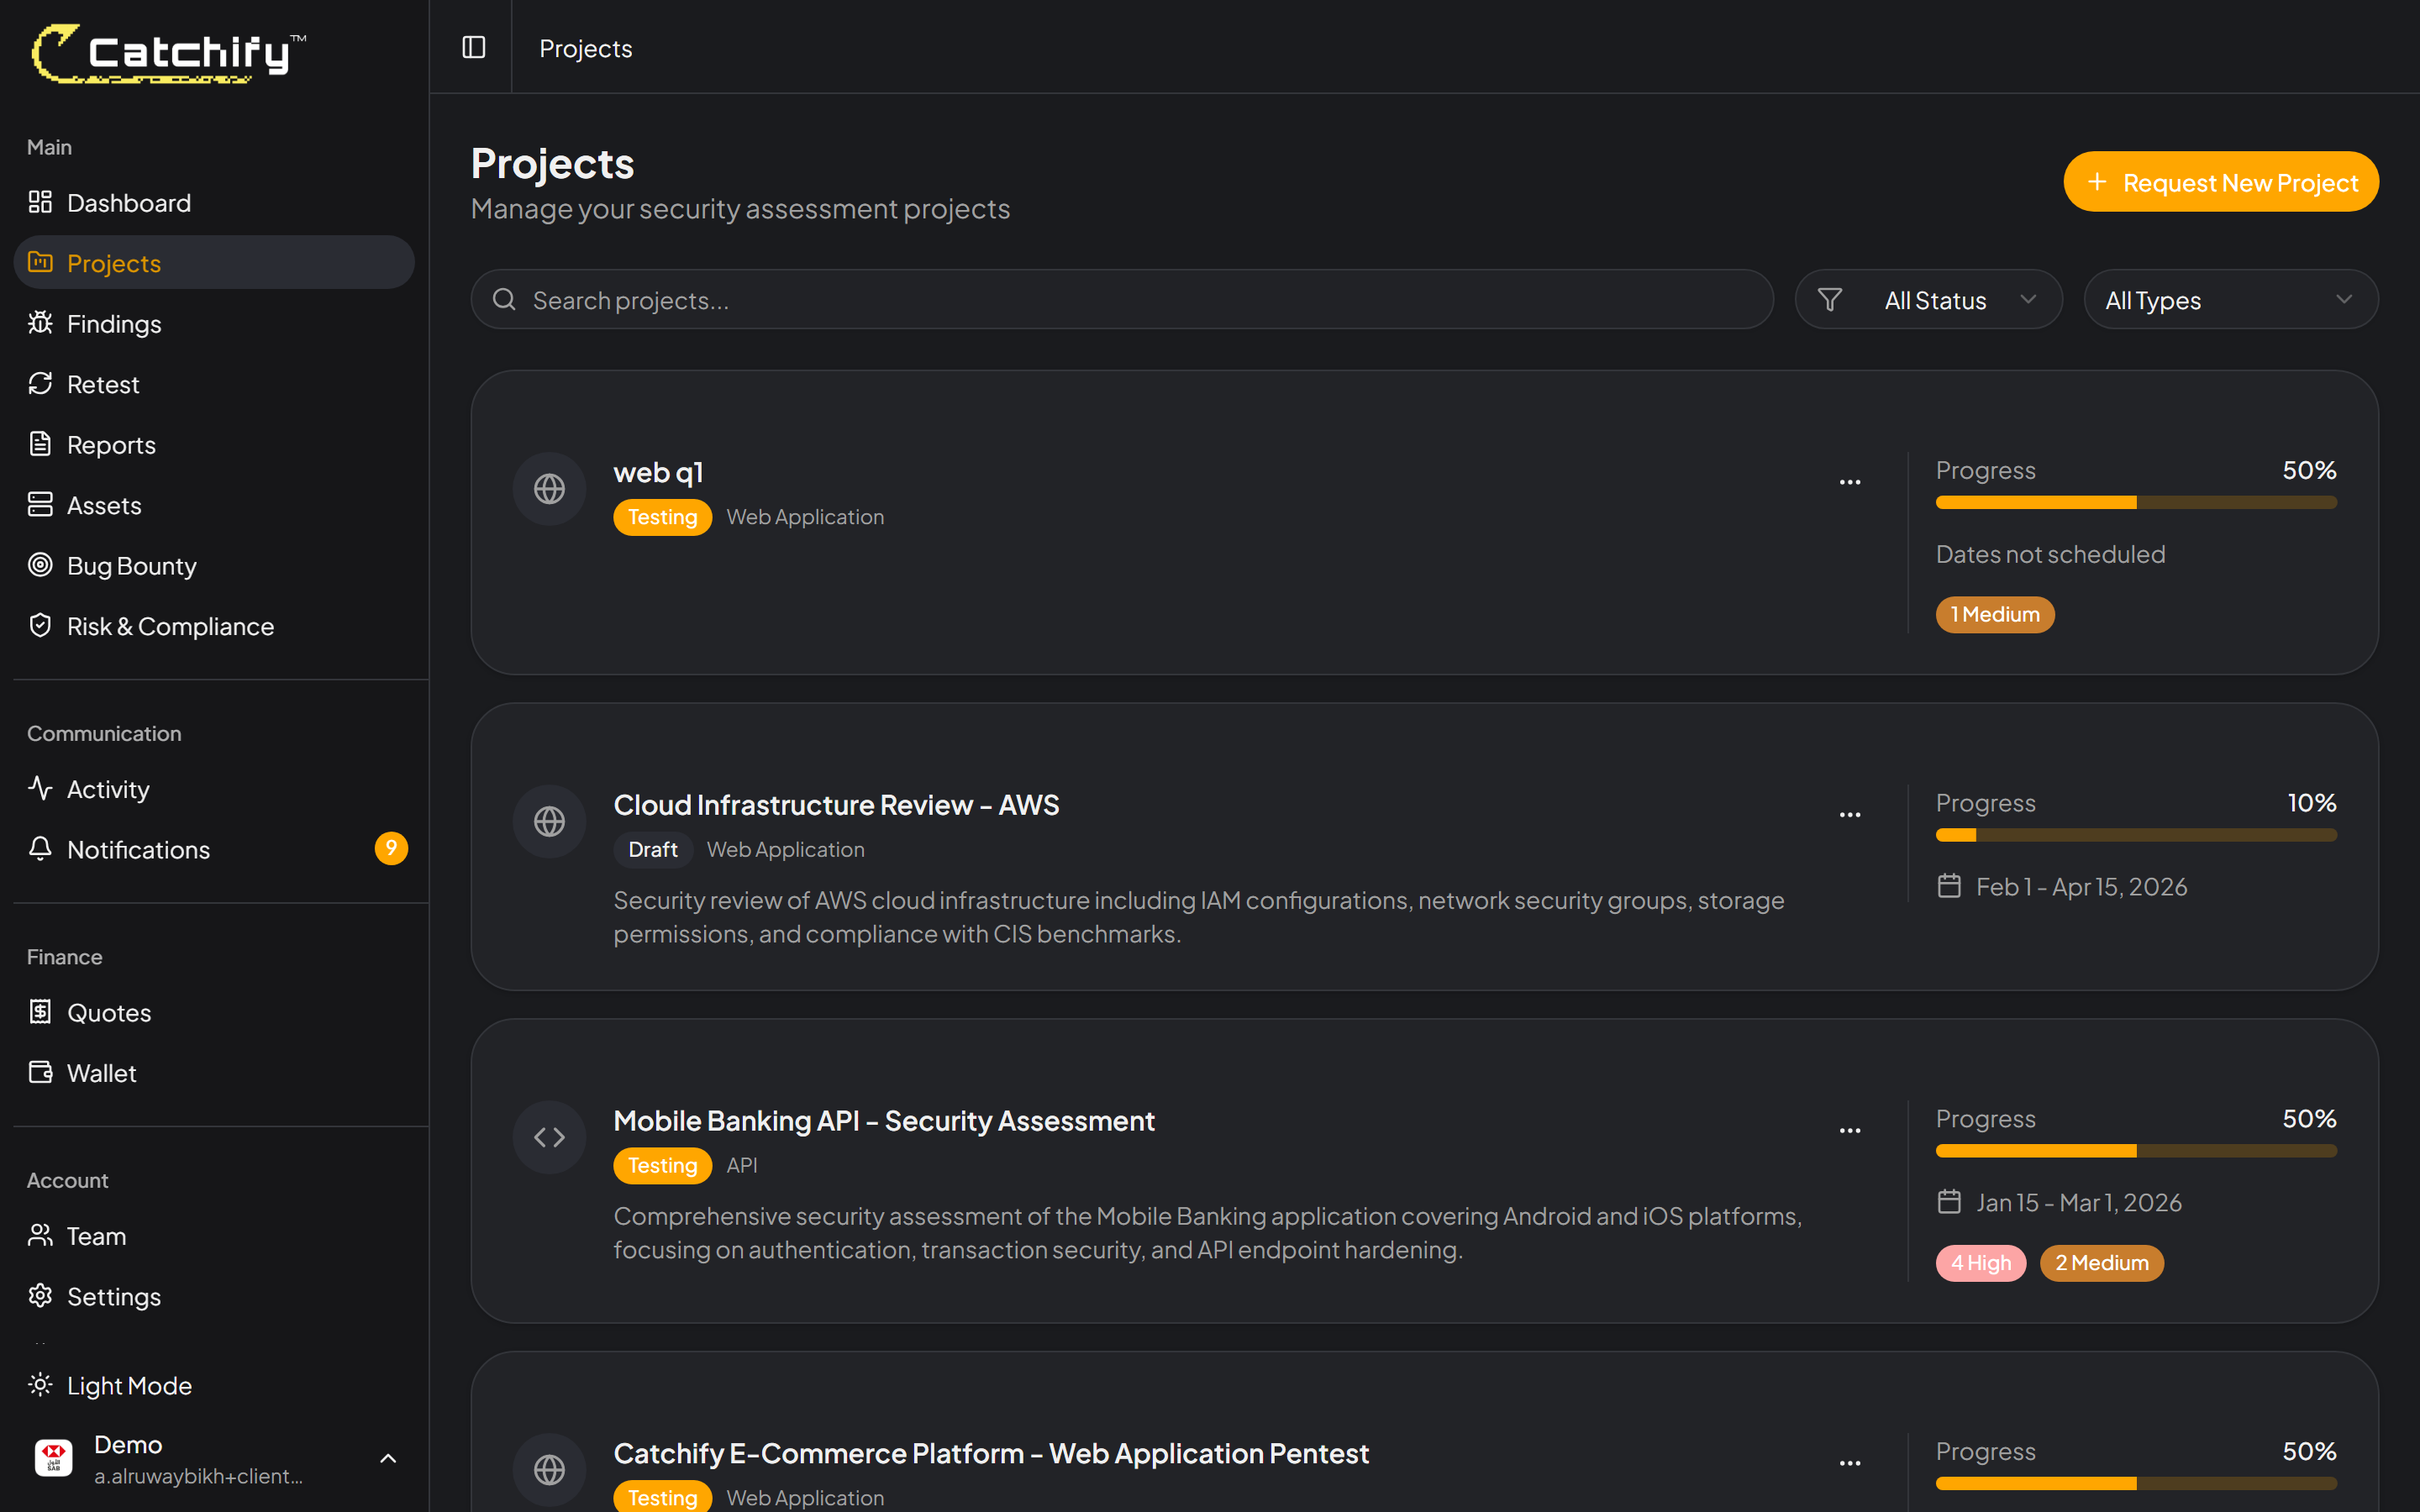
Navigate to **Projects** in the main menu to see a list of all your penetration testing engagements. Each project card shows key information at a glance:

* **Project name** -- The name of the application or system being tested
* **Status** -- Whether the project is pending, active, or completed
* **Start and end dates** -- The testing window for the engagement
* **Finding count** -- How many vulnerabilities have been discovered so far

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-15c911e2ca57c27b169455bb0fe03b8b28ddb777%2Fprojects-list.png?alt=media" alt="List of penetration testing projects showing status and finding counts"><figcaption><p>Your projects page -- see all engagements at a glance</p></figcaption></figure>

## Project Statuses

Each project goes through a defined lifecycle:

| Status        | What It Means                                                                                                       |
| ------------- | ------------------------------------------------------------------------------------------------------------------- |
| **Pending**   | The project has been set up and is waiting for testing to begin. The Catchify team is preparing for the engagement. |
| **Active**    | Our security researchers are currently testing your application. Findings will appear as they are discovered.       |
| **Completed** | Testing is finished. The final report is available for download, and all findings have been documented.             |

{% hint style="info" %}
During an active engagement, you may see new findings appearing in real time. You do not need to wait for the final report to start reviewing and addressing issues.
{% endhint %}

## Project Details

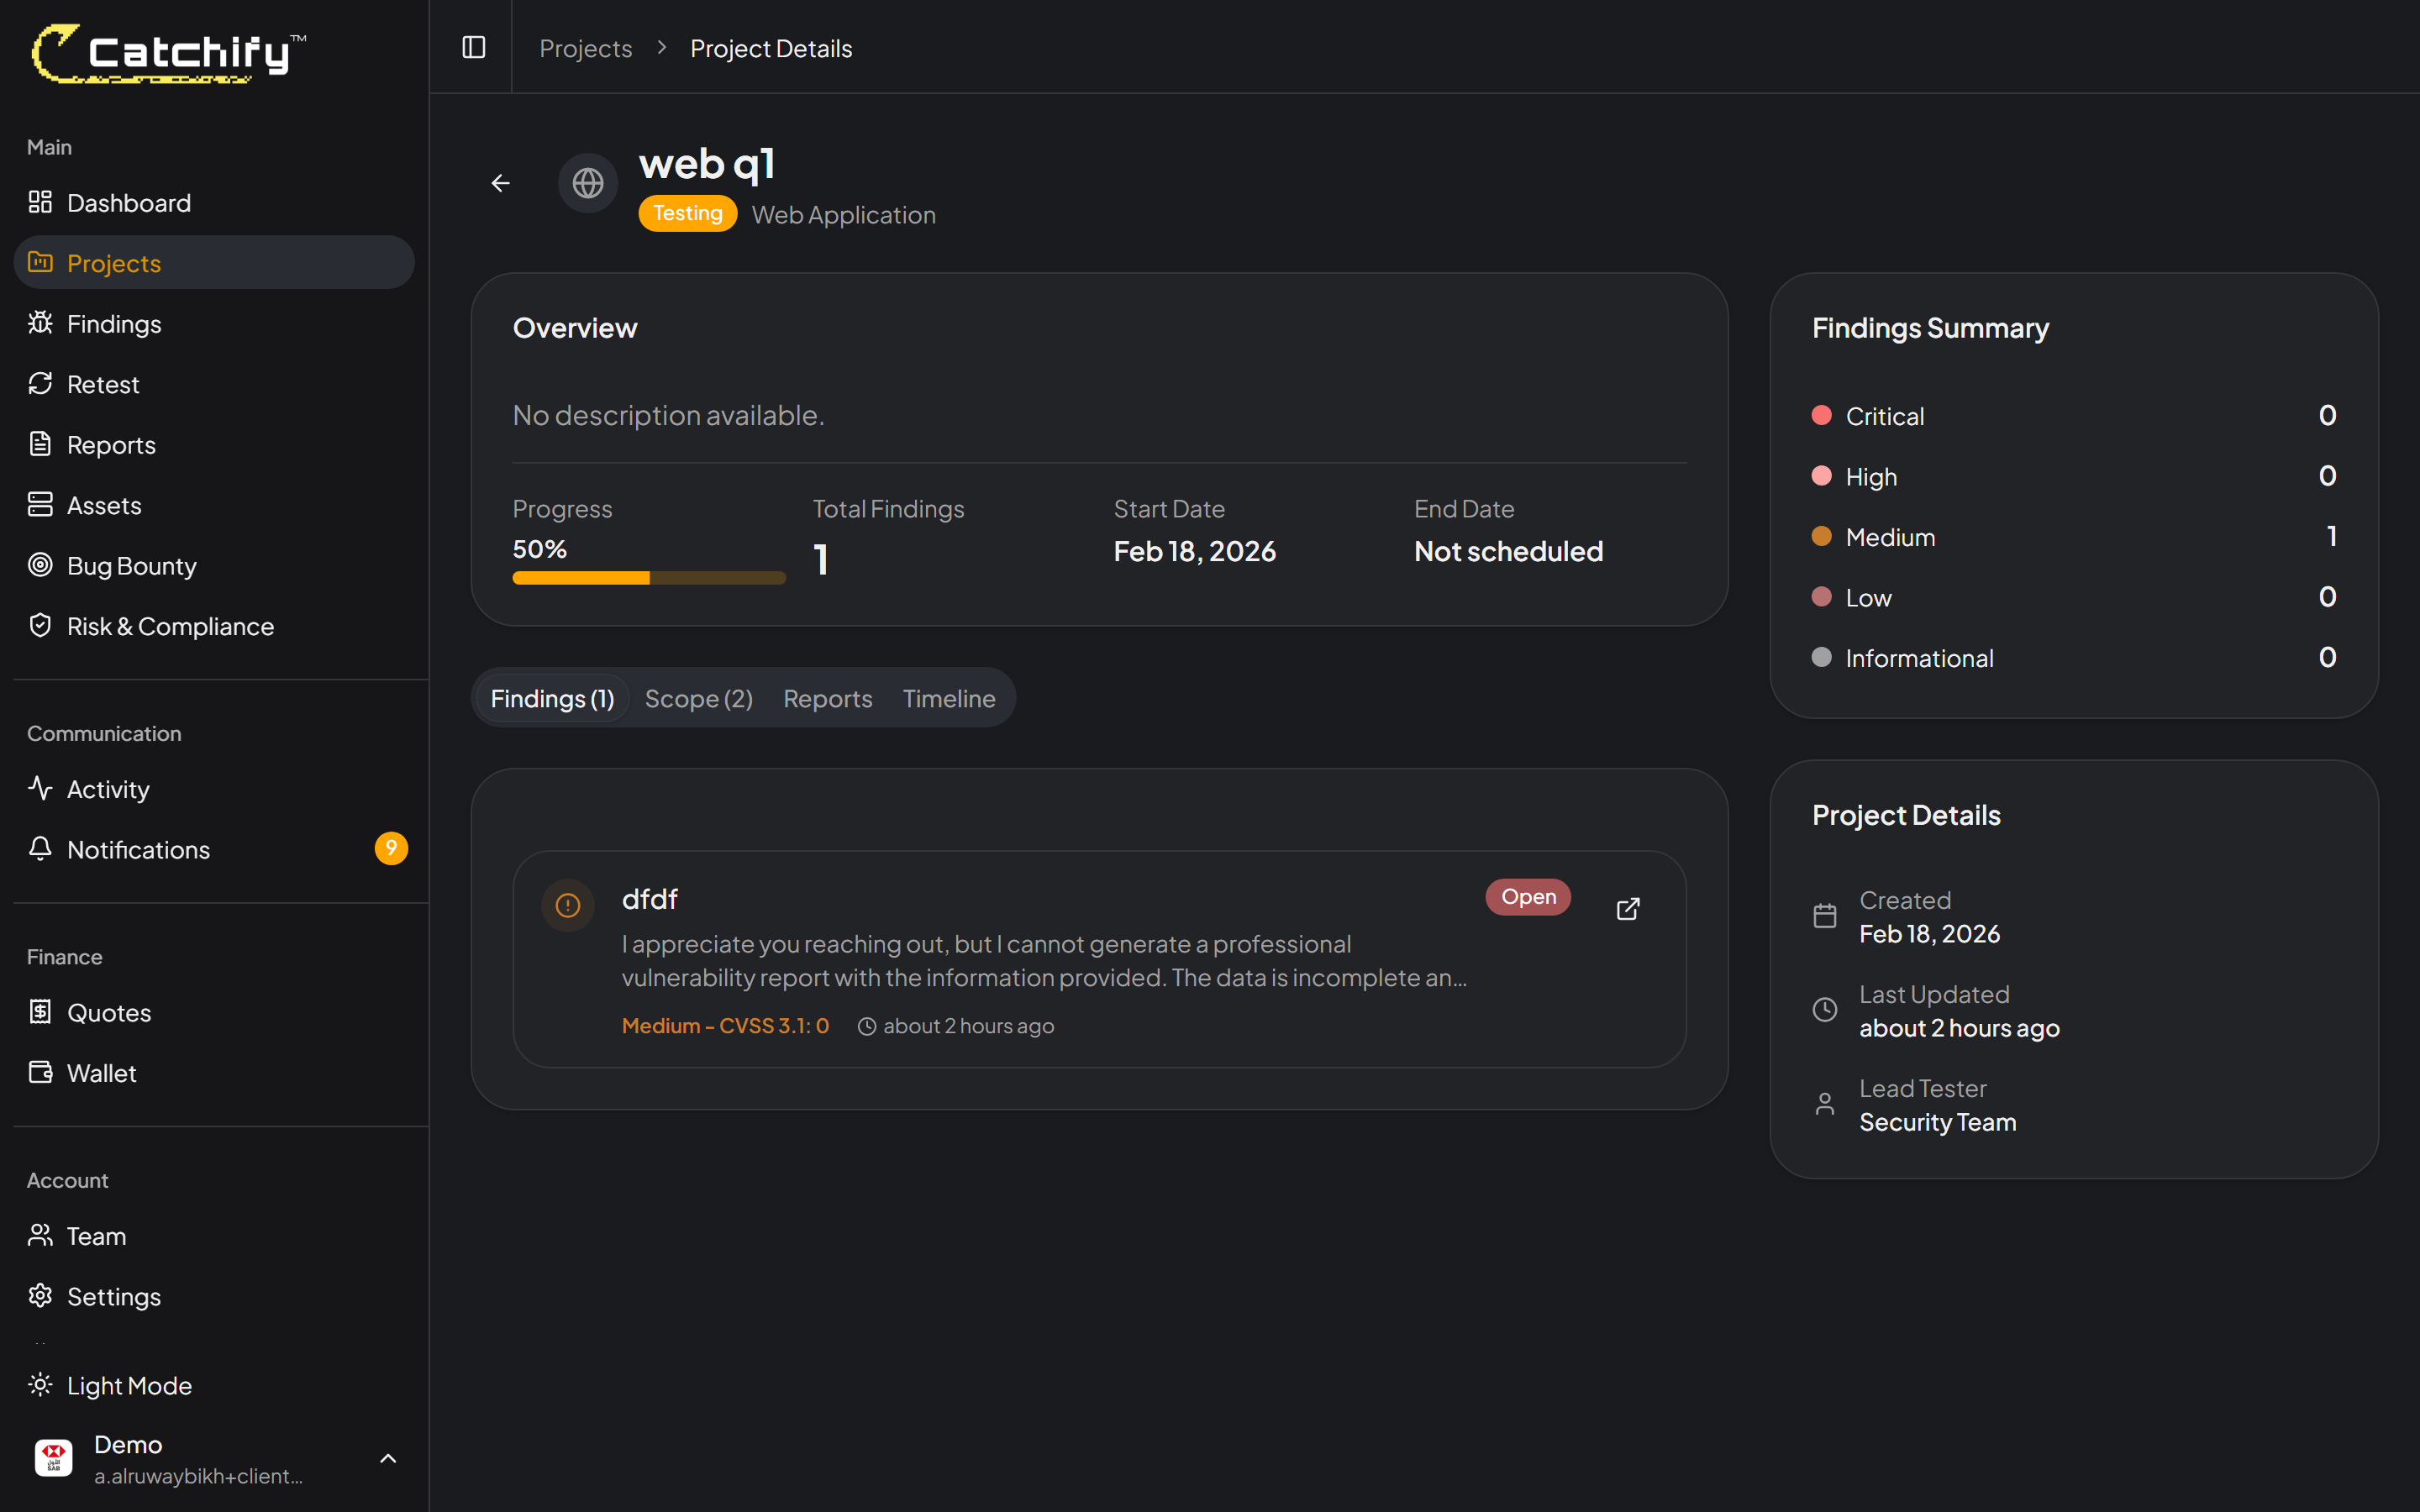
Click on any project to view its full details. The project detail page includes:

### Overview Tab

A summary of the engagement including:

* The scope of testing (which applications, URLs, or systems are being tested)
* The type of testing (web application, mobile, network, cloud)
* The assigned testing team
* Key dates and milestones

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e355c860c197568aa524dc3d5b6321bb8d87693%2Fproject-detail.png?alt=media" alt="Project detail page showing scope, type, and timeline"><figcaption><p>The project overview gives you all the key details of the engagement</p></figcaption></figure>

### Findings Tab

A list of all vulnerabilities discovered during testing. You can:

* Filter findings by severity (Critical, High, Medium, Low, Informational)
* Filter by status (Open, In Progress, Fixed, Verified)
* Search for specific findings by title or description
* Click any finding to see its full details

### Assets Tab

A list of the assets (applications, domains, IP addresses) included in the project scope. This helps you confirm exactly what is being tested.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e355c860c197568aa524dc3d5b6321bb8d87693%2Fproject-detail.png?alt=media" alt="Project findings tab with severity filters and finding list"><figcaption><p>View and filter all findings for a specific project</p></figcaption></figure>

## What to Expect During a Project

Here is what a typical penetration testing engagement looks like from your perspective:

1. **Kickoff** -- The Catchify team will confirm the scope and timeline with you. You may need to provide access credentials or whitelist our testing IP addresses.
2. **Active testing** -- Our security researchers begin testing. You may start seeing findings appear within the first few days.
3. **Findings review** -- As findings come in, you can review them, ask questions by adding comments, and start working on fixes.
4. **Final report** -- Once testing is complete, the Catchify team will deliver a comprehensive report with an executive summary, detailed findings, and remediation recommendations.
5. **Retest** -- After you have fixed the identified issues, you can request a retest to verify the fixes.

{% hint style="success" %}
You do not need to wait until the engagement is over to start fixing issues. Addressing critical and high findings early helps reduce your risk exposure faster.
{% endhint %}

## Need a New Project?

If you would like to schedule a new penetration test, contact your account manager or [request a quote](/catchify-platform-documentation/quotes-and-invoices/requesting-a-quote) through the portal. The Catchify team will work with you to define the scope and timeline.


# Understanding Findings

A finding is a security vulnerability or weakness that our researchers have discovered during testing. Every finding is documented with enough detail for your development team to understand the issue and fix it. This page explains how findings work and how to manage them in the portal.

## What a Finding Contains

When you open a finding, you will see the following information:

* **Title** -- A clear, descriptive name for the vulnerability
* **Severity** -- How serious the issue is (Critical, High, Medium, Low, or Informational). See [Severity Levels Explained](/catchify-platform-documentation/penetration-testing/severity-levels) for details.
* **Status** -- Where the finding is in the resolution process
* **Description** -- A detailed explanation of what the vulnerability is and why it matters
* **Impact** -- What could happen if the vulnerability were exploited by an attacker
* **Steps to reproduce** -- A clear walkthrough showing how the issue can be demonstrated
* **Evidence** -- Screenshots, request/response samples, or other proof that the vulnerability exists
* **Recommendation** -- Guidance on how to fix the issue
* **Affected asset** -- Which application, URL, or system is affected

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7412541663a49bd9dc22317438fedf1afdb932ec%2Ffinding-detail.png?alt=media" alt="Finding detail page showing severity, description, impact, and recommendation"><figcaption><p>A finding detail page -- everything you need to understand and fix the issue</p></figcaption></figure>

## Finding Statuses

Each finding moves through a defined workflow as your team addresses it:

| Status            | What It Means                                                                         |
| ----------------- | ------------------------------------------------------------------------------------- |
| **Open**          | The finding has been identified and is waiting to be addressed by your team           |
| **In Progress**   | Your team is actively working on a fix                                                |
| **Fixed**         | Your team has applied a fix and the finding is ready for verification                 |
| **Verified**      | The Catchify team has confirmed that the fix resolves the issue                       |
| **Accepted Risk** | Your organization has acknowledged the finding but decided not to fix it at this time |

The typical flow is: **Open** --> **In Progress** --> **Fixed** --> **Verified**

{% hint style="info" %}
When you mark a finding as Fixed, you can request a retest so the Catchify team can verify the fix. See [Requesting a Retest](/catchify-platform-documentation/penetration-testing/requesting-retest) for more details.
{% endhint %}

## Browsing Your Findings

The Findings page gives you a complete list of all vulnerabilities across your projects. You can use filters to narrow down what you see:

* **By severity** -- Focus on critical and high findings first
* **By status** -- See only open findings, or review what has been verified
* **By project** -- View findings for a specific engagement
* **Search** -- Find specific findings by keyword

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-0bd249e86c305f1317a5aeef1b124134ece74a4e%2Ffindings-list.png?alt=media" alt="Findings list page with filter options for severity, status, and project"><figcaption><p>Filter and search your findings to focus on what matters most</p></figcaption></figure>

## Adding Comments

You can add comments to any finding to communicate with your team or the Catchify team. Comments are useful for:

* Asking questions about a finding
* Providing context about your environment
* Noting progress on a fix
* Requesting clarification on the recommendation

To add a comment, open the finding and scroll to the **Comments** section at the bottom of the page. Type your message and click **Add Comment**.

## Exporting Findings

You can download your findings in multiple formats for sharing with your team:

* **PDF report** -- A formatted document suitable for management review
* **CSV export** -- A spreadsheet format for tracking and analysis

{% hint style="success" %}
We recommend reviewing new findings within 48 hours of them being reported. The sooner your team starts working on fixes, the shorter your window of exposure.
{% endhint %}

## Working with Your Development Team

Findings are written to be actionable. Share them directly with your developers by:

* Sending them a link to the finding in the portal (if they have access)
* Exporting findings and assigning them in your issue tracker
* Using the [Jira integration](/catchify-platform-documentation/integrations/jira) to automatically create tickets from findings

The combination of detailed descriptions, reproduction steps, and remediation guidance gives your development team everything they need to resolve the issue.


# Severity Levels Explained

Every finding discovered by the Catchify team is assigned a severity level that reflects how serious the vulnerability is and how urgently it should be addressed. Understanding these levels helps you prioritize your remediation efforts and communicate risk to stakeholders.

## The Five Severity Levels

| Severity          | Color  | Risk Level                           | Typical Response Time              |
| ----------------- | ------ | ------------------------------------ | ---------------------------------- |
| **Critical**      | Red    | Immediate threat to your business    | Address within 24-48 hours         |
| **High**          | Orange | Significant security risk            | Address within 1-2 weeks           |
| **Medium**        | Yellow | Moderate risk that should be planned | Address within 1 month             |
| **Low**           | Blue   | Minor issue with limited impact      | Address in your next release cycle |
| **Informational** | Gray   | Best practice recommendation         | Consider for future improvements   |

## Critical

Critical findings represent the most severe vulnerabilities -- issues that could allow an attacker to take full control of a system, access sensitive data, or cause major business disruption with minimal effort.

**Examples of critical findings:**

* An attacker can access your entire database without authentication
* Remote code execution is possible on your servers
* Administrative accounts can be compromised without credentials
* Sensitive customer data (personal information, financial records) is publicly accessible

{% hint style="warning" %}
Critical findings should be treated as emergencies. We recommend mobilizing your team to address these within 24-48 hours of discovery. The Catchify team will highlight critical findings to you immediately.
{% endhint %}

## High

High-severity findings represent significant security risks. While they may require more specific conditions to exploit than critical findings, they still pose a serious threat to your organization.

**Examples of high findings:**

* Stored cross-site scripting (XSS) that could affect other users
* Privilege escalation allowing a regular user to gain admin access
* Sensitive data exposed through insecure configurations
* Authentication bypasses for non-administrative functions

## Medium

Medium-severity findings are genuine security issues that should be addressed, but they typically require more effort or specific conditions to exploit. These are important to fix as part of your ongoing security improvement plan.

**Examples of medium findings:**

* Cross-site request forgery (CSRF) on important actions
* Information disclosure that reveals system details to potential attackers
* Missing security headers that reduce the effectiveness of browser protections
* Session management weaknesses

## Low

Low-severity findings are minor issues with limited direct impact. While they are unlikely to cause significant damage on their own, they may contribute to a larger attack if left unaddressed.

**Examples of low findings:**

* Verbose error messages revealing software versions
* Minor information leaks in HTTP headers
* Weak password policy enforcement
* Non-sensitive cookies without security flags

## Informational

Informational findings are not vulnerabilities in the traditional sense. They are best practice recommendations and observations that can help strengthen your overall security posture.

**Examples of informational findings:**

* Recommendations for adopting newer security standards
* Suggestions for improving logging and monitoring
* Notes about deprecated software that should be upgraded
* Hardening recommendations for server configurations

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-0bd249e86c305f1317a5aeef1b124134ece74a4e%2Ffindings-list.png?alt=media" alt="Example severity distribution showing counts per level"><figcaption><p>A typical severity distribution -- aim to resolve critical and high findings first</p></figcaption></figure>

## How Severity Is Determined

The Catchify team assigns severity levels based on industry-standard frameworks and considers factors such as:

* **Exploitability** -- How easy is it for an attacker to take advantage of this vulnerability?
* **Impact** -- What is the potential damage if the vulnerability is exploited?
* **Scope** -- How much of your environment or data is affected?
* **Required privileges** -- Does the attacker need existing access, or can anyone exploit it?

{% hint style="info" %}
If you disagree with a severity rating or want to discuss it, add a comment on the finding or contact your account manager. The Catchify team is always open to reviewing severity assessments based on your specific business context.
{% endhint %}

## Prioritizing Remediation

When deciding what to fix first, we recommend this approach:

1. **Start with Critical** -- These need immediate attention
2. **Move to High** -- Address these within your next sprint or release cycle
3. **Plan for Medium** -- Include these in your regular development backlog
4. **Schedule Low and Informational** -- Address these as time allows or bundle them into larger improvement efforts

This approach ensures you are reducing the most significant risks first while still making progress on all findings.


# Requesting a Retest

After your development team has fixed a security finding, you can request a retest through the portal. A retest means the Catchify team will verify that the fix actually resolves the vulnerability -- giving you confidence that the issue is truly closed.

## Why Retesting Matters

Fixing a vulnerability is only half the job. Without verification, you cannot be sure that:

* The fix fully addresses the root cause (not just the symptom)
* The fix did not accidentally introduce a new vulnerability
* The finding can be officially marked as resolved

Retesting turns a "we think it is fixed" into a "we know it is fixed."

{% hint style="info" %}
Retests are performed by the same Catchify researchers who identified the original finding, so they know exactly what to look for.
{% endhint %}

## How to Request a Retest

1. Navigate to the finding you have fixed (through **Projects** or **Findings** in the main menu)
2. Open the finding detail page
3. Change the finding status to **Fixed** if you have not already
4. Click the **Request Retest** button

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-97f48acbb8373e466d27e7a43340bda2c2c643fc%2Fretest-requests.png?alt=media" alt="Finding detail page showing the Request Retest button"><figcaption><p>Click Request Retest after your team has applied the fix</p></figcaption></figure>

5. Add a brief note describing what was changed (optional but recommended -- this helps the Catchify team verify efficiently)
6. Click **Submit**

{% hint style="success" %}
Including details about your fix -- such as what was changed and where -- helps the Catchify team complete the retest faster. For example: "Added input validation on the login form to prevent SQL injection" is much more helpful than "Fixed it."
{% endhint %}

## What Happens After You Request a Retest

Once you submit a retest request, here is what to expect:

| Step                   | What Happens                                                                                                                     | Typical Timeframe |
| ---------------------- | -------------------------------------------------------------------------------------------------------------------------------- | ----------------- |
| **Request received**   | The Catchify team is notified and the finding status changes to **Retest Requested**                                             | Immediate         |
| **Retest in progress** | A security researcher verifies the fix using the original reproduction steps                                                     | 1-3 business days |
| **Result: Pass**       | The fix is confirmed. The finding status changes to **Verified**.                                                                | --                |
| **Result: Fail**       | The vulnerability is still present or partially fixed. The finding returns to **Open** with a comment explaining what was found. | --                |

## If the Retest Fails

If the Catchify team finds that the vulnerability is still exploitable after your fix, they will:

* Add a detailed comment to the finding explaining why the retest failed
* Include updated reproduction steps if the behavior has changed
* Set the finding back to **Open**

You can then review the feedback, apply a revised fix, and request another retest.

{% hint style="warning" %}
A failed retest does not mean your effort was wasted. Partial fixes often reduce the severity of the issue, and the detailed feedback helps your team get to the right solution faster.
{% endhint %}

## Retest Tips

* **Fix one issue at a time** -- Request retests for individual findings rather than batching many together. This makes it easier to track what passed and what did not.
* **Test internally first** -- Before requesting a retest, have your own team verify the fix using the reproduction steps in the finding.
* **Include details** -- The more information you provide about your fix, the faster the retest can be completed.
* **Keep access available** -- Make sure the Catchify team still has the necessary access to retest. If credentials or VPN access have changed, update them before requesting the retest.

## Retest Turnaround

Retests are typically completed within **1-3 business days** of the request. If your engagement includes an SLA with specific retest turnaround times, those commitments apply.

If you need an expedited retest for a critical finding, contact your account manager and the Catchify team will prioritize it.


# Pentest Reports

At the conclusion of every penetration testing engagement, the Catchify team delivers a comprehensive report summarizing the testing performed, the vulnerabilities discovered, and the recommended next steps. These reports are designed to be useful for both technical teams and executive stakeholders.

## What is Included in a Report

Each pentest report contains the following sections:

### Executive Summary

A high-level overview written for non-technical stakeholders such as CISOs, board members, and senior management. It covers:

* The scope and objectives of the engagement
* The overall security posture and risk level
* A summary of key findings by severity
* Strategic recommendations

### Methodology

A description of the testing approach used, including:

* The type of testing performed (black box, gray box, white box)
* The standards and frameworks followed (OWASP, PTES, NIST)
* The testing timeline

### Findings Summary

A table listing all findings with their severity, status, and the affected component. This provides a quick reference for tracking remediation progress.

### Detailed Findings

Each finding is documented with:

* Title and severity
* Description and business impact
* Detailed reproduction steps
* Evidence (screenshots and observations)
* Remediation recommendations

### Recommendations

A prioritized list of actions your organization should take, including both immediate fixes and longer-term security improvements.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-6174da2aa5a95be412aa42d6a3e52ca42b93b548%2Freports-list.png?alt=media" alt="Sample pentest report showing executive summary and findings overview"><figcaption><p>A typical pentest report -- professional, detailed, and ready to share with leadership</p></figcaption></figure>

## Accessing Your Reports

To view and download your reports:

1. Navigate to **Projects** in the main menu
2. Click on the completed project
3. Go to the **Reports** tab
4. Click **Download PDF** to save the report to your computer

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-6174da2aa5a95be412aa42d6a3e52ca42b93b548%2Freports-list.png?alt=media" alt="Reports tab showing available report with download button"><figcaption><p>Download your report as a PDF from the project detail page</p></figcaption></figure>

{% hint style="info" %}
Reports become available after the testing engagement is complete and the Catchify team has finalized their review. You will receive a notification when your report is ready.
{% endhint %}

## Understanding Your Report

Here are some tips for getting the most out of your pentest report:

**For executive audiences:**

* Start with the Executive Summary for a big-picture understanding
* Focus on the severity distribution and risk rating
* Use the strategic recommendations section for planning

**For technical teams:**

* Go directly to the Detailed Findings section
* Use the reproduction steps to understand each issue
* Follow the remediation recommendations to fix vulnerabilities
* Reference the findings when requesting retests

**For compliance teams:**

* The report can serve as evidence of security testing for audits and certifications
* The methodology section documents the testing standards applied
* The findings and remediation sections demonstrate your organization's approach to risk management

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7412541663a49bd9dc22317438fedf1afdb932ec%2Ffinding-detail.png?alt=media" alt="Detailed finding within a pentest report showing description, evidence, and recommendation"><figcaption><p>Each finding in the report includes everything your team needs to take action</p></figcaption></figure>

## Sharing Reports

Pentest reports often need to be shared with different stakeholders. Here are some recommendations:

* **Board and executive team** -- Share the Executive Summary section
* **Development team** -- Share the Detailed Findings and Recommendations sections
* **Compliance and audit** -- Share the full report as evidence of testing
* **Third-party clients** -- Share with caution. Discuss with your account manager about what level of detail is appropriate to share externally.

{% hint style="warning" %}
Pentest reports contain sensitive information about your organization's security vulnerabilities. Handle them with care and limit distribution to authorized personnel only.
{% endhint %}

## Requesting Additional Reports

If you need a customized version of your report (for example, an executive-only summary or a report filtered to specific findings), contact your account manager. The Catchify team can prepare tailored versions to meet your specific needs.


# What is Bug Bounty?

A bug bounty program is an ongoing invitation for vetted security researchers to find and report vulnerabilities in your applications. Instead of a one-time test, bug bounty provides continuous security coverage -- researchers look for issues around the clock, and you only pay for valid, verified findings.

## How It Works

The concept is simple: you define what you want tested (the scope), set reward amounts for different severity levels, and Catchify's community of security researchers gets to work finding vulnerabilities. When a researcher finds something, they submit a report, the Catchify team reviews it, and if it is valid, the researcher is rewarded.

Here is the process from your perspective:

1. **You define the scope** -- Together with the Catchify team, you decide which applications, domains, and systems are open for testing
2. **Researchers test your applications** -- Vetted security researchers look for vulnerabilities in the areas you have defined
3. **Reports are triaged** -- The Catchify triage team reviews every submission before it reaches you, filtering out duplicates, false positives, and out-of-scope reports
4. **You review confirmed findings** -- Only validated reports are presented to you for review
5. **Researchers are rewarded** -- When you approve a finding, the researcher receives their reward through Catchify

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-fbc50cb012776f20c1ad83d359be128f696a4b0d%2Fbugbounty-programs.png?alt=media" alt="Bug bounty programs list showing available programs"><figcaption><p>The bug bounty workflow -- from researcher submission to verified finding</p></figcaption></figure>

## Why Bug Bounty?

Bug bounty programs complement penetration testing by providing ongoing security coverage. Here is why organizations choose bug bounty:

| Benefit                  | Description                                                                       |
| ------------------------ | --------------------------------------------------------------------------------- |
| **Continuous coverage**  | Unlike a one-time pentest, researchers are always looking for new vulnerabilities |
| **Diverse perspectives** | Multiple researchers with different skills and approaches test your systems       |
| **Pay for results**      | You only pay when a valid vulnerability is found -- no finding, no cost           |
| **Faster discovery**     | With many researchers working simultaneously, issues are found sooner             |
| **Managed for you**      | The Catchify team handles triage, researcher management, and payouts              |

{% hint style="info" %}
Many organizations run bug bounty programs alongside regular penetration testing. The two approaches complement each other -- pentesting provides structured, comprehensive coverage, while bug bounty catches issues through diverse, creative testing approaches.
{% endhint %}

## How Catchify Manages It for You

Running a bug bounty program can be complex, but Catchify handles the operational work so you do not have to:

* **Researcher vetting** -- Every researcher on the Catchify platform goes through an identity verification and screening process before they can participate in programs
* **Triage** -- Our experienced security team reviews every submission, verifying that reports are valid, unique, and within scope
* **Communication** -- The Catchify team manages day-to-day communication with researchers on your behalf
* **Payments** -- Researcher rewards are handled through the Catchify wallet system -- you fund your wallet, and the Catchify team distributes payments

## Is Bug Bounty Right for You?

Bug bounty is a great fit if:

* Your applications are customer-facing and constantly evolving
* You want continuous security testing beyond periodic penetration tests
* Your team wants to focus on fixing issues rather than managing a testing program
* You are looking for a cost-effective way to scale your security testing

If you are interested in starting a bug bounty program, talk to your account manager. The Catchify team will help you define the scope, set appropriate reward levels, and launch the program.

{% hint style="success" %}
Catchify's bug bounty programs are private by default -- only vetted, invited researchers can see and participate in your program. Your scope and vulnerabilities are never publicly visible.
{% endhint %}


# VDP vs Bug Bounty

If you are exploring ways to improve your organization's security posture, you have likely come across two terms: **VDP** (Vulnerability Disclosure Policy) and **Bug Bounty Program**. Both help you receive vulnerability reports from security researchers, but they work quite differently. This page breaks down what each one is, when to use it, and how they can work together.

## What is a VDP?

A **Vulnerability Disclosure Policy** is a public statement on your website that tells security researchers:

* That your organization welcomes responsible security research
* How they should report vulnerabilities they discover
* What they can expect after submitting a report (response times, process)
* That they will not face legal action for following the policy

Think of a VDP as an open door -- it gives researchers a safe, structured way to let you know about security issues they find. There are no monetary rewards involved; researchers report vulnerabilities out of goodwill, professional responsibility, or for public recognition.

Catchify provides a [VDP Widget](/catchify-platform-documentation/integrations/vdp-widget) that you can embed directly on your website. It gives you a professional, branded disclosure page in minutes -- no development work needed beyond adding a small code snippet.

{% hint style="info" %}
Many international standards, including ISO 27001 and SAMA guidelines, recommend or require organizations to have a vulnerability disclosure policy in place. A VDP helps you meet these requirements.
{% endhint %}

## What is a Bug Bounty Program?

A **Bug Bounty Program** is a paid program where security researchers are financially rewarded for finding and reporting vulnerabilities in your applications. You define the scope (which systems can be tested), set reward amounts based on severity, and Catchify's community of vetted researchers gets to work.

The key difference is the financial incentive. Because researchers are paid for valid findings, bug bounty programs attract more skilled and motivated researchers who dedicate real time and effort to testing your systems.

With Catchify, your bug bounty program is fully managed:

* The Catchify team triages every submission before it reaches you
* Duplicate, false positive, and out-of-scope reports are filtered out
* Researcher communication is handled on your behalf
* Rewards are paid from your [Wallet](/catchify-platform-documentation/quotes-and-invoices/wallet-and-payments) balance

## Side-by-Side Comparison

|                           | **VDP**                                         | **Bug Bounty Program**                                   |
| ------------------------- | ----------------------------------------------- | -------------------------------------------------------- |
| **Purpose**               | Provide a responsible disclosure channel        | Incentivize researchers to actively find vulnerabilities |
| **Rewards**               | No monetary rewards                             | Paid rewards based on severity                           |
| **Researcher motivation** | Goodwill, recognition, responsible disclosure   | Financial incentive plus recognition                     |
| **Who participates**      | Any researcher who finds an issue               | Vetted researchers invited to your program               |
| **Testing approach**      | Researchers report issues they happen to find   | Researchers actively and continuously test your systems  |
| **Volume of reports**     | Lower -- researchers report opportunistic finds | Higher -- financial incentive drives dedicated testing   |
| **Managed by Catchify**   | VDP Widget hosted and maintained for you        | Full management: triage, communication, and payouts      |
| **Cost to you**           | No reward costs                                 | Reward costs based on findings (pay for results)         |
| **Best for**              | Organizations starting their security journey   | Organizations wanting continuous, incentivized testing   |
| **Compliance**            | Meets VDP requirements (ISO 27001, SAMA)        | Goes beyond compliance with proactive security testing   |

## Which One Should You Choose?

**Start with a VDP if:**

* You are beginning to formalize your security program
* You want a responsible disclosure channel without a budget commitment
* You need to meet compliance requirements that call for a disclosure policy
* You want to signal to the security community that you take security seriously

**Add a Bug Bounty Program if:**

* Your applications are customer-facing and constantly evolving
* You want dedicated, continuous security testing from skilled researchers
* You are ready to allocate budget for security findings
* You want to go beyond compliance and proactively identify vulnerabilities
* Your team prefers to focus on fixing issues rather than managing testing

## Using Both Together

Many Catchify clients use a VDP and a bug bounty program together, and we recommend this approach for organizations that are ready for it. Here is how they complement each other:

1. **Your VDP** serves as the public-facing policy on your website. It tells any researcher who comes across your systems how to report issues responsibly.
2. **Your Bug Bounty Program** is your private, incentivized testing channel. Vetted researchers are actively invited to test specific applications within a defined scope.

Reports from both channels are managed through your Catchify portal, so you have a single view of all incoming vulnerability reports regardless of how they were submitted.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-vdp.png?alt=media" alt="VDP Widget integration tab in the Catchify portal"><figcaption><p>Both VDP and Bug Bounty reports are managed from your Catchify portal</p></figcaption></figure>

{% hint style="success" %}
Not sure which approach is right for your organization? Talk to your Catchify account manager. We will help you assess your needs and recommend the best path forward -- whether that is starting with a VDP, launching a bug bounty program, or both.
{% endhint %}

## Next Steps

* **Set up a VDP:** See [VDP Widget](/catchify-platform-documentation/integrations/vdp-widget) to embed a disclosure policy on your website
* **Launch a Bug Bounty Program:** See [What is Bug Bounty?](/catchify-platform-documentation/bug-bounty-program/what-is-bug-bounty) to learn more, or contact your account manager to get started
* **Manage rewards:** See [Wallet & Payments](/catchify-platform-documentation/quotes-and-invoices/wallet-and-payments) to understand how bug bounty rewards are funded


# Managing Your Program

Once your bug bounty program is live, you can manage it directly from your Catchify portal. The program management page gives you control over your program's scope, rewards, and rules -- while the Catchify team handles researcher management and day-to-day operations.

## Viewing Your Program

Navigate to **Bug Bounty** in the main menu to see your active programs. Click on a program to view its details and settings.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-4353ada1462ed4cc09c07fd420cac840fd57c9e0%2Fbugbounty-program-detail.png?alt=media" alt="Bug bounty program overview page showing status, scope, and reward table"><figcaption><p>Your bug bounty program overview -- scope, rewards, and current status at a glance</p></figcaption></figure>

## Program Settings

Your program page shows the key configuration that defines how the program operates:

### Scope

The scope defines exactly what researchers are allowed to test. It includes:

* **In-scope targets** -- The specific domains, applications, or systems researchers can test
* **Out-of-scope items** -- Targets or vulnerability types that researchers should not test or report
* **Testing rules** -- Guidelines researchers must follow, such as not accessing customer data or not performing denial-of-service testing

{% hint style="info" %}
The Catchify team helps you define your initial scope during program setup. If you need to update it later -- for example, to add a new application or exclude a system undergoing maintenance -- contact your account manager.
{% endhint %}

### Reward Table

Your reward table defines how much researchers earn for valid findings at each severity level:

| Severity     | Typical Reward Range     |
| ------------ | ------------------------ |
| **Critical** | SAR 5,000 -- SAR 25,000+ |
| **High**     | SAR 2,000 -- SAR 10,000  |
| **Medium**   | SAR 500 -- SAR 3,000     |
| **Low**      | SAR 100 -- SAR 500       |

The actual amounts for your program are set during setup. Competitive rewards attract more skilled researchers, which means better coverage for your applications.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-4353ada1462ed4cc09c07fd420cac840fd57c9e0%2Fbugbounty-program-detail.png?alt=media" alt="Reward table showing amounts for each severity level"><figcaption><p>Your reward table -- researchers see these amounts when they view your program</p></figcaption></figure>

### Program Rules

Program rules set expectations for how researchers should behave. Common rules include:

* Do not access, modify, or delete data belonging to other users
* Do not perform testing that could degrade service performance
* Report vulnerabilities promptly and do not disclose them publicly
* Only test within the defined scope

## Program Statuses

Your program can be in one of these states:

| Status     | Meaning                                                                                                                    |
| ---------- | -------------------------------------------------------------------------------------------------------------------------- |
| **Active** | The program is live and researchers can submit reports                                                                     |
| **Paused** | The program is temporarily halted -- researchers cannot submit new reports, but existing reports are still being processed |
| **Draft**  | The program is being set up and is not yet visible to researchers                                                          |

{% hint style="warning" %}
If you need to pause your program -- for example, during a major deployment or migration -- contact the Catchify team. They will pause the program and notify active researchers.
{% endhint %}

## Program Statistics

Your program page includes key metrics to help you track performance:

* **Total reports received** -- How many reports have been submitted by researchers
* **Valid reports** -- Reports that were confirmed as real vulnerabilities
* **Total rewards paid** -- The cumulative amount paid to researchers
* **Average response time** -- How quickly reports are triaged and responded to

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-4353ada1462ed4cc09c07fd420cac840fd57c9e0%2Fbugbounty-program-detail.png?alt=media" alt="Program statistics showing report counts, rewards paid, and response times"><figcaption><p>Track your program's performance with real-time statistics</p></figcaption></figure>

## Working with the Catchify Team

While you have visibility into your program through the portal, the Catchify team handles many operational tasks behind the scenes:

* **Researcher invitations** -- The Catchify team selects and invites qualified researchers to your program based on their skills and track record
* **Initial triage** -- Every report is reviewed by the Catchify triage team before it reaches you
* **Researcher communication** -- Routine questions from researchers are handled by the Catchify team
* **Scope clarifications** -- If a researcher has questions about what is in scope, the Catchify team provides guidance based on your program rules

{% hint style="success" %}
Think of the Catchify team as an extension of your security organization. You set the direction, and we handle the execution.
{% endhint %}


# Reviewing Reports

When a security researcher discovers a vulnerability in your application through the bug bounty program, they submit a report through Catchify. The Catchify triage team reviews every report first, and only validated submissions reach your queue for review. This page explains how to review and manage those reports.

## How Reports Reach You

Before a report appears in your portal, it goes through Catchify's triage process:

1. **Researcher submits a report** -- A researcher identifies a vulnerability and submits detailed documentation
2. **Catchify triage review** -- Our security team validates the report, confirming it is legitimate, in scope, and not a duplicate
3. **Report appears in your portal** -- Only confirmed, valid reports are forwarded to you for review
4. **You review and respond** -- You review the finding and approve or provide feedback

{% hint style="info" %}
The Catchify triage team filters out duplicates, false positives, and out-of-scope reports so you only spend time on issues that matter.
{% endhint %}

## Viewing Your Reports

Navigate to **Bug Bounty** and then **Reports** to see all submissions for your programs. Each report shows:

* **Title** -- A summary of the vulnerability
* **Severity** -- The assessed severity level
* **Status** -- Where the report is in the review process
* **Researcher** -- The username of the researcher who submitted it (researchers remain anonymous by default)
* **Submitted date** -- When the report was received

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e6dcee19efba31b58414f765d0a8c7bfa19bcf2%2Fbugbounty-reports-list.png?alt=media" alt="Bug bounty reports list showing title, severity, status, and researcher"><figcaption><p>Your bug bounty reports -- review validated submissions from security researchers</p></figcaption></figure>

## Report Statuses

Each report moves through the following stages:

| Status        | What It Means                                                              |
| ------------- | -------------------------------------------------------------------------- |
| **New**       | The report has been submitted and is awaiting initial triage               |
| **Triaged**   | The Catchify team has validated the report and it is ready for your review |
| **Confirmed** | You have confirmed that the vulnerability is valid and will be addressed   |
| **Approved**  | The report has been approved for reward payment                            |
| **Rejected**  | The report was determined to not be a valid finding (with explanation)     |
| **Duplicate** | The same vulnerability was already reported by another researcher          |
| **Resolved**  | The vulnerability has been fixed and verified                              |

The typical flow for a valid report is: **New** --> **Triaged** --> **Confirmed** --> **Approved** --> **Resolved**

## Reviewing a Report

When you open a report, you will see the full details submitted by the researcher:

* **Vulnerability description** -- What the issue is and how it was found
* **Impact assessment** -- What an attacker could do by exploiting this vulnerability
* **Steps to reproduce** -- How to demonstrate the vulnerability
* **Evidence** -- Screenshots, recordings, or other proof
* **Suggested severity** -- The researcher's proposed severity (the Catchify team may adjust this during triage)

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-59cc9e80364ea7d60eedf1a24c69110c93578ca8%2Fbugbounty-report-detail.png?alt=media" alt="Bug bounty report detail showing description, steps to reproduce, and evidence"><figcaption><p>A report includes everything you need to understand the vulnerability</p></figcaption></figure>

## Taking Action on a Report

After reviewing a report, you can:

### Confirm the Finding

If you agree the vulnerability is valid, change the status to **Confirmed**. This signals to the Catchify team that you acknowledge the issue and will work on a fix.

### Add Comments

Add comments to communicate with the Catchify team about the report. For example:

* Ask for clarification about the reproduction steps
* Provide context about why a finding may be less severe in your environment
* Share an estimated timeline for a fix

### Approve for Reward

When you are satisfied that the report is valid and complete, change the status to **Approved**. The Catchify team will process the researcher's reward from your bug bounty wallet.

### Reject

If you believe the report is not valid or not applicable, you can reject it. Provide a clear explanation so the Catchify team can communicate the reasoning to the researcher.

{% hint style="warning" %}
Prompt responses to reports maintain researcher motivation and program reputation. We recommend reviewing new reports within 48 hours of them being triaged.
{% endhint %}

## After Approval

Once a report is approved:

* The researcher receives their reward through the Catchify wallet system
* The finding is added to your project's finding list
* You can track the fix and request a retest, just like any other finding
* The report status changes to **Resolved** once the fix is verified

{% hint style="success" %}
Consistent, timely reviews encourage researchers to continue testing your applications. A well-managed bug bounty program attracts the best talent.
{% endhint %}


# Rewards & Payments

When a security researcher submits a valid vulnerability report through your bug bounty program, they earn a reward. The Catchify platform manages the entire payment process for you -- from setting reward levels to distributing payments to researchers.

## How Rewards Work

Rewards are paid to researchers based on the severity of their verified findings. When you approve a bug bounty report, the corresponding reward amount is deducted from your bug bounty wallet and paid to the researcher through Catchify.

You set the reward amounts for each severity level when your program is created, and you can adjust them over time with help from the Catchify team.

### Typical Reward Ranges

| Severity     | Typical Range (SAR) | Description                                      |
| ------------ | ------------------- | ------------------------------------------------ |
| **Critical** | 5,000 -- 25,000+    | Vulnerabilities with the highest business impact |
| **High**     | 2,000 -- 10,000     | Significant security risks                       |
| **Medium**   | 500 -- 3,000        | Moderate issues that should be addressed         |
| **Low**      | 100 -- 500          | Minor issues with limited impact                 |

{% hint style="info" %}
The actual reward amounts for your program depend on the type and sensitivity of your applications. The Catchify team will recommend appropriate levels based on industry benchmarks and your budget.
{% endhint %}

## The Payment Process

Here is what happens from the time a report is approved to when the researcher gets paid:

1. **You approve the report** -- You confirm the vulnerability is valid and approve the reward
2. **Amount deducted from wallet** -- The reward amount is automatically deducted from your bug bounty wallet
3. **Catchify processes payment** -- The Catchify team handles the transfer to the researcher
4. **Researcher receives payment** -- The researcher is paid through the platform

You do not need to handle any payment logistics -- no invoicing individual researchers, no bank transfers, and no payment tracking. Catchify manages everything.

## Your Bug Bounty Wallet

Your bug bounty wallet is a prepaid balance that funds researcher rewards. You add credits to your wallet, and rewards are deducted automatically when reports are approved.

### Adding Credits

To add credits to your wallet:

1. Navigate to **Wallet** in the main menu
2. Click **Add Credits**
3. Enter the amount you would like to add
4. The Catchify team will generate an invoice for the credit amount
5. Once payment is received, credits are added to your wallet

### Viewing Your Balance

Your current wallet balance is displayed on the Wallet page. You can also see:

* **Available balance** -- How much is available for future rewards
* **Pending rewards** -- Amounts reserved for reports that are confirmed but not yet paid
* **Total spent** -- Cumulative rewards paid since the program started

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7321e075350ad74c1442416058e029defa5c4de4%2Fwallet-overview.png?alt=media" alt="Bug bounty wallet showing balance, pending rewards, and transaction history"><figcaption><p>Your wallet balance and recent transactions</p></figcaption></figure>

{% hint style="warning" %}
Keep your wallet funded to ensure researchers can be paid promptly. If your wallet balance is too low to cover a reward, the payment will be held until credits are added. This can slow down report resolution and reduce researcher engagement.
{% endhint %}

## Transaction History

The wallet page includes a complete transaction history showing:

* Date of each transaction
* Transaction type (credit added, reward paid)
* Amount
* Related report (for reward payments)
* Running balance

This gives you full visibility into how your bug bounty budget is being spent.

## Setting Competitive Rewards

The Catchify team can help you set reward levels that are competitive and aligned with your budget. Key considerations include:

* **Application sensitivity** -- Applications handling financial or personal data typically warrant higher rewards
* **Market benchmarks** -- Rewards should be competitive with similar programs in your industry
* **Budget allocation** -- Work with your account manager to plan monthly or quarterly budgets
* **Researcher quality** -- Higher rewards attract more experienced researchers

{% hint style="success" %}
Investing in competitive rewards pays off. Organizations with well-funded programs consistently receive higher-quality reports and faster vulnerability discovery.
{% endhint %}

## Need to Adjust Your Rewards?

If you want to change your reward amounts -- for example, to increase rewards during a product launch or focus researchers on a specific application -- contact your account manager. The Catchify team will update your program settings and communicate changes to active researchers.


# Requesting a Quote

When you need a new penetration test or want to explore additional services, you can request a quote directly through your Catchify portal. The Catchify team will review your request and prepare a tailored proposal based on your requirements.

## How to Request a Quote

1. Navigate to **Quotes** in the main menu
2. Click **Request New Quote**
3. Fill in the details about what you need:
   * **Service type** -- Select the type of testing (web application, mobile application, network, cloud infrastructure, etc.)
   * **Target details** -- Describe the application or system to be tested, including URLs, environments, and any relevant context
   * **Preferred timeline** -- When you would like testing to begin and any deadlines to consider
   * **Additional notes** -- Any specific requirements, compliance standards, or areas of concern
4. Click **Submit Request**

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-0152a11213b3d50fd939f83e2ff6e0c78f0fdfbf%2Fquotes-list.png?alt=media" alt="Quotes page showing quote requests and their statuses"><figcaption><p>Fill in your requirements and the Catchify team will prepare a proposal</p></figcaption></figure>

## What Happens Next

After you submit your request:

| Step                   | What Happens                                                                    | Typical Timeframe |
| ---------------------- | ------------------------------------------------------------------------------- | ----------------- |
| **Request received**   | The Catchify team reviews your requirements                                     | Same day          |
| **Scoping discussion** | Your account manager may reach out to clarify details or discuss the engagement | 1-2 business days |
| **Quote prepared**     | A formal quote is created with scope, pricing, and timeline                     | 2-3 business days |
| **Quote delivered**    | The quote appears in your portal and you receive an email notification          | --                |

{% hint style="info" %}
For straightforward engagements, quotes can often be prepared within one business day. More complex scoping (such as large infrastructure assessments) may take a bit longer.
{% endhint %}

## Reviewing a Quote

When your quote is ready, you will find it in the **Quotes** section of your portal. Each quote includes:

* **Service description** -- A detailed breakdown of what will be tested and how
* **Scope** -- The specific targets, methodologies, and boundaries of the engagement
* **Timeline** -- Proposed start and end dates
* **Pricing** -- The total cost of the engagement, broken down by service
* **Terms** -- Payment terms and conditions

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-0152a11213b3d50fd939f83e2ff6e0c78f0fdfbf%2Fquotes-list.png?alt=media" alt="Quote detail page showing scope, timeline, and pricing"><figcaption><p>Review your quote -- scope, timeline, and pricing all in one place</p></figcaption></figure>

## Approving or Declining a Quote

Once you have reviewed the quote:

* **To approve** -- Click **Approve Quote**. This confirms the engagement and the Catchify team will begin scheduling the testing.
* **To discuss changes** -- Add a comment or contact your account manager if you would like to adjust the scope, timeline, or pricing before approving.
* **To decline** -- Click **Decline Quote** if you do not wish to proceed. You can always request a new quote later.

{% hint style="success" %}
Once a quote is approved, the Catchify team will send you a formal agreement and begin preparing for the engagement. You will receive an invoice based on the agreed payment terms.
{% endhint %}

## Quote Statuses

| Status       | Meaning                                                           |
| ------------ | ----------------------------------------------------------------- |
| **Draft**    | The quote is being prepared by the Catchify team                  |
| **Sent**     | The quote is ready for your review                                |
| **Approved** | You have approved the quote and the engagement is being scheduled |
| **Declined** | The quote was not accepted                                        |
| **Expired**  | The quote was not acted upon within the validity period           |

## Viewing Past Quotes

All your quotes -- past and present -- are accessible from the Quotes page. This gives you a full history of your engagements and makes it easy to request similar services again.

{% hint style="info" %}
If you need a similar engagement to one you have done before, mention the previous quote in your new request. The Catchify team can use it as a starting point, which speeds up the scoping process.
{% endhint %}

## Questions About Pricing?

Catchify pricing is based on the complexity and scope of each engagement. Factors that influence pricing include:

* The number and type of applications or systems to be tested
* The depth of testing required (basic assessment vs. comprehensive testing)
* The timeline and urgency of the engagement
* Any special requirements such as compliance-specific testing

Contact your account manager at any time to discuss pricing or explore options that fit your budget.


# Your Invoices

The Invoices page in your Catchify portal gives you a complete view of all invoices associated with your account. Whether for penetration testing engagements, bug bounty wallet top-ups, or other services, you can view, download, and track the status of every invoice in one place.

## Viewing Your Invoices

Navigate to **Invoices** in the main menu to see a list of all your invoices. Each entry shows:

* **Invoice number** -- A unique reference number for the invoice
* **Date** -- When the invoice was issued
* **Amount** -- The total amount
* **Status** -- The current payment status
* **Description** -- What the invoice is for

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-b5aeab87c73df39da5ed48e7ac4b3e086486f499%2Finvoices-list.png?alt=media" alt="Invoices list page showing invoice numbers, dates, amounts, and statuses"><figcaption><p>All your invoices in one place -- view status and download at any time</p></figcaption></figure>

## Invoice Statuses

| Status             | What It Means                                                                |
| ------------------ | ---------------------------------------------------------------------------- |
| **Draft**          | The invoice is being prepared and has not been finalized yet                 |
| **Sent**           | The invoice has been issued and is awaiting payment                          |
| **Paid**           | Payment has been received and recorded                                       |
| **Overdue**        | The payment due date has passed. Please arrange payment as soon as possible. |
| **Partially Paid** | A portion of the invoice has been paid, with a remaining balance outstanding |

{% hint style="warning" %}
If an invoice is marked as overdue, please contact your account manager or email <support@catchify.sa> to arrange payment. Overdue invoices may affect your ability to request new engagements.
{% endhint %}

## Viewing Invoice Details

Click on any invoice to see its full details, including:

* **Line items** -- A breakdown of the services or credits included
* **Tax information** -- VAT amounts where applicable
* **Payment terms** -- Due date and accepted payment methods
* **Notes** -- Any additional information from the Catchify team

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-b5aeab87c73df39da5ed48e7ac4b3e086486f499%2Finvoices-list.png?alt=media" alt="Invoice detail page showing line items, tax, and payment terms"><figcaption><p>Click any invoice to see the full breakdown</p></figcaption></figure>

## Downloading Invoices

You can download any invoice as a PDF for your records, accounting, or compliance purposes:

1. Open the invoice you want to download
2. Click **Download PDF**
3. The invoice will be saved to your computer

## ZATCA Compliance

All Catchify invoices are generated in compliance with ZATCA (Zakat, Tax and Customs Authority) regulations in Saudi Arabia. This includes:

* Proper VAT registration and calculation
* Required fields and formatting per ZATCA standards
* QR code for electronic invoice verification where applicable

{% hint style="info" %}
If your organization requires invoices in a specific format for your accounting system, contact your account manager. We can accommodate most formatting requirements.
{% endhint %}

## Invoice History

Your complete invoice history is available in the portal at all times. You can:

* **Filter by status** -- View only paid, pending, or overdue invoices
* **Filter by date** -- Narrow down to a specific time period
* **Search** -- Find a specific invoice by number or description

This makes it easy to pull up records during audits, budget reviews, or end-of-year accounting.

## Payment Methods

The Catchify team will provide payment instructions on each invoice. Common payment methods include:

* Bank transfer
* Wire transfer

If you have questions about payment options or need to set up a different payment arrangement, your account manager can help.

{% hint style="success" %}
Keeping your invoices up to date ensures uninterrupted access to Catchify services and timely processing of new engagements.
{% endhint %}


# Wallet & Payments

Your Catchify wallet is a prepaid balance used to fund bug bounty rewards and other security services. The wallet is managed by the Catchify team -- you do not need to add credits yourself. Instead, Catchify invoices you, and once your payment is received, the team adds credits to your account on your behalf.

By keeping your wallet funded, you ensure that researchers are paid promptly when their reports are approved -- which keeps your program attractive and your applications continuously tested.

## How the Wallet Works

The wallet follows a simple, Catchify-managed flow:

1. **Catchify sends you an invoice** -- The Catchify team invoices you for the credit amount based on your program's needs
2. **You pay the invoice** -- You process the payment through your normal accounts payable process
3. **Catchify adds credits to your wallet** -- Once your payment is confirmed, the Catchify team adds the credits to your account
4. **Rewards are deducted automatically** -- When a bug bounty report is approved and rewarded, the amount is deducted from your wallet balance
5. **Catchify tops you up as needed** -- When your balance gets low, the Catchify team will send you a new invoice to keep your program funded

You do not manage credits directly. The Catchify team handles the entire process from invoicing through to crediting your account.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7321e075350ad74c1442416058e029defa5c4de4%2Fwallet-overview.png?alt=media" alt="Wallet page showing current balance, pending rewards, and recent transactions"><figcaption><p>Your wallet balance and recent activity</p></figcaption></figure>

## Viewing Your Wallet

Navigate to **Wallet** in the main menu to see:

| Section                 | What It Shows                                                     |
| ----------------------- | ----------------------------------------------------------------- |
| **Available Balance**   | The amount currently available for rewards                        |
| **Pending Rewards**     | Amounts reserved for approved reports awaiting payment processing |
| **Total Credits Added** | Cumulative amount deposited into your wallet                      |
| **Total Rewards Paid**  | Cumulative amount paid out to researchers                         |

## Understanding Credits

Credits represent your prepaid balance for security services on the Catchify platform. Here is how the credit system works:

| Step                      | What Happens                                                                            |
| ------------------------- | --------------------------------------------------------------------------------------- |
| **Catchify invoices you** | The Catchify team determines how much credit you need and sends an invoice              |
| **You pay the invoice**   | You process the payment as you would any vendor invoice                                 |
| **Credits are added**     | The Catchify team adds the corresponding credits to your account                        |
| **Credits are consumed**  | Credits are used when bug bounty rewards are paid out or pentest services are delivered |

You can view your credit balance and full transaction history at any time in the portal. Every credit addition and deduction is recorded with a clear reference to the associated invoice or report.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7321e075350ad74c1442416058e029defa5c4de4%2Fwallet-overview.png?alt=media" alt="Credits section showing balance and recent credit transactions"><figcaption><p>Your credit balance and transaction details are always visible in the portal</p></figcaption></figure>

{% hint style="info" %}
You do not add credits yourself. The process is always: Catchify invoices you, you pay, and the Catchify team adds credits to your account. This ensures accurate record-keeping and proper invoicing.
{% endhint %}

## Transaction History

The wallet page includes a complete history of every transaction, so you always know exactly where your budget is going:

* **Credits added** -- Deposits added by the Catchify team after you pay an invoice, with dates and invoice references
* **Rewards paid** -- Payments to researchers, linked to the specific bug bounty report
* **Running balance** -- Your balance after each transaction

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-7321e075350ad74c1442416058e029defa5c4de4%2Fwallet-overview.png?alt=media" alt="Transaction history table showing credits, rewards, and running balance"><figcaption><p>Full transparency into every wallet transaction</p></figcaption></figure>

You can filter the transaction history by:

* **Date range** -- View transactions for a specific period
* **Transaction type** -- Show only credits or only rewards

## What Consumes Credits?

Credits are deducted from your wallet when:

* **Bug bounty rewards are paid** -- When a report is approved and a reward is assigned, the amount is automatically deducted from your balance
* **Pentest services are delivered** -- Penetration testing engagements may also consume credits, depending on your agreement with Catchify

Each deduction is linked to the specific report or service it relates to, so you always have a clear audit trail.

## Budget Planning

To keep your bug bounty program running smoothly, we recommend:

* **Maintain a minimum balance** -- Keep enough in your wallet to cover at least a few weeks of expected rewards. Your account manager can help estimate this based on your program's activity level.
* **Respond to top-up invoices promptly** -- When the Catchify team sends a top-up invoice, processing it quickly ensures there are no gaps in your program's ability to pay researchers.
* **Review spending monthly** -- Check your transaction history to understand your average monthly reward spend and plan accordingly.

{% hint style="warning" %}
If your wallet balance reaches zero, approved reports cannot be paid until credits are added. The Catchify team monitors your balance and will proactively send you an invoice when it gets low, but prompt payment helps avoid any delays in rewarding researchers.
{% endhint %}

## Wallet vs. Invoices

It is helpful to understand the relationship between your wallet and your invoices:

* **Invoices fund your wallet** -- When the Catchify team sends you a credit invoice and you pay it, credits are added to your wallet
* **Bug bounty rewards** are paid from your wallet balance automatically
* **Your transaction history** shows every credit addition (with invoice reference) and every reward deduction (with report reference)

In short: Catchify invoices you, you pay, credits appear in your wallet, and rewards are deducted as reports are approved. The entire flow is managed for you.

{% hint style="success" %}
A well-funded wallet signals to researchers that your program is active and reliable, attracting higher-quality submissions and more consistent coverage.
{% endhint %}

## Questions About Your Wallet?

If you have questions about your wallet balance, need help planning your budget, or want to understand your spending patterns, contact your account manager or email <support@catchify.sa>.


# Inviting Team Members

Catchify is designed for teams. You can invite colleagues from across your organization -- security managers, developers, IT directors, project managers -- so everyone who needs visibility into your security testing program has access.

## How to Invite a Team Member

1. Navigate to **Team** in the main menu
2. Click **Invite Member**
3. Enter the team member's details:
   * **Email address** -- The email they will use to log in
   * **Full name** -- Their first and last name
   * **Role** -- Select the appropriate role (see [Roles & Permissions](/catchify-platform-documentation/team-management/roles-and-permissions) for details)
4. Click **Send Invitation**

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5c3da7ff5f66771ab0af667598d4e82a7f97f2da%2Fteam-management.png?alt=media" alt="Team member invitation form with email, name, and role fields"><figcaption><p>Invite a colleague by entering their email and selecting their role</p></figcaption></figure>

The team member will receive an invitation email with a link to set up their account. They will need to:

* Click the link in the email
* Create a password
* Verify their email address
* Log in to the portal

{% hint style="info" %}
Invitation links expire after 7 days. If a team member does not activate their account in time, you can resend the invitation from the Team page.
{% endhint %}

## Managing Your Team

The Team page shows all members of your organization on Catchify:

| Column     | Description                                                         |
| ---------- | ------------------------------------------------------------------- |
| **Name**   | The team member's full name                                         |
| **Email**  | Their email address                                                 |
| **Role**   | Their assigned role (Manager or Member)                             |
| **Status** | Active, Pending (invitation sent but not yet accepted), or Disabled |
| **Joined** | When they activated their account                                   |

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5c3da7ff5f66771ab0af667598d4e82a7f97f2da%2Fteam-management.png?alt=media" alt="Team members list showing names, roles, and statuses"><figcaption><p>View and manage all your team members from one page</p></figcaption></figure>

## Editing a Team Member

To change a team member's role or permissions:

1. Find the member on the Team page
2. Click the **Edit** button next to their name
3. Update their role or specific permissions
4. Click **Save Changes**

Changes take effect immediately -- the team member will see their updated access the next time they load a page or log in.

## Removing a Team Member

If a team member leaves your organization or no longer needs access:

1. Find the member on the Team page
2. Click **Remove** next to their name
3. Confirm the removal

The member will immediately lose access to the portal. Their past activity (comments, status changes, etc.) will remain visible in the system for audit purposes.

{% hint style="warning" %}
Removing a team member is permanent. If they need access again in the future, you will need to send a new invitation.
{% endhint %}

## Resending Invitations

If a team member did not receive their invitation or the link expired:

1. Find the member on the Team page (they will show a **Pending** status)
2. Click **Resend Invitation**
3. A fresh invitation email will be sent to their address

## Best Practices for Team Setup

* **Invite all stakeholders early** -- Make sure everyone who needs visibility has access before testing begins
* **Assign appropriate roles** -- Give each member only the access they need. See [Roles & Permissions](/catchify-platform-documentation/team-management/roles-and-permissions) for guidance.
* **Review your team regularly** -- Periodically check your team list and remove members who no longer need access
* **Enable 2FA for everyone** -- Encourage all team members to set up two-factor authentication for an extra layer of security

{% hint style="success" %}
There is no limit to the number of team members you can add to your Catchify account. Invite everyone who needs to be part of the security conversation.
{% endhint %}


# Roles & Permissions

Catchify uses a role-based access system to ensure each team member sees and does only what they need to. This keeps your security data organized and prevents accidental changes by team members who do not need full access.

## Available Roles

There are two main roles in Catchify:

### Manager

Managers have full access to everything in the portal. This role is designed for security leaders, CISOs, and team leads who need complete visibility and control.

**Managers can:**

* View all projects, findings, and reports
* Manage bug bounty programs
* Approve quotes and view invoices
* Invite and manage team members
* Configure integrations
* Request retests
* Access the wallet and manage payments

### Member

Members have customizable access based on the specific permissions you assign. This role is ideal for developers, project managers, compliance staff, and other team members who need access to specific parts of the portal.

## Permission Details

When assigning the Member role, you can enable or disable the following permissions:

| Permission              | What It Allows                                             |
| ----------------------- | ---------------------------------------------------------- |
| **View Findings**       | See security findings across projects                      |
| **Add Comments**        | Add comments to findings and reports                       |
| **View Invoices**       | Access invoice history and download PDFs                   |
| **Manage Team**         | Invite, edit, and remove team members                      |
| **Manage Integrations** | Set up and configure Slack, Jira, and webhook integrations |
| **Request Retest**      | Submit retest requests after fixes are applied             |
| **View Assets**         | See the list of assets and scope information for projects  |
| **Upload Files**        | Attach files and documents to findings and projects        |
| **View Quotes**         | Access quotes and their details                            |

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5c3da7ff5f66771ab0af667598d4e82a7f97f2da%2Fteam-management.png?alt=media" alt="Permission settings showing checkboxes for each available permission"><figcaption><p>Select exactly which permissions each team member needs</p></figcaption></figure>

{% hint style="info" %}
Only Managers can change roles and permissions for other team members. If you need your permissions updated, ask a Manager on your team.
{% endhint %}

## Recommended Setups

Here are some common permission configurations for different roles in your organization:

### CISO / Security Director

**Role:** Manager

Full access to the portal. CISOs and security directors typically need to see everything, approve quotes, manage the team, and oversee the entire security testing program.

### Security Engineer / Analyst

**Role:** Member

| Permission          | Enabled |
| ------------------- | ------- |
| View Findings       | Yes     |
| Add Comments        | Yes     |
| Request Retest      | Yes     |
| View Assets         | Yes     |
| Upload Files        | Yes     |
| View Invoices       | No      |
| Manage Team         | No      |
| Manage Integrations | No      |
| View Quotes         | No      |

Security engineers need to work directly with findings -- reviewing them, adding context, and requesting retests after fixes.

### Developer / Engineering Lead

**Role:** Member

| Permission          | Enabled |
| ------------------- | ------- |
| View Findings       | Yes     |
| Add Comments        | Yes     |
| Request Retest      | Yes     |
| View Assets         | Yes     |
| Upload Files        | Yes     |
| View Invoices       | No      |
| Manage Team         | No      |
| Manage Integrations | No      |
| View Quotes         | No      |

Developers need to see findings and their reproduction steps so they can implement fixes. They should also be able to request retests.

### Project Manager

**Role:** Member

| Permission          | Enabled |
| ------------------- | ------- |
| View Findings       | Yes     |
| Add Comments        | Yes     |
| View Invoices       | Yes     |
| View Assets         | Yes     |
| View Quotes         | Yes     |
| Request Retest      | No      |
| Manage Team         | No      |
| Manage Integrations | No      |
| Upload Files        | No      |

Project managers need visibility into findings for planning and tracking, along with access to quotes and invoices for budget management.

### Compliance / Audit

**Role:** Member

| Permission          | Enabled |
| ------------------- | ------- |
| View Findings       | Yes     |
| View Invoices       | Yes     |
| View Assets         | Yes     |
| View Quotes         | Yes     |
| Add Comments        | No      |
| Request Retest      | No      |
| Manage Team         | No      |
| Manage Integrations | No      |
| Upload Files        | No      |

Compliance team members typically need read-only access to findings, invoices, and reports for audit and regulatory purposes.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5c3da7ff5f66771ab0af667598d4e82a7f97f2da%2Fteam-management.png?alt=media" alt="Role assignment page showing Manager and Member options with permission toggles"><figcaption><p>Assign roles and fine-tune permissions for each team member</p></figcaption></figure>

## Changing Roles and Permissions

To update a team member's role or permissions:

1. Go to the **Team** page
2. Click **Edit** next to the team member
3. Change their role or adjust individual permissions
4. Click **Save Changes**

Changes take effect immediately.

{% hint style="warning" %}
Be careful when granting the Manage Team permission. Team members with this permission can invite new members and change permissions for others.
{% endhint %}

## Best Practices

* **Follow the principle of least privilege** -- Give each team member only the permissions they need for their job
* **Review permissions quarterly** -- As roles change within your organization, update portal permissions accordingly
* **Have at least two Managers** -- Ensure you have a backup Manager in case one is unavailable
* **Document your setup** -- Keep an internal record of who has what access and why

{% hint style="success" %}
A well-organized team setup with appropriate permissions ensures security data is accessible to those who need it while staying protected from unauthorized access.
{% endhint %}


# Slack Notifications

Connect Catchify to your Slack workspace so your team receives real-time notifications about new findings, status changes, and other important events -- right where you already communicate. No more checking the portal to see if something new has come in.

## Setting Up Slack Integration

Connecting Slack takes just a few steps:

### Step 1: Open Integration Settings

1. Navigate to **Integrations** in the main menu
2. Find the **Slack** card and click **Connect**

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5e0ecc34b0ef31e98a68400089da6954acf39c74%2Fintegrations-slack.png?alt=media" alt="Integrations page showing the Slack integration tab"><figcaption><p>Find Slack on the Integrations page and click Connect</p></figcaption></figure>

### Step 2: Authorize Catchify

1. You will be redirected to Slack's authorization page
2. Select the Slack workspace you want to connect
3. Review the permissions Catchify is requesting
4. Click **Allow** to authorize the connection

{% hint style="info" %}
You will need to be a Slack workspace administrator or have permission to install apps in your Slack workspace.
{% endhint %}

### Step 3: Choose Your Channel and Events

After authorization, you will be taken back to Catchify to configure your preferences:

1. **Select a channel** -- Choose which Slack channel should receive Catchify notifications (for example, #security-alerts or #catchify-findings)
2. **Choose events** -- Select which types of events you want to be notified about

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-5e0ecc34b0ef31e98a68400089da6954acf39c74%2Fintegrations-slack.png?alt=media" alt="Slack configuration page showing channel selection and event toggles"><figcaption><p>Choose your channel and select which events to receive</p></figcaption></figure>

## Available Notification Events

You can choose to receive Slack notifications for any combination of the following events:

| Event                      | What You Will See                                                   |
| -------------------------- | ------------------------------------------------------------------- |
| **New Finding**            | A message when a new vulnerability is discovered                    |
| **Finding Status Changed** | Updates when a finding moves to a new status                        |
| **New Bug Bounty Report**  | A message when a researcher submits a new report                    |
| **Report Status Changed**  | Updates when a bug bounty report is triaged, confirmed, or resolved |
| **Retest Completed**       | Notification when a retest is finished with the pass/fail result    |
| **New Comment**            | A message when someone adds a comment to a finding                  |
| **Project Started**        | Notification when a new pentest engagement begins                   |
| **Project Completed**      | Notification when a pentest engagement is finished                  |
| **Invoice Created**        | A message when a new invoice is generated                           |

## What Notifications Look Like

Catchify notifications in Slack are formatted as rich messages that include:

* The event type (for example, "New Critical Finding")
* The name of the affected project or program
* Key details such as finding title and severity
* A direct link to view the full details in the Catchify portal

## Managing Your Slack Integration

After setup, you can manage your Slack integration at any time:

* **Change the channel** -- Update which channel receives notifications
* **Update events** -- Add or remove event types
* **Test the connection** -- Send a test notification to verify everything is working
* **Disconnect** -- Remove the Slack integration entirely

To make changes, go to **Integrations** in the main menu and click **Configure** on the Slack card.

{% hint style="warning" %}
If you change the Slack channel and the bot has not been added to the new channel, notifications will fail silently. Make sure to invite the Catchify bot to any new channel you select.
{% endhint %}

## Tips for Getting the Most from Slack Notifications

* **Use a dedicated channel** -- Create a channel specifically for Catchify notifications (like #catchify-alerts) to keep security updates organized
* **Pin important notifications** -- When a critical finding comes in, pin it in the channel so your team does not miss it
* **Set channel notification preferences** -- Configure Slack to send push notifications for critical and high findings while keeping lower-severity updates as regular messages
* **Involve the right people** -- Add all relevant team members to your Catchify Slack channel so everyone stays informed

{% hint style="success" %}
Teams that connect Slack to Catchify respond to critical findings significantly faster. Real-time notifications mean your team can start working on fixes within minutes of discovery.
{% endhint %}


# Jira Integration

Connect Catchify to your Jira workspace so security findings are automatically turned into Jira tickets. This keeps your development team in their familiar workflow while ensuring security issues are tracked and resolved alongside regular development tasks.

## What the Jira Integration Does

When a new finding is discovered in Catchify, the integration can automatically create a corresponding Jira issue in your project. The Jira ticket includes:

* The finding title as the issue summary
* The severity level mapped to your Jira priority scheme
* The full description, impact, and remediation guidance
* A link back to the finding in Catchify for additional details

When a Jira ticket is updated (for example, moved to "Done"), the status can sync back to Catchify -- keeping both systems in alignment.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-jira.png?alt=media" alt="Jira integration tab in the Catchify portal"><figcaption><p>Findings in Catchify automatically become Jira tickets for your development team</p></figcaption></figure>

## Setting Up the Integration

### Step 1: Open Integration Settings

1. Navigate to **Integrations** in the main menu
2. Find the **Jira** card and click **Connect**

### Step 2: Connect Your Jira Instance

1. Enter your Jira workspace URL (for example, yourcompany.atlassian.net)
2. Authorize Catchify to access your Jira workspace
3. Select the Jira project where findings should be created

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-jira.png?alt=media" alt="Jira connection form showing workspace URL and project selection"><figcaption><p>Connect your Jira workspace and choose your project</p></figcaption></figure>

### Step 3: Configure Field Mapping

Map Catchify fields to your Jira fields:

| Catchify Field | Jira Field           | Notes                                                 |
| -------------- | -------------------- | ----------------------------------------------------- |
| Finding title  | Summary              | The issue title                                       |
| Severity       | Priority             | Map Critical/High/Medium/Low to your Jira priorities  |
| Description    | Description          | Full finding details including impact and remediation |
| Status         | Status               | Map Catchify statuses to your Jira workflow           |
| Project        | Labels or Components | Optional: tag tickets by Catchify project             |

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-jira.png?alt=media" alt="Field mapping configuration showing Catchify fields mapped to Jira fields"><figcaption><p>Map Catchify fields to your Jira workflow</p></figcaption></figure>

### Step 4: Choose Sync Options

Configure how the integration behaves:

* **Auto-create tickets** -- Automatically create a Jira ticket for every new finding, or only for specific severity levels
* **Status sync** -- Enable two-way status sync so changes in Jira are reflected in Catchify and vice versa
* **Severity filter** -- Only create tickets for findings above a certain severity threshold (for example, only Medium and above)

{% hint style="info" %}
We recommend starting with auto-create enabled for High and Critical findings only, and then expanding to Medium and Low once your team is comfortable with the workflow.
{% endhint %}

## How Status Sync Works

When two-way sync is enabled:

| Action in Catchify           | Result in Jira                                              |
| ---------------------------- | ----------------------------------------------------------- |
| Finding marked as Open       | Jira ticket created (if auto-create is on)                  |
| Finding moved to In Progress | Jira ticket status updated to your "In Progress" equivalent |
| Finding moved to Fixed       | Jira ticket status updated to your "Done" equivalent        |

| Action in Jira              | Result in Catchify                    |
| --------------------------- | ------------------------------------- |
| Ticket moved to In Progress | Finding status updated to In Progress |
| Ticket moved to Done        | Finding status updated to Fixed       |

## Managing the Integration

After setup, you can:

* **Edit configuration** -- Change field mappings, sync options, or the target Jira project
* **View sync history** -- See a log of all tickets created and status updates synced
* **Pause sync** -- Temporarily stop syncing without disconnecting the integration
* **Disconnect** -- Remove the Jira integration entirely

{% hint style="warning" %}
If your Jira project workflow changes (for example, new status names or fields), you may need to update the field mapping in Catchify to keep the sync working correctly.
{% endhint %}

## Tips for a Smooth Integration

* **Use a dedicated Jira project** -- Consider creating a "Security Findings" project in Jira specifically for Catchify tickets, so they do not get lost among other work
* **Set up Jira notifications** -- Configure Jira to notify the right developers when new security tickets are created
* **Track resolution time** -- Use Jira's built-in reporting to track how quickly your team resolves security findings
* **Include in sprint planning** -- Make security findings part of your regular sprint planning to ensure they get addressed consistently

{% hint style="success" %}
Teams using the Jira integration resolve findings faster because developers receive tickets in the tool they already use every day. No context-switching required.
{% endhint %}


# Webhook Notifications

Webhooks allow Catchify to send real-time notifications to any system that can receive HTTP requests. This is useful if you want to integrate Catchify with custom tools, internal dashboards, ticketing systems, or communication platforms beyond Slack and Jira.

## What Are Webhooks?

A webhook is a way for Catchify to automatically send information to another system when something happens -- like a new finding being discovered or a report being submitted. Instead of your system checking Catchify for updates, Catchify pushes updates to your system as they occur.

## Setting Up a Webhook

1. Navigate to **Integrations** in the main menu
2. Find the **Webhooks** card and click **Configure**
3. Click **Add Webhook**
4. Enter the following details:
   * **URL** -- The endpoint where Catchify should send notifications (provided by your receiving system)
   * **Name** -- A friendly name for this webhook (for example, "Internal Dashboard" or "ServiceNow Integration")
   * **Events** -- Select which events should trigger this webhook
5. Click **Save**

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-webhooks.png?alt=media" alt="Webhook configuration form with URL, name, and event selection"><figcaption><p>Add a webhook by providing a URL and selecting which events to send</p></figcaption></figure>

## Available Events

You can configure your webhook to send notifications for any combination of these events:

| Event                 | When It Fires                                 |
| --------------------- | --------------------------------------------- |
| **finding.created**   | A new finding is discovered                   |
| **finding.updated**   | A finding's status or details change          |
| **report.created**    | A new bug bounty report is submitted          |
| **report.updated**    | A bug bounty report status changes            |
| **retest.completed**  | A retest has been completed                   |
| **project.started**   | A penetration testing engagement begins       |
| **project.completed** | A penetration testing engagement finishes     |
| **comment.created**   | A new comment is added to a finding or report |

## What Gets Sent

When an event occurs, Catchify sends an HTTP POST request to your webhook URL. The request includes a JSON body with details about the event, such as:

* The event type
* A timestamp
* Key details about the finding, report, or project that triggered the event
* A link to view the full details in the Catchify portal

{% hint style="info" %}
Your technical team can use the event data to build custom workflows -- for example, automatically creating tickets in a custom ticketing system, updating a security dashboard, or triggering alerts in a monitoring tool.
{% endhint %}

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-webhooks.png?alt=media" alt="Webhook delivery log showing recent events with status and response codes"><figcaption><p>The delivery log shows the status of every webhook notification sent</p></figcaption></figure>

## Securing Your Webhooks

To ensure that webhook notifications are genuinely from Catchify (and not from a malicious source), each webhook request includes an HMAC signature in the request headers. Your receiving system can verify this signature to confirm the request is authentic.

When you create a webhook, Catchify generates a **signing secret** that is displayed once. Share this secret with your technical team so they can configure signature verification on the receiving end.

{% hint style="warning" %}
Store your webhook signing secret securely. If you lose it, you can regenerate a new one from the webhook settings -- but you will need to update your receiving system with the new secret.
{% endhint %}

## Managing Your Webhooks

From the Webhooks configuration page, you can:

* **View delivery history** -- See a log of all notifications sent, including response codes from your endpoint
* **Edit a webhook** -- Change the URL, name, or selected events
* **Test a webhook** -- Send a test event to verify your endpoint is working
* **Disable a webhook** -- Temporarily stop sending notifications without deleting the configuration
* **Delete a webhook** -- Permanently remove the webhook

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-webhooks.png?alt=media" alt="Webhook list showing configured webhooks with edit and delete options"><figcaption><p>Manage all your webhooks from one page</p></figcaption></figure>

## Troubleshooting

If your webhook notifications are not arriving:

* **Check the delivery log** -- Look for error response codes that indicate what went wrong
* **Verify the URL** -- Make sure the webhook URL is correct and publicly accessible
* **Check your firewall** -- Ensure your receiving system allows incoming requests from external sources
* **Review the endpoint** -- Make sure your endpoint returns a 200 status code to acknowledge receipt

If deliveries fail repeatedly, Catchify will automatically disable the webhook after a number of consecutive failures. You will see a notification in the portal when this happens.

{% hint style="success" %}
Webhooks are the most flexible way to integrate Catchify with your existing tools and workflows. If you can receive an HTTP request, you can integrate with Catchify.
{% endhint %}


# VDP Widget

A Vulnerability Disclosure Policy (VDP) is a public page on your website that tells security researchers how to responsibly report vulnerabilities they find in your systems. Catchify provides an embeddable widget that makes it easy to add a professional, branded VDP page to your website in minutes.

## What is a VDP?

A Vulnerability Disclosure Policy publicly communicates that your organization:

* Welcomes responsible security research
* Has a clear process for receiving and handling vulnerability reports
* Will not take legal action against researchers who follow the policy
* Is committed to maintaining secure systems

Many international standards and regulations (including ISO 27001 and SAMA guidelines) recommend or require organizations to have a VDP in place.

{% hint style="info" %}
A VDP is different from a bug bounty program. A VDP is a policy for responsible disclosure -- it does not necessarily involve financial rewards. However, the two can work together: your VDP can direct researchers to your Catchify bug bounty program.
{% endhint %}

## Setting Up the VDP Widget

### Step 1: Configure Your Policy

1. Navigate to **Integrations** in the main menu
2. Find the **VDP Widget** card and click **Configure**
3. Customize your policy settings:
   * **Organization name** -- Your company name as it should appear on the widget
   * **Contact email** -- The email address for vulnerability reports (you can use your Catchify support email)
   * **Scope** -- Describe which systems are in scope for reporting
   * **Response commitment** -- How quickly you commit to acknowledging reports (for example, "within 3 business days")
   * **Safe harbor statement** -- A statement protecting researchers who follow your policy

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-vdp.png?alt=media" alt="VDP widget configuration page with organization name, email, and scope fields"><figcaption><p>Customize your VDP policy details</p></figcaption></figure>

### Step 2: Customize Appearance

You can customize the look of the widget to match your website:

* **Theme** -- Choose between light and dark themes
* **Accent color** -- Match your brand color
* **Position** -- Choose where the widget appears on your page (embedded or floating button)

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-vdp.png?alt=media" alt="Widget appearance settings showing theme, color, and position options"><figcaption><p>Match the widget to your website's look and feel</p></figcaption></figure>

### Step 3: Add the Widget to Your Website

After configuring your policy and appearance, Catchify will provide a small code snippet to add to your website. Share this snippet with your web development team and ask them to add it to the appropriate page (usually your security page or footer).

The snippet is a single line that loads the widget -- your development team will know what to do with it.

{% hint style="success" %}
The widget is hosted by Catchify, so it always stays up to date. If you change your policy settings in the portal, the widget on your website updates automatically -- no code changes needed.
{% endhint %}

## What Visitors See

When someone visits your VDP page, they see:

* Your organization name and branding
* The scope of systems covered by the policy
* Clear instructions on how to submit a report
* Your response time commitment
* The safe harbor statement
* A submission form for reporting vulnerabilities

Reports submitted through the VDP widget are routed through Catchify and appear in your portal alongside your bug bounty reports, so you can manage everything in one place.

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-9e4e0d1bf53f6267d13bff58f533223cee60cbfb%2Fintegrations-vdp.png?alt=media" alt="VDP widget as seen by a visitor on the company website"><figcaption><p>A clean, professional vulnerability disclosure page on your website</p></figcaption></figure>

## Benefits of a VDP Widget

| Benefit                       | Description                                                                                 |
| ----------------------------- | ------------------------------------------------------------------------------------------- |
| **Professional presentation** | Shows security researchers that your organization takes security seriously                  |
| **Centralized management**    | Reports come through Catchify alongside your other security findings                        |
| **Compliance**                | Helps meet regulatory requirements for responsible disclosure policies                      |
| **Easy maintenance**          | Update your policy from the Catchify portal -- changes appear on your website automatically |
| **Branding**                  | Customizable appearance matches your website design                                         |

## Managing Your VDP

After setup, you can update your policy at any time from the Integrations page:

* **Edit policy text** -- Update scope, response commitments, or contact information
* **Change appearance** -- Adjust colors, theme, or positioning
* **View submissions** -- Reports from the VDP widget appear in your Bug Bounty reports section
* **Disable widget** -- Temporarily hide the widget from your website

{% hint style="warning" %}
If you disable the VDP widget, the code snippet on your website will show nothing. Remember to remove the snippet from your website if you no longer want the widget, or re-enable it in the portal to make it visible again.
{% endhint %}


# Getting Help

The Catchify team is here to support you at every stage -- from setting up your account to managing ongoing security programs. Whether you have a quick question or need help resolving a complex issue, there are several ways to get assistance.

## Contact Your Account Manager

Every Catchify client has a dedicated account manager who serves as your main point of contact. Your account manager can help with:

* Setting up new penetration testing engagements
* Launching or adjusting your bug bounty program
* Understanding findings and prioritizing remediation
* Answering questions about quotes, invoices, and payments
* Coordinating with the Catchify technical team on your behalf

Your account manager's contact details are available in your portal settings. Do not hesitate to reach out -- they are there to help.

## Email Support

For general questions, technical issues, or requests, email us at:

**<info@catchify.sa>**

Our support team monitors this inbox during business hours (Sunday through Thursday, 9:00 AM to 6:00 PM, Saudi Arabia time) and aims to respond within one business day.

When contacting support, include the following to help us resolve your issue quickly:

* Your name and organization
* A description of the issue or question
* Any relevant screenshots or error messages
* The URL of the page where you encountered the issue (if applicable)

{% hint style="info" %}
For urgent issues related to active penetration testing engagements or critical security matters, contact your account manager directly for the fastest response.
{% endhint %}

## In-Portal Notifications

Catchify keeps you informed through the notification system built into the portal:

* The **notification bell** in the top-right corner shows unread notifications
* Click the bell to see recent updates about your projects, findings, and reports
* Click any notification to go directly to the relevant page

<figure><img src="https://1934022057-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FSEbSDqwQ0dOF3yycuHLw%2Fuploads%2Fgit-blob-a25ab26e9f3ccbdbdc2a11f6c3395f109c3ad18b%2Fnotifications-page.png?alt=media" alt="Portal header showing the notification bell with unread count badge"><figcaption><p>Check the notification bell for the latest updates on your account</p></figcaption></figure>

Notifications cover events such as:

* New findings discovered in your projects
* Status changes on findings and reports
* Retest results
* New invoices and quotes
* Team member activity

## Adding Comments in the Portal

For questions about specific findings or reports, the fastest way to communicate is through the commenting system:

1. Open the finding or report you have a question about
2. Scroll to the **Comments** section
3. Type your question or note
4. Click **Add Comment**

The Catchify team monitors comments on active engagements and will respond directly in the portal. This keeps all communication in context and easy to reference later.

## Documentation

This guide covers all aspects of the client portal. Use the table of contents to navigate to the topic you need help with. Here are some commonly referenced pages:

* [Logging In](/catchify-platform-documentation/getting-started/logging-in) -- Trouble accessing your account
* [Understanding Findings](/catchify-platform-documentation/penetration-testing/understanding-findings) -- How to read and manage findings
* [Requesting a Retest](/catchify-platform-documentation/penetration-testing/requesting-retest) -- How to verify your fixes
* [Roles & Permissions](/catchify-platform-documentation/team-management/roles-and-permissions) -- Managing team access
* [FAQ](/catchify-platform-documentation/support/faq) -- Answers to the most common questions

## Feedback

We are always looking to improve the Catchify platform and your experience as a client. If you have suggestions, feature requests, or feedback, we would love to hear from you:

* Tell your account manager during your regular check-ins
* Email feedback to <info@catchify.sa> with "Feedback" in the subject line
* Add comments in the portal on specific areas where you would like to see improvements

{% hint style="success" %}
Your feedback directly shapes the Catchify product roadmap. Many of our most popular features were suggested by clients like you.
{% endhint %}


# FAQ

Here are answers to the questions we hear most often from Catchify clients. If your question is not covered here, contact your account manager or email <support@catchify.sa>.

***

## Account & Access

### I did not receive my invitation email. What should I do?

Check your spam or junk folder first. If you still cannot find it, ask the team manager who sent the invitation to resend it from the Team page. If the problem persists, contact <support@catchify.sa>.

### I forgot my password. How do I reset it?

Go to [portal.catchify.sa](https://portal.catchify.sa), click **Forgot Password?**, and enter your email address. You will receive a link to set a new password. The link expires after 1 hour, so use it promptly.

### My account seems to be locked. What happened?

For security, accounts are temporarily locked after multiple failed login attempts. Wait a few minutes and try again. If you are still unable to log in, contact <support@catchify.sa> for assistance.

### I lost access to my authenticator app for 2FA. How do I get back in?

Contact the Catchify support team at <support@catchify.sa>. After verifying your identity, we will reset your two-factor authentication so you can set it up again on a new device.

### Can I change the email address on my account?

Contact your account manager to request an email change. For security, email changes require identity verification.

***

## Findings & Vulnerabilities

### What is a finding?

A finding is a security vulnerability or weakness discovered during penetration testing or through your bug bounty program. Each finding includes a description, severity level, evidence, and recommendations for fixing the issue. See [Understanding Findings](/catchify-platform-documentation/penetration-testing/understanding-findings) for details.

### What do the severity levels mean?

Findings are rated from Critical (most severe) to Informational (least severe). Critical findings represent immediate threats, while Informational findings are best-practice recommendations. See [Severity Levels Explained](/catchify-platform-documentation/penetration-testing/severity-levels) for a full breakdown.

### How quickly should I fix a finding?

We recommend addressing Critical findings within 24-48 hours, High findings within 1-2 weeks, and Medium findings within a month. Low and Informational findings can be addressed in regular development cycles. These are guidelines -- your account manager can help you prioritize based on your specific context.

### Can I dispute or discuss a finding's severity?

Yes. Add a comment to the finding explaining your perspective, or contact your account manager. The Catchify team is open to reviewing severity assessments based on your business context and environment.

### What does "Accepted Risk" mean?

When you mark a finding as Accepted Risk, it means your organization has acknowledged the vulnerability but has decided not to fix it at this time -- perhaps because the risk is mitigated by other controls, or the cost of fixing outweighs the risk. The finding remains documented for future reference.

***

## Penetration Testing

### How long does a typical pentest take?

It depends on the scope. A focused web application test might take 1-2 weeks, while a comprehensive assessment of multiple systems could take 3-4 weeks. Your account manager will provide a timeline when your quote is prepared.

### Can I see findings during the test, or only after it is complete?

You can see findings in real time as they are discovered. You do not need to wait for the final report to start reviewing and addressing issues.

### How do I request a retest after fixing a vulnerability?

Open the finding, change its status to Fixed, and click **Request Retest**. The Catchify team will verify your fix, usually within 1-3 business days. See [Requesting a Retest](/catchify-platform-documentation/penetration-testing/requesting-retest) for step-by-step instructions.

### Where do I download my pentest report?

Go to **Projects**, click on the completed project, and navigate to the **Reports** tab. Click **Download PDF** to save the report. See [Pentest Reports](/catchify-platform-documentation/penetration-testing/reports) for more details.

***

## Bug Bounty

### What is the difference between a pentest and a bug bounty program?

A penetration test is a time-bound, structured engagement where our team tests your applications during a defined period. A bug bounty program is ongoing -- researchers continuously test your applications, and you only pay for valid findings. Many organizations use both for comprehensive coverage.

### Who are the researchers testing my applications?

Catchify's researchers go through an identity verification and screening process before joining the platform. Your bug bounty program is private -- only vetted, invited researchers can see and participate.

### How are duplicate reports handled?

The Catchify triage team reviews all reports before they reach you. If a researcher submits a vulnerability that has already been reported by someone else, it is marked as a duplicate and does not appear in your review queue.

### How do I fund researcher rewards?

You add credits to your bug bounty wallet, and rewards are deducted automatically when reports are approved. See [Wallet & Payments](/catchify-platform-documentation/quotes-and-invoices/wallet-and-payments) for details.

***

## Invoices & Payments

### How do I view and download my invoices?

Navigate to **Invoices** in the main menu. Click any invoice to view its details, and click **Download PDF** to save a copy. See [Your Invoices](/catchify-platform-documentation/quotes-and-invoices/your-invoices) for details.

### Are invoices ZATCA-compliant?

Yes. All Catchify invoices are generated in compliance with ZATCA (Zakat, Tax and Customs Authority) regulations, including proper VAT calculation and required formatting.

### What payment methods do you accept?

Catchify accepts bank transfers and wire transfers. Payment instructions are included on each invoice. Contact your account manager if you need alternative arrangements.

***

## Team & Access

### How many team members can I add?

There is no limit. You can invite as many team members as needed to your Catchify account.

### What is the difference between a Manager and a Member?

Managers have full access to everything in the portal. Members have customizable permissions -- you can choose exactly what they can see and do. See [Roles & Permissions](/catchify-platform-documentation/team-management/roles-and-permissions) for details.

### Can I remove a team member's access?

Yes. Go to the **Team** page, find the member, and click **Remove**. Their access will be revoked immediately.

***

## Data & Security

### Where is my data stored?

All Catchify data is hosted in Dammam, Saudi Arabia, ensuring your information stays within the Kingdom and meets local data residency requirements.

### Is my data encrypted?

Yes. All data is encrypted in transit (using TLS/SSL) and at rest. The Catchify platform follows industry best practices for data protection.

### Who can see my findings and reports?

Only authorized members of your organization can see your data. The Catchify team has access for the purpose of providing testing and support services. Your data is never shared with other clients.

***

## Still Have Questions?

If your question was not answered here, we are happy to help:

* **Email:** <support@catchify.sa>
* **Account Manager:** Check your portal settings for contact details

{% hint style="info" %}
We update this FAQ regularly based on the questions we receive. If you asked a question that you think would help other clients, let us know and we may add it here.
{% endhint %}